Designing agent handoffs that do not lose authorization context addresses one concrete problem: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. The guide works from the actual objects — handoff, authorization context, RunContext, history filter, specialist agent — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: handoff meets authorization context
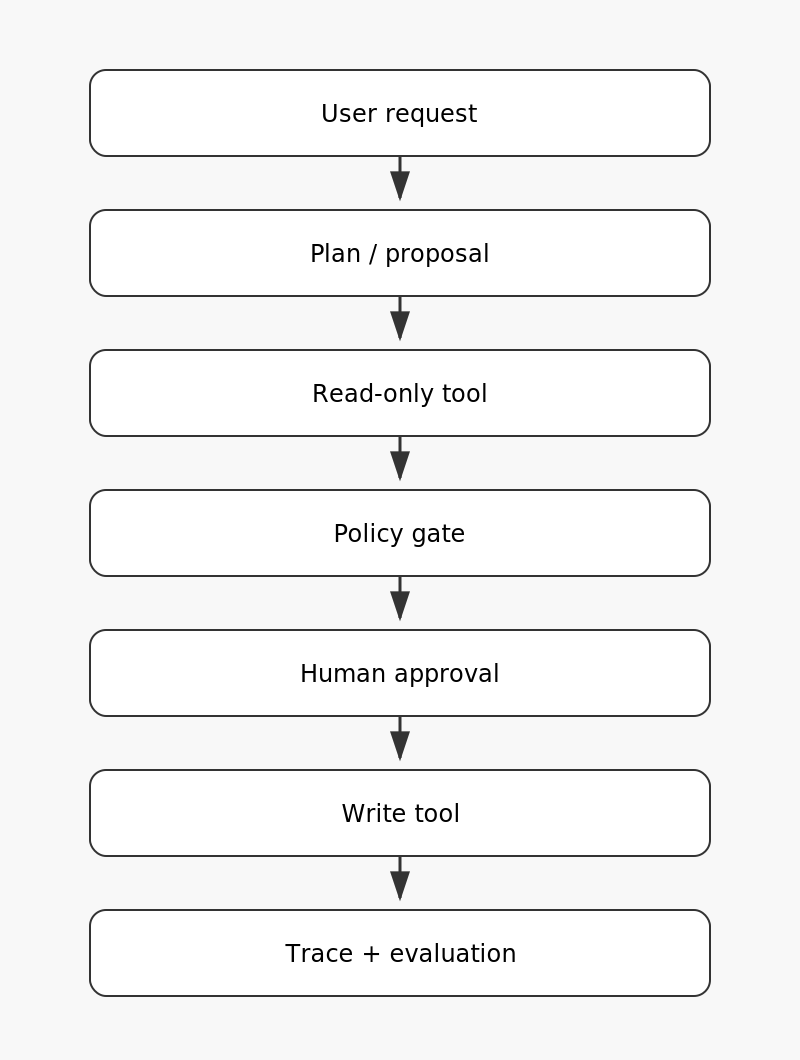
A robust implementation separates what the model proposes from what the application authorizes and verifies.
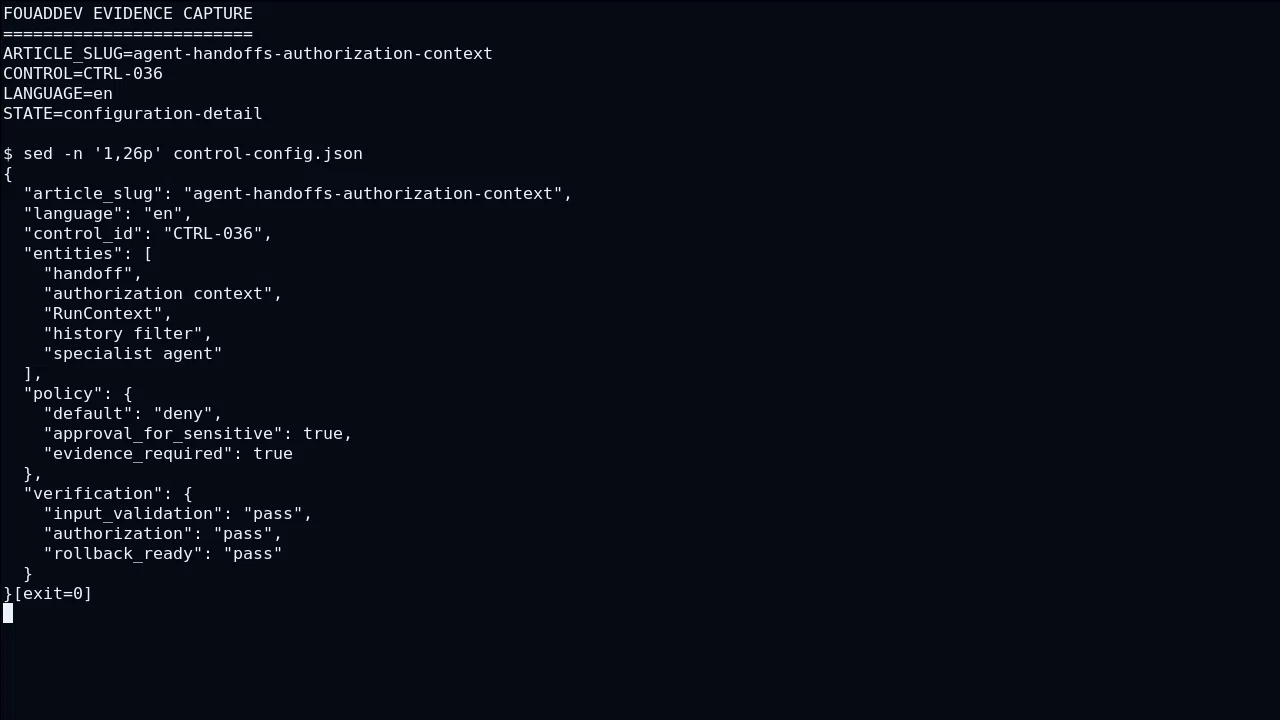
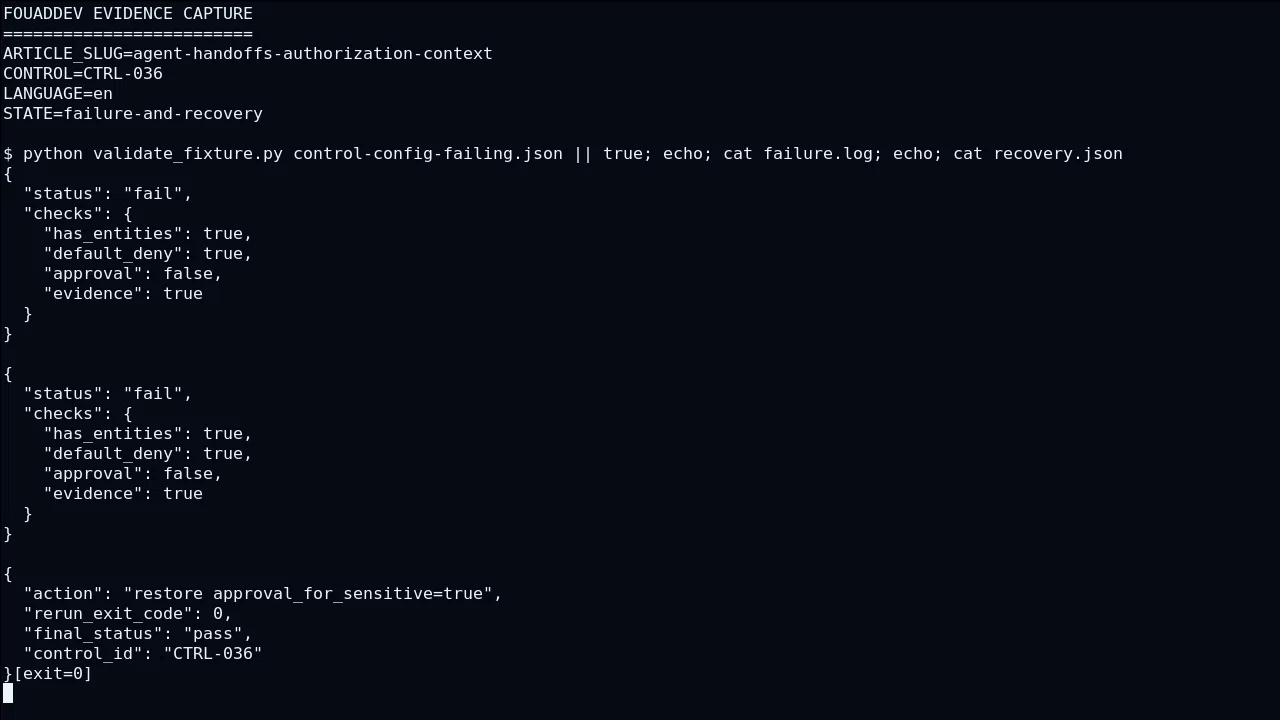
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c11 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. To test authorization context, fixture agent-handoffs-authorization-context-c11 contains both an allowed state and a rejected state; rejection must occur before any change attributed to RunContext. Operations then observes the transition between RunContext and history filter, while security checks that specialist agent receives neither implicit authority nor unnecessary data. If the history filter verification fails, rollback restores the configuration around specialist agent, replays agent-handoffs-authorization-context-c11, and compares the new state with the control evidence from handoff.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c12 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to RunContext, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by history filter and handoff: anything not demonstrated by scenario agent-handoffs-authorization-context-c12 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns authorization context into a reviewable decision point with a named input and a retained output.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c13 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. To test history filter, fixture agent-handoffs-authorization-context-c13 contains both an allowed state and a rejected state; rejection must occur before any change attributed to specialist agent. Operations then observes the transition between specialist agent and handoff, while security checks that authorization context receives neither implicit authority nor unnecessary data. If the handoff verification fails, rollback restores the configuration around authorization context, replays agent-handoffs-authorization-context-c13, and compares the new state with the control evidence from RunContext.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c14 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to specialist agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by handoff and RunContext: anything not demonstrated by scenario agent-handoffs-authorization-context-c14 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns history filter into a reviewable decision point with a named input and a retained output.

Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c21 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns authorization context into a reviewable decision point with a named input and a retained output. To test RunContext, fixture agent-handoffs-authorization-context-c21 contains both an allowed state and a rejected state; rejection must occur before any change attributed to history filter. Operations then observes the transition between history filter and specialist agent, while security checks that handoff receives neither implicit authority nor unnecessary data.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c22 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. If the handoff verification fails, rollback restores the configuration around authorization context, replays agent-handoffs-authorization-context-c22, and compares the new state with the control evidence from RunContext. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to history filter, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by specialist agent and authorization context: anything not demonstrated by scenario agent-handoffs-authorization-context-c22 is labeled as a limitation or inference, never promoted to fact.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c23 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns history filter into a reviewable decision point with a named input and a retained output. To test specialist agent, fixture agent-handoffs-authorization-context-c23 contains both an allowed state and a rejected state; rejection must occur before any change attributed to handoff. Operations then observes the transition between handoff and authorization context, while security checks that RunContext receives neither implicit authority nor unnecessary data.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c24 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. If the RunContext verification fails, rollback restores the configuration around history filter, replays agent-handoffs-authorization-context-c24, and compares the new state with the control evidence from specialist agent. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to handoff, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization context and history filter: anything not demonstrated by scenario agent-handoffs-authorization-context-c24 is labeled as a limitation or inference, never promoted to fact.
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c31 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. The conclusion stays bounded by specialist agent and authorization context: anything not demonstrated by scenario agent-handoffs-authorization-context-c31 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns RunContext into a reviewable decision point with a named input and a retained output. To test history filter, fixture agent-handoffs-authorization-context-c31 contains both an allowed state and a rejected state; rejection must occur before any change attributed to specialist agent.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c32 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. Operations then observes the transition between handoff and authorization context, while security checks that RunContext receives neither implicit authority nor unnecessary data. If the authorization context verification fails, rollback restores the configuration around RunContext, replays agent-handoffs-authorization-context-c32, and compares the new state with the control evidence from history filter. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to specialist agent, a concrete condition, and evidence instead of a generic assurance.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c33 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. The conclusion stays bounded by authorization context and history filter: anything not demonstrated by scenario agent-handoffs-authorization-context-c33 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns specialist agent into a reviewable decision point with a named input and a retained output. To test handoff, fixture agent-handoffs-authorization-context-c33 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization context.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c34 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. Operations then observes the transition between RunContext and history filter, while security checks that specialist agent receives neither implicit authority nor unnecessary data. If the history filter verification fails, rollback restores the configuration around specialist agent, replays agent-handoffs-authorization-context-c34, and compares the new state with the control evidence from handoff. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to authorization context, a concrete condition, and evidence instead of a generic assurance.

Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c41 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to specialist agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by handoff and RunContext: anything not demonstrated by scenario agent-handoffs-authorization-context-c41 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns history filter into a reviewable decision point with a named input and a retained output.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c42 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. To test handoff, fixture agent-handoffs-authorization-context-c42 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization context. Operations then observes the transition between authorization context and RunContext, while security checks that history filter receives neither implicit authority nor unnecessary data. If the RunContext verification fails, rollback restores the configuration around history filter, replays agent-handoffs-authorization-context-c42, and compares the new state with the control evidence from specialist agent.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c43 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to authorization context, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by RunContext and specialist agent: anything not demonstrated by scenario agent-handoffs-authorization-context-c43 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns handoff into a reviewable decision point with a named input and a retained output.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c44 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. To test RunContext, fixture agent-handoffs-authorization-context-c44 contains both an allowed state and a rejected state; rejection must occur before any change attributed to history filter. Operations then observes the transition between history filter and specialist agent, while security checks that handoff receives neither implicit authority nor unnecessary data. If the specialist agent verification fails, rollback restores the configuration around handoff, replays agent-handoffs-authorization-context-c44, and compares the new state with the control evidence from authorization context.

Trust boundaries around RunContext
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c51 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. If the RunContext verification fails, rollback restores the configuration around history filter, replays agent-handoffs-authorization-context-c51, and compares the new state with the control evidence from specialist agent. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to handoff, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization context and history filter: anything not demonstrated by scenario agent-handoffs-authorization-context-c51 is labeled as a limitation or inference, never promoted to fact.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c52 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns handoff into a reviewable decision point with a named input and a retained output. To test authorization context, fixture agent-handoffs-authorization-context-c52 contains both an allowed state and a rejected state; rejection must occur before any change attributed to RunContext. Operations then observes the transition between RunContext and history filter, while security checks that specialist agent receives neither implicit authority nor unnecessary data.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c53 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. If the specialist agent verification fails, rollback restores the configuration around handoff, replays agent-handoffs-authorization-context-c53, and compares the new state with the control evidence from authorization context. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to RunContext, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by history filter and handoff: anything not demonstrated by scenario agent-handoffs-authorization-context-c53 is labeled as a limitation or inference, never promoted to fact.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c54 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns RunContext into a reviewable decision point with a named input and a retained output. To test history filter, fixture agent-handoffs-authorization-context-c54 contains both an allowed state and a rejected state; rejection must occur before any change attributed to specialist agent. Operations then observes the transition between specialist agent and handoff, while security checks that authorization context receives neither implicit authority nor unnecessary data.
Build the decision path with history filter
The starting point is not a feature; it is an observable decision boundary.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c61 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. Operations then observes the transition between RunContext and history filter, while security checks that specialist agent receives neither implicit authority nor unnecessary data. If the history filter verification fails, rollback restores the configuration around specialist agent, replays agent-handoffs-authorization-context-c61, and compares the new state with the control evidence from handoff. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to authorization context, a concrete condition, and evidence instead of a generic assurance.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c62 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. The conclusion stays bounded by history filter and handoff: anything not demonstrated by scenario agent-handoffs-authorization-context-c62 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns authorization context into a reviewable decision point with a named input and a retained output. To test RunContext, fixture agent-handoffs-authorization-context-c62 contains both an allowed state and a rejected state; rejection must occur before any change attributed to history filter.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c63 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. Operations then observes the transition between specialist agent and handoff, while security checks that authorization context receives neither implicit authority nor unnecessary data. If the handoff verification fails, rollback restores the configuration around authorization context, replays agent-handoffs-authorization-context-c63, and compares the new state with the control evidence from RunContext. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to history filter, a concrete condition, and evidence instead of a generic assurance.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c64 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. The conclusion stays bounded by handoff and RunContext: anything not demonstrated by scenario agent-handoffs-authorization-context-c64 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns history filter into a reviewable decision point with a named input and a retained output. To test specialist agent, fixture agent-handoffs-authorization-context-c64 contains both an allowed state and a rejected state; rejection must occur before any change attributed to handoff.

Verify specialist agent with observable evidence
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c71 starts at authorization context and treats RunContext as an explicit boundary rather than an implicit assumption. The first control requires history filter to emit an observable result before specialist agent can trigger the intended effect around handoff. To test RunContext, fixture agent-handoffs-authorization-context-c71 contains both an allowed state and a rejected state; rejection must occur before any change attributed to history filter. Operations then observes the transition between history filter and specialist agent, while security checks that handoff receives neither implicit authority nor unnecessary data. If the specialist agent verification fails, rollback restores the configuration around handoff, replays agent-handoffs-authorization-context-c71, and compares the new state with the control evidence from authorization context.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c72 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to history filter, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by specialist agent and authorization context: anything not demonstrated by scenario agent-handoffs-authorization-context-c72 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns RunContext into a reviewable decision point with a named input and a retained output.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c73 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. To test specialist agent, fixture agent-handoffs-authorization-context-c73 contains both an allowed state and a rejected state; rejection must occur before any change attributed to handoff. Operations then observes the transition between handoff and authorization context, while security checks that RunContext receives neither implicit authority nor unnecessary data. If the authorization context verification fails, rollback restores the configuration around RunContext, replays agent-handoffs-authorization-context-c73, and compares the new state with the control evidence from history filter.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c74 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to handoff, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization context and history filter: anything not demonstrated by scenario agent-handoffs-authorization-context-c74 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns specialist agent into a reviewable decision point with a named input and a retained output.
Evidence point: OWASP documents that the 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. This source anchors verify specialist agent with observable evidence but does not replace local verification. [S7]Controls that remain after launch
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c81 starts at RunContext and treats history filter as an explicit boundary rather than an implicit assumption. The first control requires specialist agent to emit an observable result before handoff can trigger the intended effect around authorization context. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns RunContext into a reviewable decision point with a named input and a retained output. To test history filter, fixture agent-handoffs-authorization-context-c81 contains both an allowed state and a rejected state; rejection must occur before any change attributed to specialist agent. Operations then observes the transition between specialist agent and handoff, while security checks that authorization context receives neither implicit authority nor unnecessary data.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c82 starts at history filter and treats specialist agent as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before authorization context can trigger the intended effect around RunContext. If the authorization context verification fails, rollback restores the configuration around RunContext, replays agent-handoffs-authorization-context-c82, and compares the new state with the control evidence from history filter. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to specialist agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by handoff and RunContext: anything not demonstrated by scenario agent-handoffs-authorization-context-c82 is labeled as a limitation or inference, never promoted to fact.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c83 starts at specialist agent and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires authorization context to emit an observable result before RunContext can trigger the intended effect around history filter. That sequence serves this concrete job: Route to specialists without dropping the user identity, policy decision, or evidence needed to authorize the next tool call. It turns specialist agent into a reviewable decision point with a named input and a retained output. To test handoff, fixture agent-handoffs-authorization-context-c83 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization context. Operations then observes the transition between authorization context and RunContext, while security checks that history filter receives neither implicit authority nor unnecessary data.
In “Designing agent handoffs that do not lose authorization context”, scenario agent-handoffs-authorization-context-c84 starts at handoff and treats authorization context as an explicit boundary rather than an implicit assumption. The first control requires RunContext to emit an observable result before history filter can trigger the intended effect around specialist agent. If the history filter verification fails, rollback restores the configuration around specialist agent, replays agent-handoffs-authorization-context-c84, and compares the new state with the control evidence from handoff. This detail makes “Designing agent handoffs that do not lose authorization context” reviewable because each operational statement points to authorization context, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by RunContext and specialist agent: anything not demonstrated by scenario agent-handoffs-authorization-context-c84 is labeled as a limitation or inference, never promoted to fact.
Evidence point: Kubernetes documents that kubernetes policy objects include NetworkPolicies for traffic controls and admission mechanisms for validating or mutating API requests. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around handoff has an input, a rule, a rejection behavior, and evidence.
- The control around authorization context has an input, a rule, a rejection behavior, and evidence.
- The control around RunContext has an input, a rule, a rejection behavior, and evidence.
- The control around history filter has an input, a rule, a rejection behavior, and evidence.
- The control around specialist agent has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] Agent orchestration - OpenAI Agents SDK — Two common orchestration patterns are manager-controlled agents-as-tools and handoffs where a specialist becomes the active agent. source
- [S2] Authorization - Model Context Protocol — For HTTP authorization, MCP requires resource-bound tokens, server-side audience validation and PKCE, and forbids insecure token passthrough patterns. source
- [S3] REST Security Cheat Sheet — OWASP REST guidance emphasizes HTTPS, explicit access control and careful handling of tokens, methods, inputs and security headers. source
- [S4] Artificial Intelligence Risk Management Framework: Generative AI Profile — NIST AI 600-1 is a generative-AI profile for integrating trustworthiness and risk actions across the AI lifecycle. source
- [S5] AI Risk Management Framework — NIST positions the AI RMF as a voluntary framework for managing AI risks and is revising it while adding profiles for specific settings. source
- [S6] OWASP Top 10 for Large Language Model Applications — OWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. source
- [S7] OWASP Top 10 for LLM Applications 2025 — The 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. source
- [S8] Policies - Kubernetes — Kubernetes policy objects include NetworkPolicies for traffic controls and admission mechanisms for validating or mutating API requests. source
- [S9] Authentication Cheat Sheet — OWASP authentication guidance separates identity proofing, authentication and session management and recommends strong controls for sensitive operations. source
- [S10] Running agents - OpenAI Agents SDK — Run configuration controls model setup, guardrails, handoff behavior, tracing, tool execution and conversation state. source



Comments
No published comment yet.
Sign in to comment