Design idempotent APIs and contracts that survive retries addresses a concrete operating problem: turn intent into verifiable behavior without hiding security, quality, or operational trade-offs. This piece moves from foundations to expert decisions, using order creation protected by an idempotency key as a running example and testing every choice against production constraints.
Objective, expected result, and scope
Design idempotent APIs and contracts that survive retries becomes an engineering problem as soon as the system must remain dependable beyond a demo. The starting point is not the tool but the decision that needs protection: who may act, on which data, under which authority, and how the team can later prove what happened. The central angle here is idempotency and contract evolution. The running example is order creation protected by an idempotency key, which keeps the discussion anchored in a concrete operating situation rather than an abstract architecture.
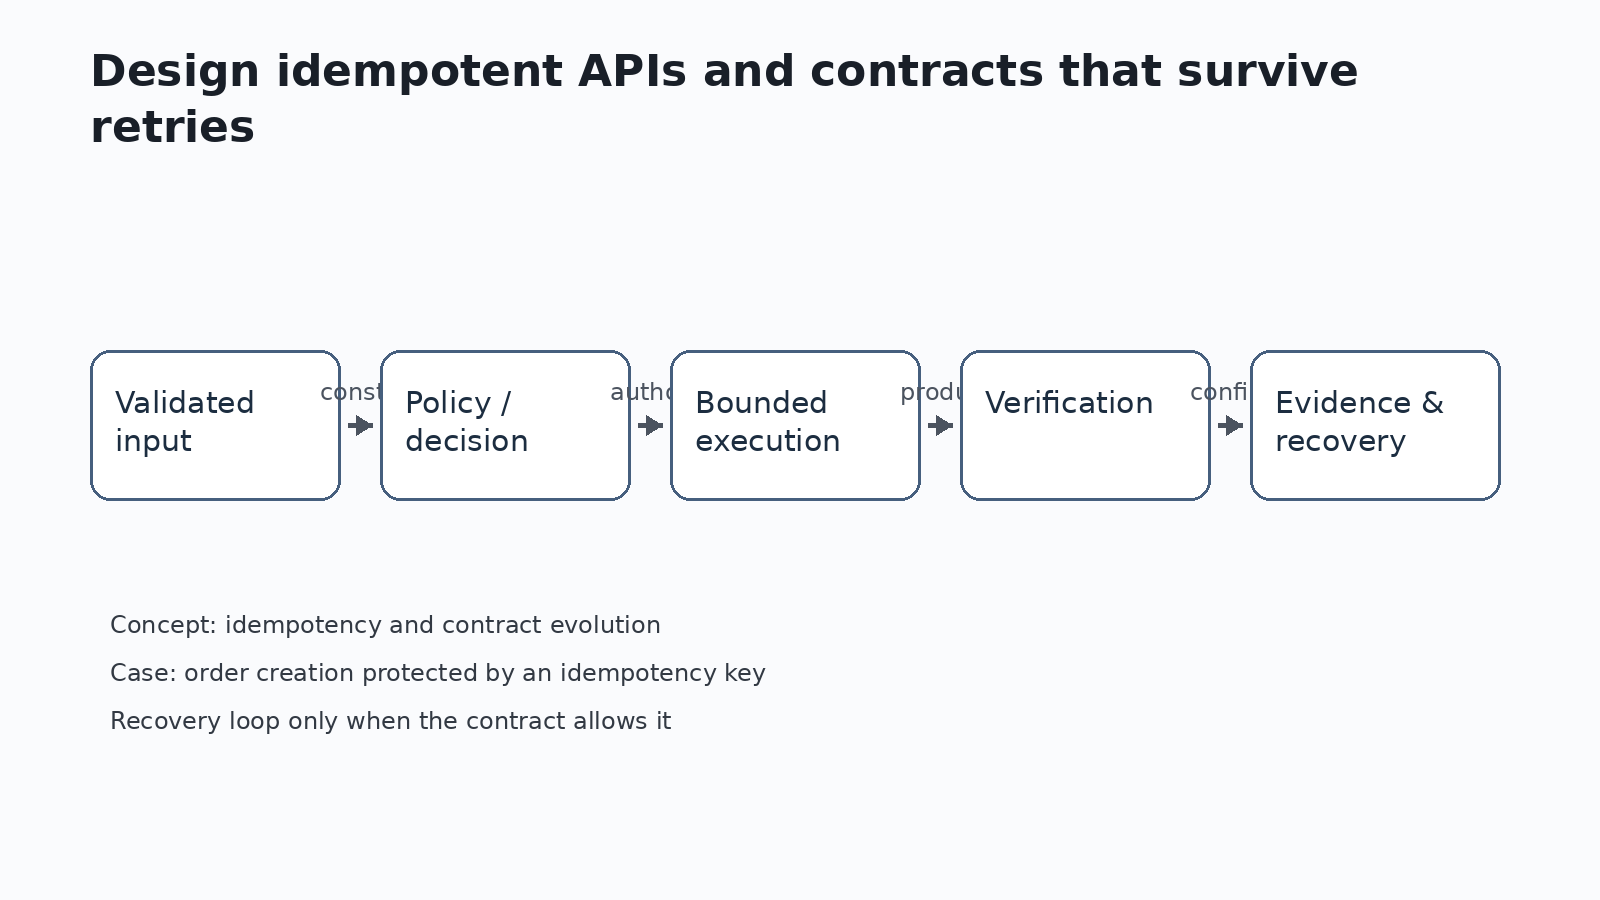
A robust design separates intent, state, execution, and evidence. Intent describes the business outcome; state records what the system actually knows; execution performs a bounded action; evidence makes that action reviewable. In Design idempotent APIs and contracts that survive retries, this separation prevents a local error from becoming a system-wide inconsistency. It also improves testability because every boundary has an observable contract and an identifiable owner.
A beginner needs the nominal flow, but production engineering must examine deviations: ambiguous input, missing data, unavailable dependencies, network retries, duplicates, insufficient permission, or contradictory results. Each case needs an explicit response. The right behavior is not always to retry. Sometimes the safe choice is to refuse, queue, request approval, or preserve state for an idempotent recovery.
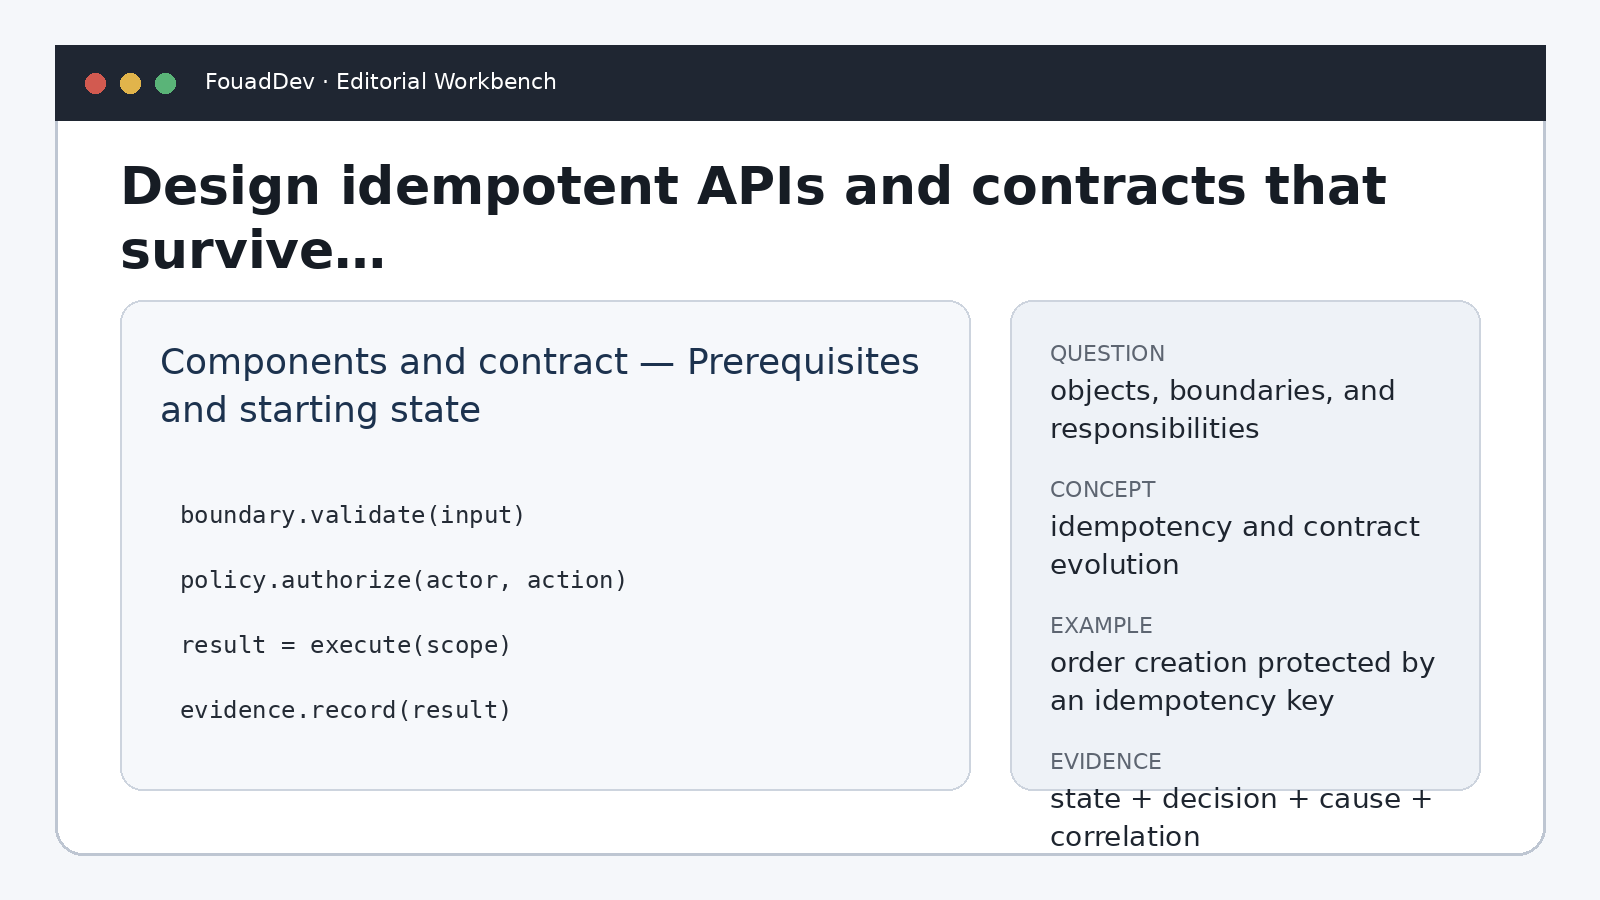
At the intermediate level, those rules become explicit interfaces. Inputs are validated before sensitive components are called; outputs are checked before they are persisted or propagated; external dependencies are wrapped behind stable boundaries. This lowers coupling and makes incremental evolution possible. A team can replace an implementation without rewriting the entire business journey when the contract remains stable and regression-tested.
Prerequisites and starting state
Advanced practice is mostly about observability and risk control. Logs should carry correlation identifiers, the minimum useful context, the decision taken, and the cause of failure without exposing unnecessary sensitive data. Metrics and traces are not substitutes for business reasoning. They should answer operational questions such as where the flow stopped, whether a retry is safe, and which component owns the next action.
In practice, order creation protected by an idempotency key must be testable end to end. Prepare a nominal case, incomplete data, an authorization denial, an unavailable dependency, and a repeated request. Define the expected result before running each test. This turns requirements into evidence and avoids validation that relies only on a screen looking correct or on the absence of an exception.
The main trade-off often sits between immediate simplicity and future controllability. A queue, guardrail, approval gate, or additional layer has a cost. That cost is justified when failures are hard to detect, expensive to reverse, or capable of affecting people, data, or critical operations. Adding components without a matching risk, however, increases the failure surface and cognitive load.
An expert pitfall is to confuse automation with autonomy. Automating a known sequence is different from delegating an open-ended decision. For Design idempotent APIs and contracts that survive retries, define what may execute automatically, what requires a deterministic policy, and what needs human confirmation. That classification should be visible in code, tests, and operating procedures rather than living only in a high-level document.
Expected result. After every important step, the system should expose a verifiable state: explicit success, explicit waiting, or a classified error. No failure should be silently converted into success.
Step 1 — establish boundaries and responsibilities
A production review should therefore look for concrete evidence: versioned contracts, regression tests, error handling, privilege controls, useful logging, a recovery strategy, and a clearly named owner. A feature may look successful in a demonstration and still be unoperable if the team cannot diagnose failure or restore a coherent state.
Quality ultimately shows up in the system's ability to make decisions understandable. An operator should distinguish an intentional refusal from an outage, a waiting state from lost data, and a legitimate retry from a duplicate. That operational legibility is an architectural outcome. It shortens diagnosis and prevents manual fixes from hiding a structural defect.
Design idempotent APIs and contracts that survive retries becomes an engineering problem as soon as the system must remain dependable beyond a demo. The starting point is not the tool but the decision that needs protection: who may act, on which data, under which authority, and how the team can later prove what happened. The central angle here is idempotency and contract evolution. The running example is order creation protected by an idempotency key, which keeps the discussion anchored in a concrete operating situation rather than an abstract architecture.
A robust design separates intent, state, execution, and evidence. Intent describes the business outcome; state records what the system actually knows; execution performs a bounded action; evidence makes that action reviewable. In Design idempotent APIs and contracts that survive retries, this separation prevents a local error from becoming a system-wide inconsistency. It also improves testability because every boundary has an observable contract and an identifiable owner.
Step 2 — implement the nominal path
A beginner needs the nominal flow, but production engineering must examine deviations: ambiguous input, missing data, unavailable dependencies, network retries, duplicates, insufficient permission, or contradictory results. Each case needs an explicit response. The right behavior is not always to retry. Sometimes the safe choice is to refuse, queue, request approval, or preserve state for an idempotent recovery.
At the intermediate level, those rules become explicit interfaces. Inputs are validated before sensitive components are called; outputs are checked before they are persisted or propagated; external dependencies are wrapped behind stable boundaries. This lowers coupling and makes incremental evolution possible. A team can replace an implementation without rewriting the entire business journey when the contract remains stable and regression-tested.
Advanced practice is mostly about observability and risk control. Logs should carry correlation identifiers, the minimum useful context, the decision taken, and the cause of failure without exposing unnecessary sensitive data. Metrics and traces are not substitutes for business reasoning. They should answer operational questions such as where the flow stopped, whether a retry is safe, and which component owns the next action.
In practice, order creation protected by an idempotency key must be testable end to end. Prepare a nominal case, incomplete data, an authorization denial, an unavailable dependency, and a repeated request. Define the expected result before running each test. This turns requirements into evidence and avoids validation that relies only on a screen looking correct or on the absence of an exception.
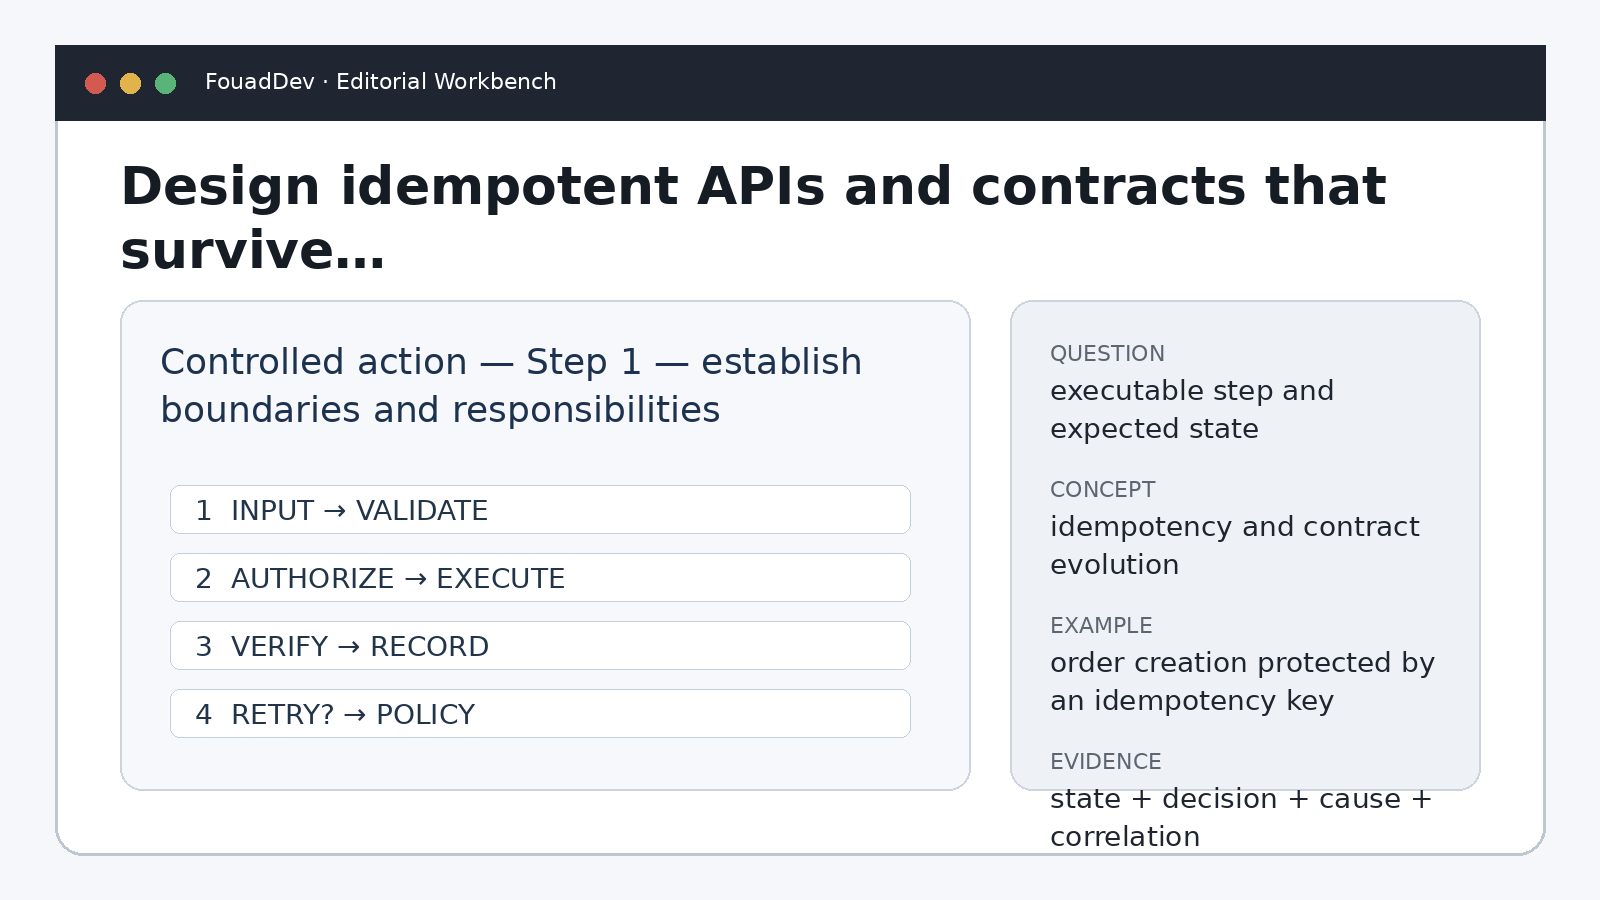
Starting action. Write down the initial state of order creation protected by an idempotency key. List required inputs, the owner of each datum, and the actions that are allowed. Do not implement retries until you can distinguish a new request from a repeated one.
Step 3 — handle errors, retries, and security
The main trade-off often sits between immediate simplicity and future controllability. A queue, guardrail, approval gate, or additional layer has a cost. That cost is justified when failures are hard to detect, expensive to reverse, or capable of affecting people, data, or critical operations. Adding components without a matching risk, however, increases the failure surface and cognitive load.
An expert pitfall is to confuse automation with autonomy. Automating a known sequence is different from delegating an open-ended decision. For Design idempotent APIs and contracts that survive retries, define what may execute automatically, what requires a deterministic policy, and what needs human confirmation. That classification should be visible in code, tests, and operating procedures rather than living only in a high-level document.
A production review should therefore look for concrete evidence: versioned contracts, regression tests, error handling, privilege controls, useful logging, a recovery strategy, and a clearly named owner. A feature may look successful in a demonstration and still be unoperable if the team cannot diagnose failure or restore a coherent state.
Quality ultimately shows up in the system's ability to make decisions understandable. An operator should distinguish an intentional refusal from an outage, a waiting state from lost data, and a legitimate retry from a duplicate. That operational legibility is an architectural outcome. It shortens diagnosis and prevents manual fixes from hiding a structural defect.
Verification and reproducible tests
Design idempotent APIs and contracts that survive retries becomes an engineering problem as soon as the system must remain dependable beyond a demo. The starting point is not the tool but the decision that needs protection: who may act, on which data, under which authority, and how the team can later prove what happened. The central angle here is idempotency and contract evolution. The running example is order creation protected by an idempotency key, which keeps the discussion anchored in a concrete operating situation rather than an abstract architecture.
A robust design separates intent, state, execution, and evidence. Intent describes the business outcome; state records what the system actually knows; execution performs a bounded action; evidence makes that action reviewable. In Design idempotent APIs and contracts that survive retries, this separation prevents a local error from becoming a system-wide inconsistency. It also improves testability because every boundary has an observable contract and an identifiable owner.
A beginner needs the nominal flow, but production engineering must examine deviations: ambiguous input, missing data, unavailable dependencies, network retries, duplicates, insufficient permission, or contradictory results. Each case needs an explicit response. The right behavior is not always to retry. Sometimes the safe choice is to refuse, queue, request approval, or preserve state for an idempotent recovery.
At the intermediate level, those rules become explicit interfaces. Inputs are validated before sensitive components are called; outputs are checked before they are persisted or propagated; external dependencies are wrapped behind stable boundaries. This lowers coupling and makes incremental evolution possible. A team can replace an implementation without rewriting the entire business journey when the contract remains stable and regression-tested.
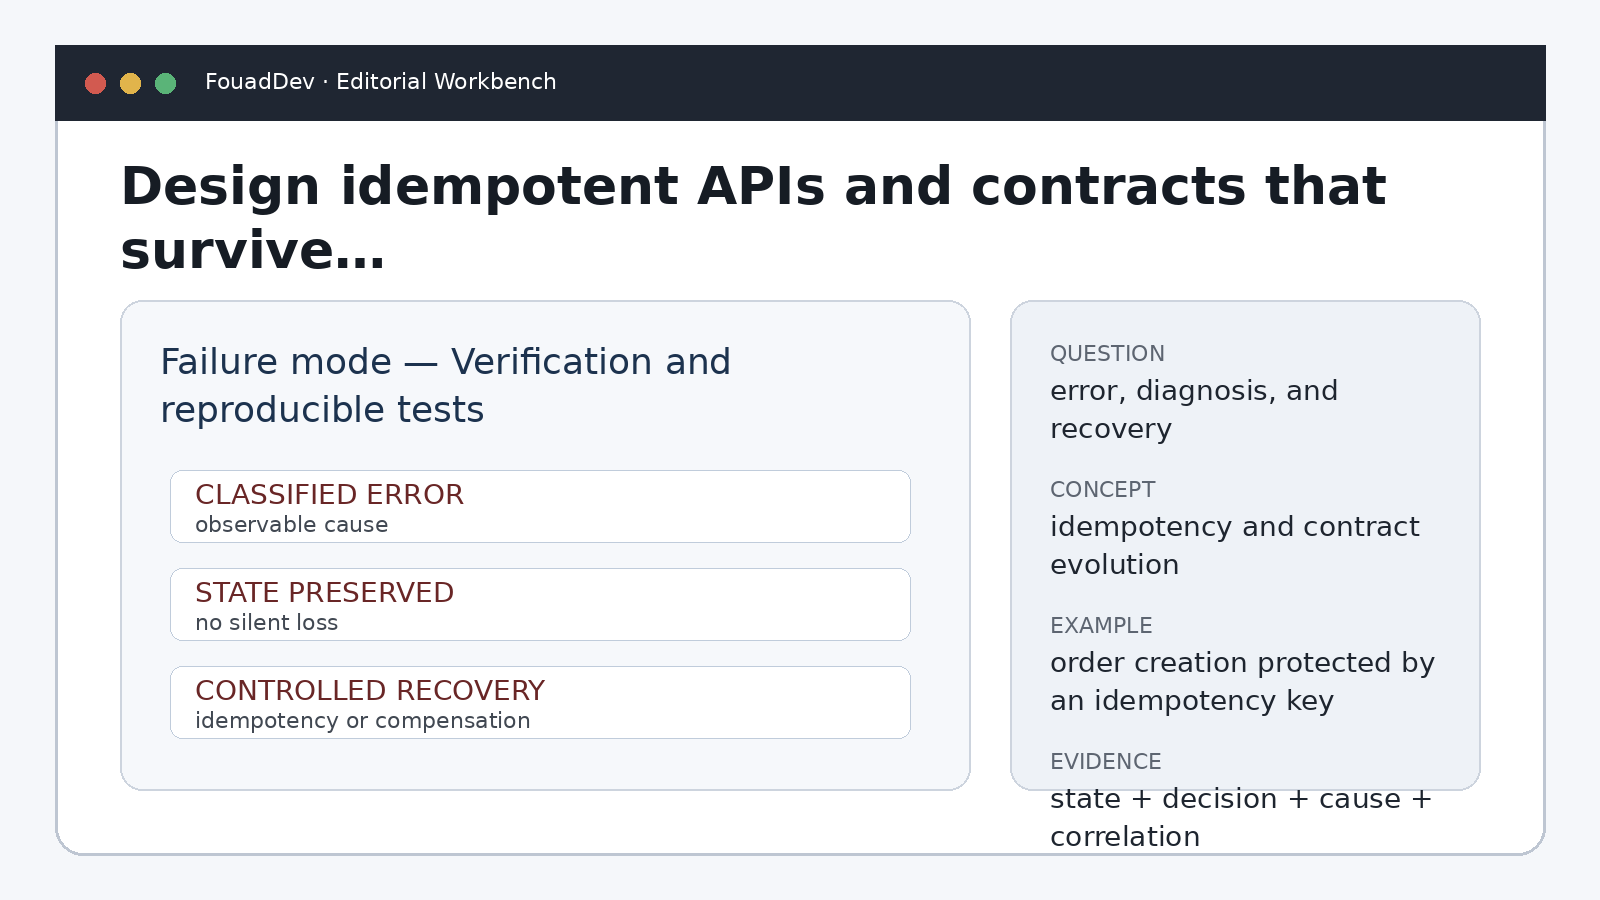
Control test. Repeat the same operation with the same correlation identifier. The business outcome must not be duplicated. Then disable one dependency and verify that state remains coherent.
Troubleshooting frequent failures
Advanced practice is mostly about observability and risk control. Logs should carry correlation identifiers, the minimum useful context, the decision taken, and the cause of failure without exposing unnecessary sensitive data. Metrics and traces are not substitutes for business reasoning. They should answer operational questions such as where the flow stopped, whether a retry is safe, and which component owns the next action.
In practice, order creation protected by an idempotency key must be testable end to end. Prepare a nominal case, incomplete data, an authorization denial, an unavailable dependency, and a repeated request. Define the expected result before running each test. This turns requirements into evidence and avoids validation that relies only on a screen looking correct or on the absence of an exception.
The main trade-off often sits between immediate simplicity and future controllability. A queue, guardrail, approval gate, or additional layer has a cost. That cost is justified when failures are hard to detect, expensive to reverse, or capable of affecting people, data, or critical operations. Adding components without a matching risk, however, increases the failure surface and cognitive load.
An expert pitfall is to confuse automation with autonomy. Automating a known sequence is different from delegating an open-ended decision. For Design idempotent APIs and contracts that survive retries, define what may execute automatically, what requires a deterministic policy, and what needs human confirmation. That classification should be visible in code, tests, and operating procedures rather than living only in a high-level document.
Production hardening
A production review should therefore look for concrete evidence: versioned contracts, regression tests, error handling, privilege controls, useful logging, a recovery strategy, and a clearly named owner. A feature may look successful in a demonstration and still be unoperable if the team cannot diagnose failure or restore a coherent state.
Quality ultimately shows up in the system's ability to make decisions understandable. An operator should distinguish an intentional refusal from an outage, a waiting state from lost data, and a legitimate retry from a duplicate. That operational legibility is an architectural outcome. It shortens diagnosis and prevents manual fixes from hiding a structural defect.
Design idempotent APIs and contracts that survive retries becomes an engineering problem as soon as the system must remain dependable beyond a demo. The starting point is not the tool but the decision that needs protection: who may act, on which data, under which authority, and how the team can later prove what happened. The central angle here is idempotency and contract evolution. The running example is order creation protected by an idempotency key, which keeps the discussion anchored in a concrete operating situation rather than an abstract architecture.
A robust design separates intent, state, execution, and evidence. Intent describes the business outcome; state records what the system actually knows; execution performs a bounded action; evidence makes that action reviewable. In Design idempotent APIs and contracts that survive retries, this separation prevents a local error from becoming a system-wide inconsistency. It also improves testability because every boundary has an observable contract and an identifiable owner.
Expected result. After every important step, the system should expose a verifiable state: explicit success, explicit waiting, or a classified error. No failure should be silently converted into success.
Advanced variations and alternative choices
A beginner needs the nominal flow, but production engineering must examine deviations: ambiguous input, missing data, unavailable dependencies, network retries, duplicates, insufficient permission, or contradictory results. Each case needs an explicit response. The right behavior is not always to retry. Sometimes the safe choice is to refuse, queue, request approval, or preserve state for an idempotent recovery.
At the intermediate level, those rules become explicit interfaces. Inputs are validated before sensitive components are called; outputs are checked before they are persisted or propagated; external dependencies are wrapped behind stable boundaries. This lowers coupling and makes incremental evolution possible. A team can replace an implementation without rewriting the entire business journey when the contract remains stable and regression-tested.
Advanced practice is mostly about observability and risk control. Logs should carry correlation identifiers, the minimum useful context, the decision taken, and the cause of failure without exposing unnecessary sensitive data. Metrics and traces are not substitutes for business reasoning. They should answer operational questions such as where the flow stopped, whether a retry is safe, and which component owns the next action.
In practice, order creation protected by an idempotency key must be testable end to end. Prepare a nominal case, incomplete data, an authorization denial, an unavailable dependency, and a repeated request. Define the expected result before running each test. This turns requirements into evidence and avoids validation that relies only on a screen looking correct or on the absence of an exception.
Control test. Repeat the same operation with the same correlation identifier. The business outcome must not be duplicated. Then disable one dependency and verify that state remains coherent.
Final executable checklist
The main trade-off often sits between immediate simplicity and future controllability. A queue, guardrail, approval gate, or additional layer has a cost. That cost is justified when failures are hard to detect, expensive to reverse, or capable of affecting people, data, or critical operations. Adding components without a matching risk, however, increases the failure surface and cognitive load.
An expert pitfall is to confuse automation with autonomy. Automating a known sequence is different from delegating an open-ended decision. For Design idempotent APIs and contracts that survive retries, define what may execute automatically, what requires a deterministic policy, and what needs human confirmation. That classification should be visible in code, tests, and operating procedures rather than living only in a high-level document.
A production review should therefore look for concrete evidence: versioned contracts, regression tests, error handling, privilege controls, useful logging, a recovery strategy, and a clearly named owner. A feature may look successful in a demonstration and still be unoperable if the team cannot diagnose failure or restore a coherent state.
Quality ultimately shows up in the system's ability to make decisions understandable. An operator should distinguish an intentional refusal from an outage, a waiting state from lost data, and a legitimate retry from a duplicate. That operational legibility is an architectural outcome. It shortens diagnosis and prevents manual fixes from hiding a structural defect.
Starting action. Write down the initial state of order creation protected by an idempotency key. List required inputs, the owner of each datum, and the actions that are allowed. Do not implement retries until you can distinguish a new request from a repeated one.

Comments
No published comment yet.
Sign in to comment