GitHub Actions OIDC to cloud: a credentialless deployment walkthrough addresses one concrete problem: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. The guide works from the actual objects — GitHub Actions, OIDC, audience, subject, cloud role — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: GitHub Actions meets OIDC
The starting point is not a feature; it is an observable decision boundary.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c11 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. Operations then observes the transition between cloud role and GitHub Actions, while security checks that OIDC receives neither implicit authority nor unnecessary data. If the GitHub Actions verification fails, rollback restores the configuration around OIDC, replays github-actions-oidc-cloud-walkthrough-c11, and compares the new state with the control evidence from audience. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to subject, a concrete condition, and evidence instead of a generic assurance.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c12 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. The conclusion stays bounded by GitHub Actions and audience: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c12 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns subject into a reviewable decision point with a named input and a retained output. To test cloud role, fixture github-actions-oidc-cloud-walkthrough-c12 contains both an allowed state and a rejected state; rejection must occur before any change attributed to GitHub Actions.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c13 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. Operations then observes the transition between OIDC and audience, while security checks that subject receives neither implicit authority nor unnecessary data. If the audience verification fails, rollback restores the configuration around subject, replays github-actions-oidc-cloud-walkthrough-c13, and compares the new state with the control evidence from cloud role. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to GitHub Actions, a concrete condition, and evidence instead of a generic assurance.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c14 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. The conclusion stays bounded by audience and cloud role: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c14 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns GitHub Actions into a reviewable decision point with a named input and a retained output. To test OIDC, fixture github-actions-oidc-cloud-walkthrough-c14 contains both an allowed state and a rejected state; rejection must occur before any change attributed to audience.
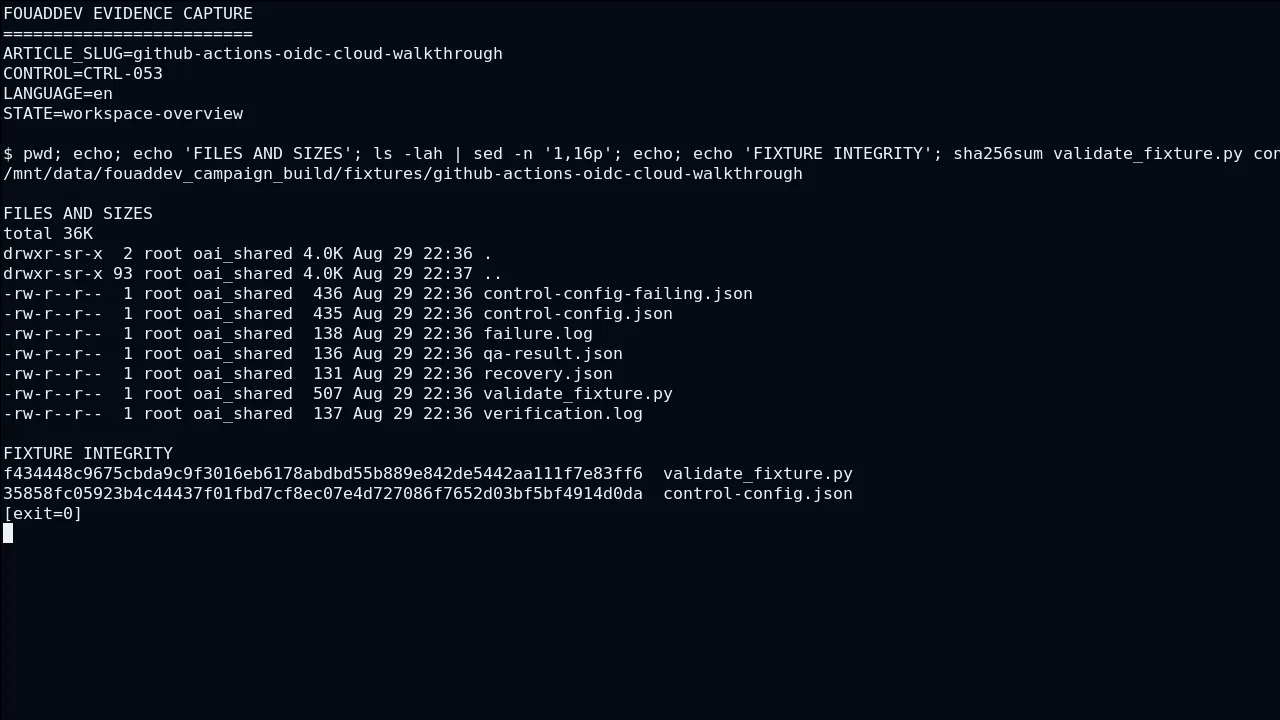
Trust boundaries around audience
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c21 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. To test cloud role, fixture github-actions-oidc-cloud-walkthrough-c21 contains both an allowed state and a rejected state; rejection must occur before any change attributed to GitHub Actions. Operations then observes the transition between GitHub Actions and OIDC, while security checks that audience receives neither implicit authority nor unnecessary data. If the OIDC verification fails, rollback restores the configuration around audience, replays github-actions-oidc-cloud-walkthrough-c21, and compares the new state with the control evidence from subject.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c22 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to GitHub Actions, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OIDC and subject: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c22 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns cloud role into a reviewable decision point with a named input and a retained output.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c23 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. To test OIDC, fixture github-actions-oidc-cloud-walkthrough-c23 contains both an allowed state and a rejected state; rejection must occur before any change attributed to audience. Operations then observes the transition between audience and subject, while security checks that cloud role receives neither implicit authority nor unnecessary data. If the subject verification fails, rollback restores the configuration around cloud role, replays github-actions-oidc-cloud-walkthrough-c23, and compares the new state with the control evidence from GitHub Actions.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c24 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to audience, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by subject and GitHub Actions: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c24 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns OIDC into a reviewable decision point with a named input and a retained output.
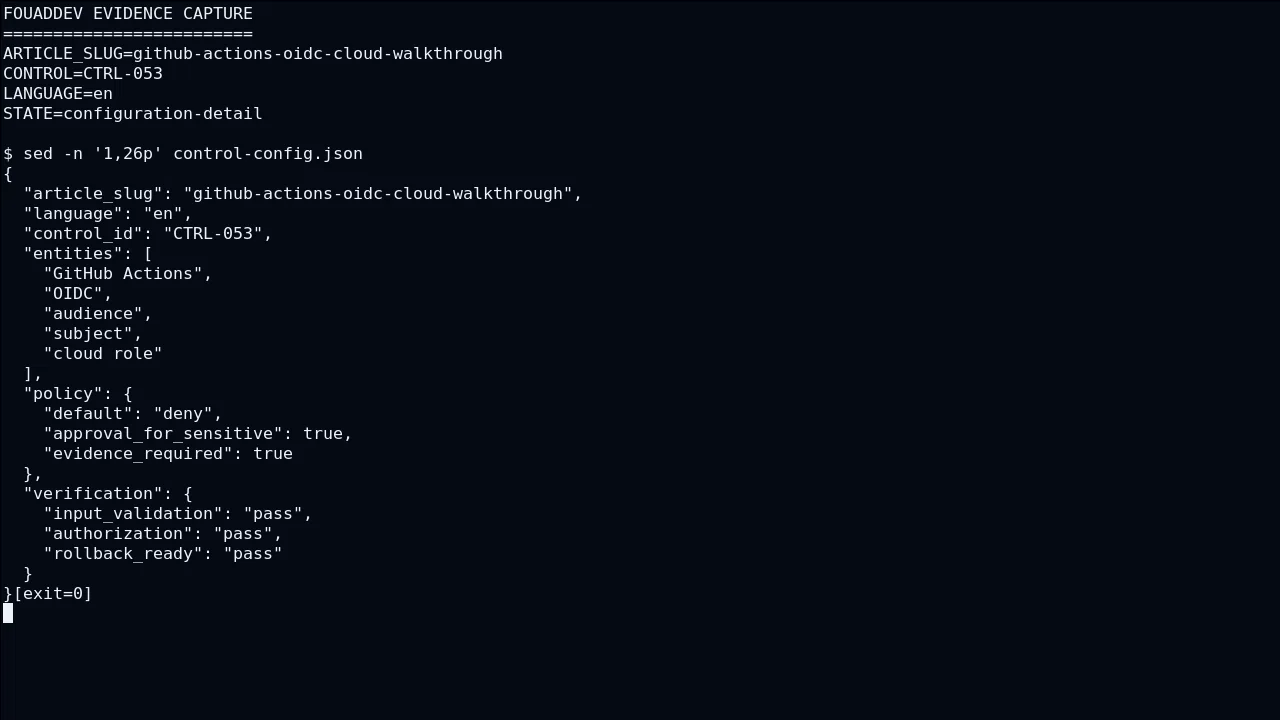
Prepare the starting state and prerequisites
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c31 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns cloud role into a reviewable decision point with a named input and a retained output. To test GitHub Actions, fixture github-actions-oidc-cloud-walkthrough-c31 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OIDC. Operations then observes the transition between OIDC and audience, while security checks that subject receives neither implicit authority nor unnecessary data.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c32 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. If the subject verification fails, rollback restores the configuration around cloud role, replays github-actions-oidc-cloud-walkthrough-c32, and compares the new state with the control evidence from GitHub Actions. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to OIDC, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by audience and cloud role: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c32 is labeled as a limitation or inference, never promoted to fact.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c33 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns OIDC into a reviewable decision point with a named input and a retained output. To test audience, fixture github-actions-oidc-cloud-walkthrough-c33 contains both an allowed state and a rejected state; rejection must occur before any change attributed to subject. Operations then observes the transition between subject and cloud role, while security checks that GitHub Actions receives neither implicit authority nor unnecessary data.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c34 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. If the GitHub Actions verification fails, rollback restores the configuration around OIDC, replays github-actions-oidc-cloud-walkthrough-c34, and compares the new state with the control evidence from audience. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to subject, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by cloud role and OIDC: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c34 is labeled as a limitation or inference, never promoted to fact.
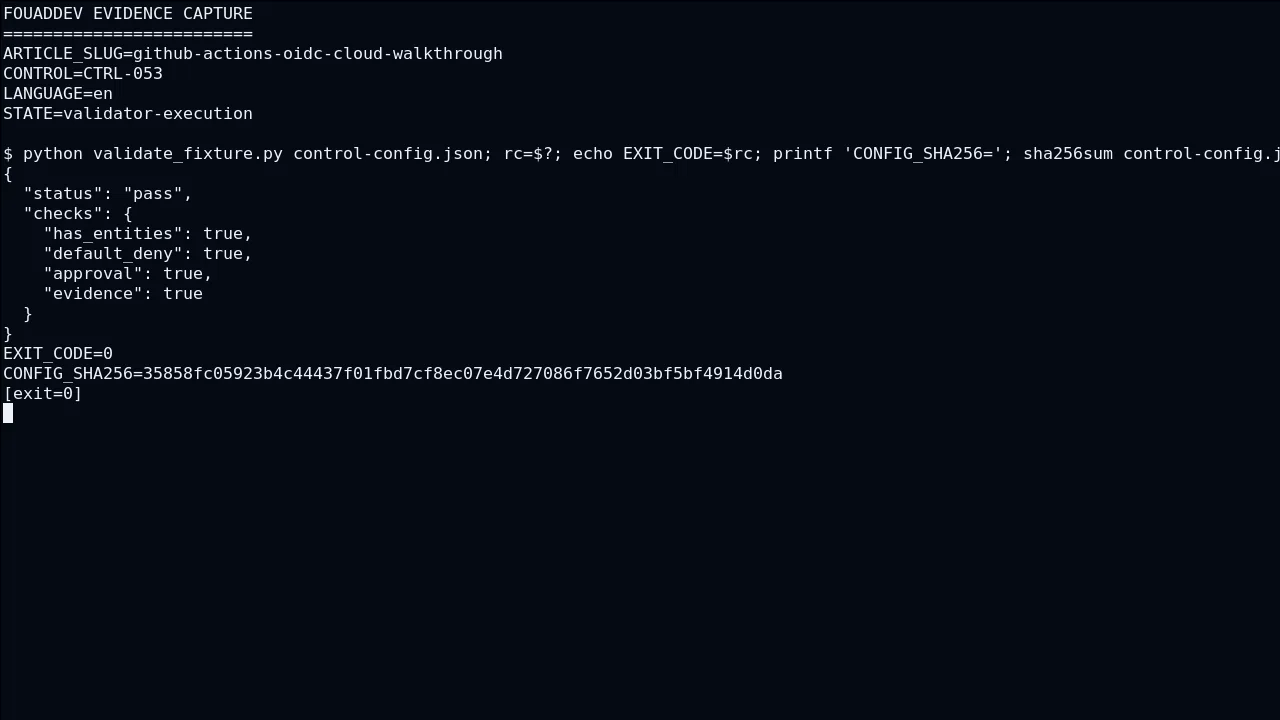
- Step 1 — Configure GitHub Actions, run verification
github-actions-oidc-cloud-walkthrough-step-1, and retain the observable result before continuing. - Step 2 — Configure OIDC, run verification
github-actions-oidc-cloud-walkthrough-step-2, and retain the observable result before continuing. - Step 3 — Configure audience, run verification
github-actions-oidc-cloud-walkthrough-step-3, and retain the observable result before continuing. - Step 4 — Configure subject, run verification
github-actions-oidc-cloud-walkthrough-step-4, and retain the observable result before continuing. - Step 5 — Configure cloud role, run verification
github-actions-oidc-cloud-walkthrough-step-5, and retain the observable result before continuing. - Step 6 — Configure GitHub Actions, run verification
github-actions-oidc-cloud-walkthrough-step-6, and retain the observable result before continuing.
Three failures and fixes
- Input rejected after the side effect: move validation before external execution.
- Missing evidence: log a decision identifier without the secret payload.
- Partial rollback: restore both configuration and authorization, then replay the control fixture.
Execute the procedure and observe the result
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c41 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. The conclusion stays bounded by audience and cloud role: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c41 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns GitHub Actions into a reviewable decision point with a named input and a retained output. To test OIDC, fixture github-actions-oidc-cloud-walkthrough-c41 contains both an allowed state and a rejected state; rejection must occur before any change attributed to audience.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c42 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. Operations then observes the transition between subject and cloud role, while security checks that GitHub Actions receives neither implicit authority nor unnecessary data. If the cloud role verification fails, rollback restores the configuration around GitHub Actions, replays github-actions-oidc-cloud-walkthrough-c42, and compares the new state with the control evidence from OIDC. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to audience, a concrete condition, and evidence instead of a generic assurance.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c43 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. The conclusion stays bounded by cloud role and OIDC: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c43 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns audience into a reviewable decision point with a named input and a retained output. To test subject, fixture github-actions-oidc-cloud-walkthrough-c43 contains both an allowed state and a rejected state; rejection must occur before any change attributed to cloud role.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c44 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. Operations then observes the transition between GitHub Actions and OIDC, while security checks that audience receives neither implicit authority nor unnecessary data. If the OIDC verification fails, rollback restores the configuration around audience, replays github-actions-oidc-cloud-walkthrough-c44, and compares the new state with the control evidence from subject. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to cloud role, a concrete condition, and evidence instead of a generic assurance.
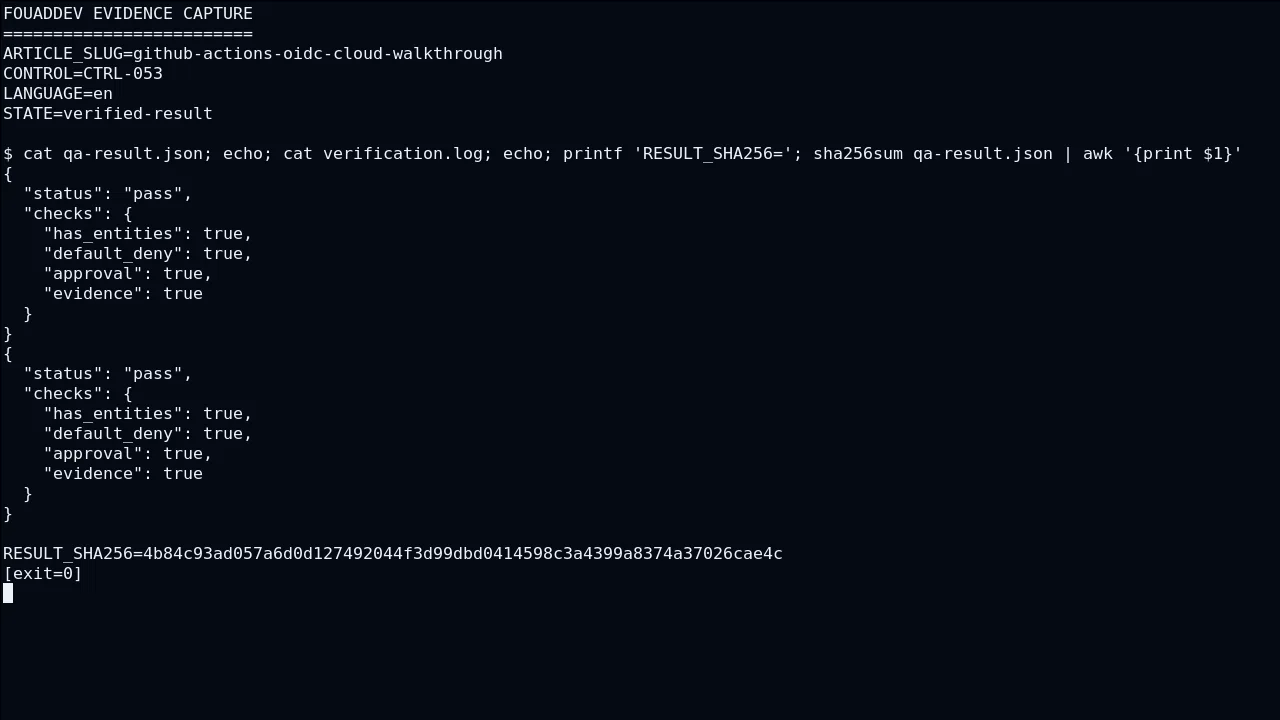
Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c51 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to audience, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by subject and GitHub Actions: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c51 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns OIDC into a reviewable decision point with a named input and a retained output.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c52 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. To test subject, fixture github-actions-oidc-cloud-walkthrough-c52 contains both an allowed state and a rejected state; rejection must occur before any change attributed to cloud role. Operations then observes the transition between cloud role and GitHub Actions, while security checks that OIDC receives neither implicit authority nor unnecessary data. If the GitHub Actions verification fails, rollback restores the configuration around OIDC, replays github-actions-oidc-cloud-walkthrough-c52, and compares the new state with the control evidence from audience.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c53 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to cloud role, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by GitHub Actions and audience: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c53 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns subject into a reviewable decision point with a named input and a retained output.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c54 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. To test GitHub Actions, fixture github-actions-oidc-cloud-walkthrough-c54 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OIDC. Operations then observes the transition between OIDC and audience, while security checks that subject receives neither implicit authority nor unnecessary data. If the audience verification fails, rollback restores the configuration around subject, replays github-actions-oidc-cloud-walkthrough-c54, and compares the new state with the control evidence from cloud role.
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
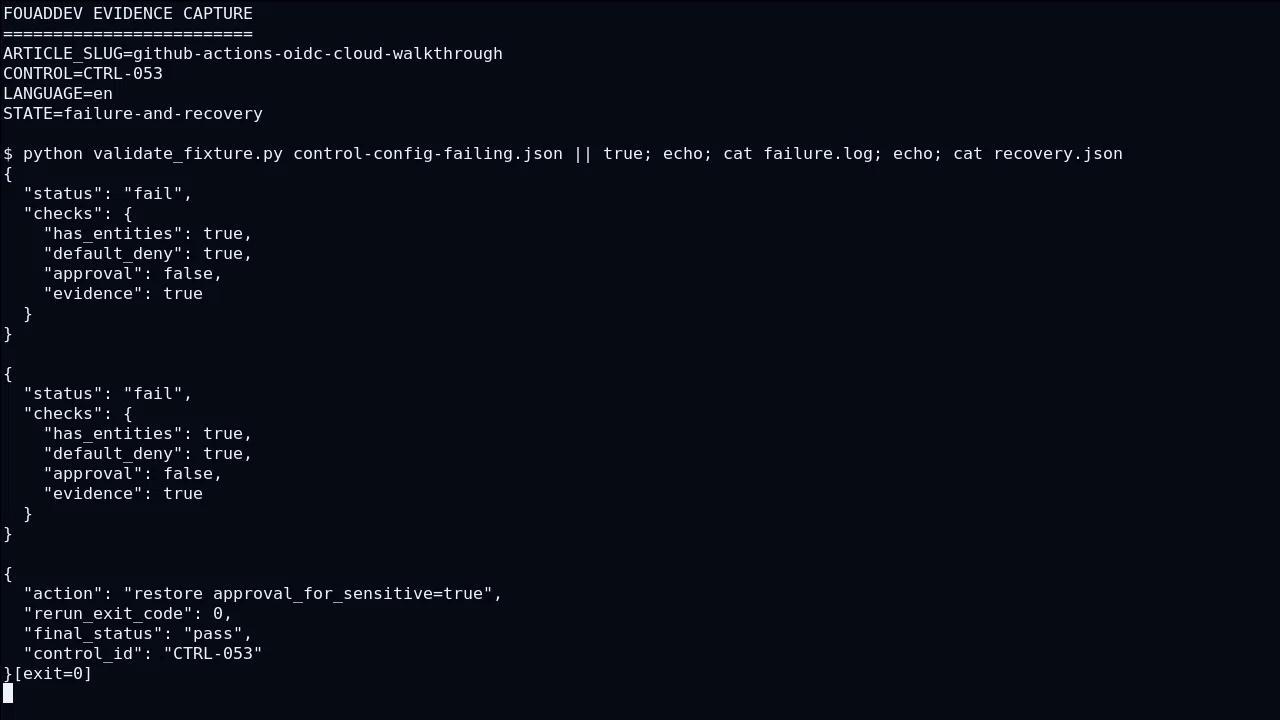
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c61 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. If the GitHub Actions verification fails, rollback restores the configuration around OIDC, replays github-actions-oidc-cloud-walkthrough-c61, and compares the new state with the control evidence from audience. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to subject, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by cloud role and OIDC: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c61 is labeled as a limitation or inference, never promoted to fact.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c62 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns subject into a reviewable decision point with a named input and a retained output. To test cloud role, fixture github-actions-oidc-cloud-walkthrough-c62 contains both an allowed state and a rejected state; rejection must occur before any change attributed to GitHub Actions. Operations then observes the transition between GitHub Actions and OIDC, while security checks that audience receives neither implicit authority nor unnecessary data.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c63 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. If the audience verification fails, rollback restores the configuration around subject, replays github-actions-oidc-cloud-walkthrough-c63, and compares the new state with the control evidence from cloud role. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to GitHub Actions, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OIDC and subject: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c63 is labeled as a limitation or inference, never promoted to fact.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c64 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns GitHub Actions into a reviewable decision point with a named input and a retained output. To test OIDC, fixture github-actions-oidc-cloud-walkthrough-c64 contains both an allowed state and a rejected state; rejection must occur before any change attributed to audience. Operations then observes the transition between audience and subject, while security checks that cloud role receives neither implicit authority nor unnecessary data.
Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
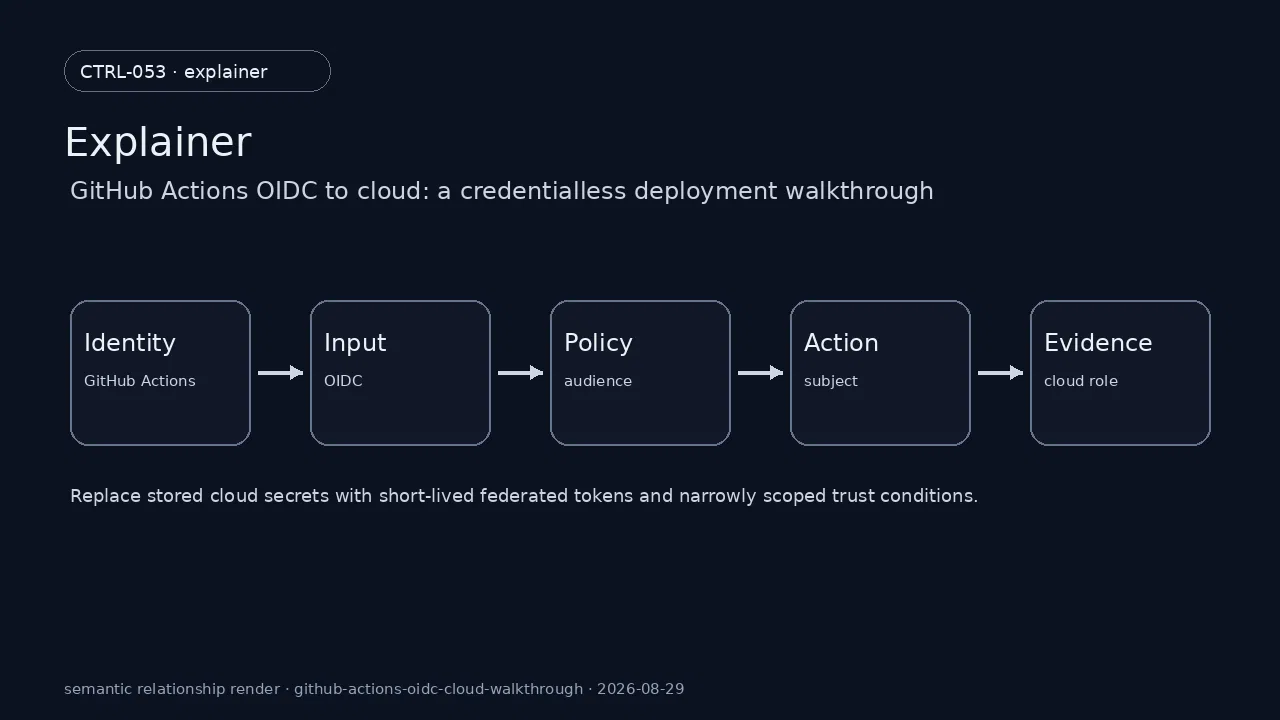
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c71 starts at subject and treats cloud role as an explicit boundary rather than an implicit assumption. The first control requires GitHub Actions to emit an observable result before OIDC can trigger the intended effect around audience. Operations then observes the transition between GitHub Actions and OIDC, while security checks that audience receives neither implicit authority nor unnecessary data. If the OIDC verification fails, rollback restores the configuration around audience, replays github-actions-oidc-cloud-walkthrough-c71, and compares the new state with the control evidence from subject. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to cloud role, a concrete condition, and evidence instead of a generic assurance.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c72 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. The conclusion stays bounded by OIDC and subject: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c72 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns cloud role into a reviewable decision point with a named input and a retained output. To test GitHub Actions, fixture github-actions-oidc-cloud-walkthrough-c72 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OIDC.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c73 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. Operations then observes the transition between audience and subject, while security checks that cloud role receives neither implicit authority nor unnecessary data. If the subject verification fails, rollback restores the configuration around cloud role, replays github-actions-oidc-cloud-walkthrough-c73, and compares the new state with the control evidence from GitHub Actions. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to OIDC, a concrete condition, and evidence instead of a generic assurance.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c74 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. The conclusion stays bounded by subject and GitHub Actions: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c74 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns OIDC into a reviewable decision point with a named input and a retained output. To test audience, fixture github-actions-oidc-cloud-walkthrough-c74 contains both an allowed state and a rejected state; rejection must occur before any change attributed to subject.
Evidence point: GitHub documents that gitHub recommends pinning third-party actions to full-length commit SHAs to obtain an immutable reference. This source anchors production decision criteria but does not replace local verification. [S7]Controls that remain after launch
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c81 starts at cloud role and treats GitHub Actions as an explicit boundary rather than an implicit assumption. The first control requires OIDC to emit an observable result before audience can trigger the intended effect around subject. To test GitHub Actions, fixture github-actions-oidc-cloud-walkthrough-c81 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OIDC. Operations then observes the transition between OIDC and audience, while security checks that subject receives neither implicit authority nor unnecessary data. If the audience verification fails, rollback restores the configuration around subject, replays github-actions-oidc-cloud-walkthrough-c81, and compares the new state with the control evidence from cloud role.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c82 starts at GitHub Actions and treats OIDC as an explicit boundary rather than an implicit assumption. The first control requires audience to emit an observable result before subject can trigger the intended effect around cloud role. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to OIDC, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by audience and cloud role: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c82 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns GitHub Actions into a reviewable decision point with a named input and a retained output.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c83 starts at OIDC and treats audience as an explicit boundary rather than an implicit assumption. The first control requires subject to emit an observable result before cloud role can trigger the intended effect around GitHub Actions. To test audience, fixture github-actions-oidc-cloud-walkthrough-c83 contains both an allowed state and a rejected state; rejection must occur before any change attributed to subject. Operations then observes the transition between subject and cloud role, while security checks that GitHub Actions receives neither implicit authority nor unnecessary data. If the cloud role verification fails, rollback restores the configuration around GitHub Actions, replays github-actions-oidc-cloud-walkthrough-c83, and compares the new state with the control evidence from OIDC.
In “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough”, scenario github-actions-oidc-cloud-walkthrough-c84 starts at audience and treats subject as an explicit boundary rather than an implicit assumption. The first control requires cloud role to emit an observable result before GitHub Actions can trigger the intended effect around OIDC. This detail makes “GitHub Actions OIDC to cloud: a credentialless deployment walkthrough” reviewable because each operational statement points to subject, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by cloud role and OIDC: anything not demonstrated by scenario github-actions-oidc-cloud-walkthrough-c84 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Replace stored cloud secrets with short-lived federated tokens and narrowly scoped trust conditions. It turns audience into a reviewable decision point with a named input and a retained output.
Evidence point: GitHub documents that dependency review exposes added, removed and updated dependencies together with vulnerability context before changes are merged. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around GitHub Actions has an input, a rule, a rejection behavior, and evidence.
- The control around OIDC has an input, a rule, a rejection behavior, and evidence.
- The control around audience has an input, a rule, a rejection behavior, and evidence.
- The control around subject has an input, a rule, a rejection behavior, and evidence.
- The control around cloud role has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] Supply chain security - GitHub Docs — GitHub supply-chain controls combine dependency visibility, vulnerability alerts, automated updates and review workflows. source
- [S2] Configuring the dependency review action — The dependency review action can fail pull requests based on vulnerability severity, dependency scope or license rules. source
- [S3] Security Checklist - Kubernetes — Kubernetes publishes a baseline security checklist while warning that cluster security requires ongoing context-specific attention rather than checklist compliance alone. source
- [S4] Application Security Checklist - Kubernetes — Kubernetes application guidance covers secure workload practices from the developer perspective. source
- [S5] Configuring OpenID Connect in cloud providers — GitHub Actions OIDC lets workflows obtain cloud access without storing long-lived cloud credentials, provided trust conditions constrain token issuance. source
- [S6] OpenID Connect reference - GitHub Docs — GitHub documents OIDC token claims such as issuer, audience and subject that cloud trust policies can evaluate. source
- [S7] Secure use reference - GitHub Actions — GitHub recommends pinning third-party actions to full-length commit SHAs to obtain an immutable reference. source
- [S8] Reviewing dependency changes in a pull request — Dependency review exposes added, removed and updated dependencies together with vulnerability context before changes are merged. source
- [S9] Running agents - OpenAI Agents SDK — Run configuration controls model setup, guardrails, handoff behavior, tracing, tool execution and conversation state. source
- [S10] Tools - OpenAI Agents SDK — The SDK distinguishes hosted tools, local execution tools, function tools and agents-as-tools, each with different trust and execution boundaries. source



Comments
No published comment yet.
Sign in to comment