OWASP API SSRF: defend the outbound request path, not only the URL field addresses one concrete problem: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. The guide works from the actual objects — OWASP API7:2023, SSRF, URL, DNS, egress — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: OWASP API7:2023 meets SSRF
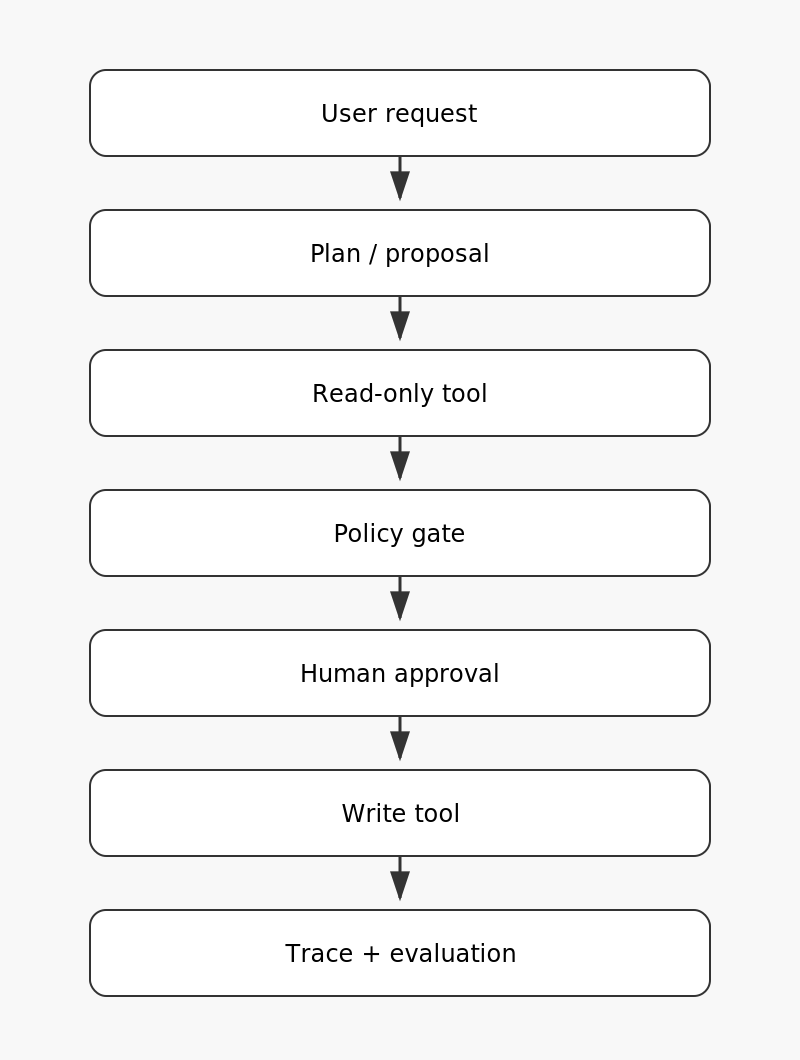
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c11 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. To test OWASP API7:2023, fixture owasp-api-ssrf-outbound-controls-c11 contains both an allowed state and a rejected state; rejection must occur before any change attributed to SSRF. Operations then observes the transition between SSRF and URL, while security checks that DNS receives neither implicit authority nor unnecessary data. If the URL verification fails, rollback restores the configuration around DNS, replays owasp-api-ssrf-outbound-controls-c11, and compares the new state with the control evidence from egress.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c12 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to SSRF, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by URL and egress: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c12 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns OWASP API7:2023 into a reviewable decision point with a named input and a retained output.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c13 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. To test URL, fixture owasp-api-ssrf-outbound-controls-c13 contains both an allowed state and a rejected state; rejection must occur before any change attributed to DNS. Operations then observes the transition between DNS and egress, while security checks that OWASP API7:2023 receives neither implicit authority nor unnecessary data. If the egress verification fails, rollback restores the configuration around OWASP API7:2023, replays owasp-api-ssrf-outbound-controls-c13, and compares the new state with the control evidence from SSRF.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c14 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to DNS, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by egress and SSRF: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c14 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns URL into a reviewable decision point with a named input and a retained output.
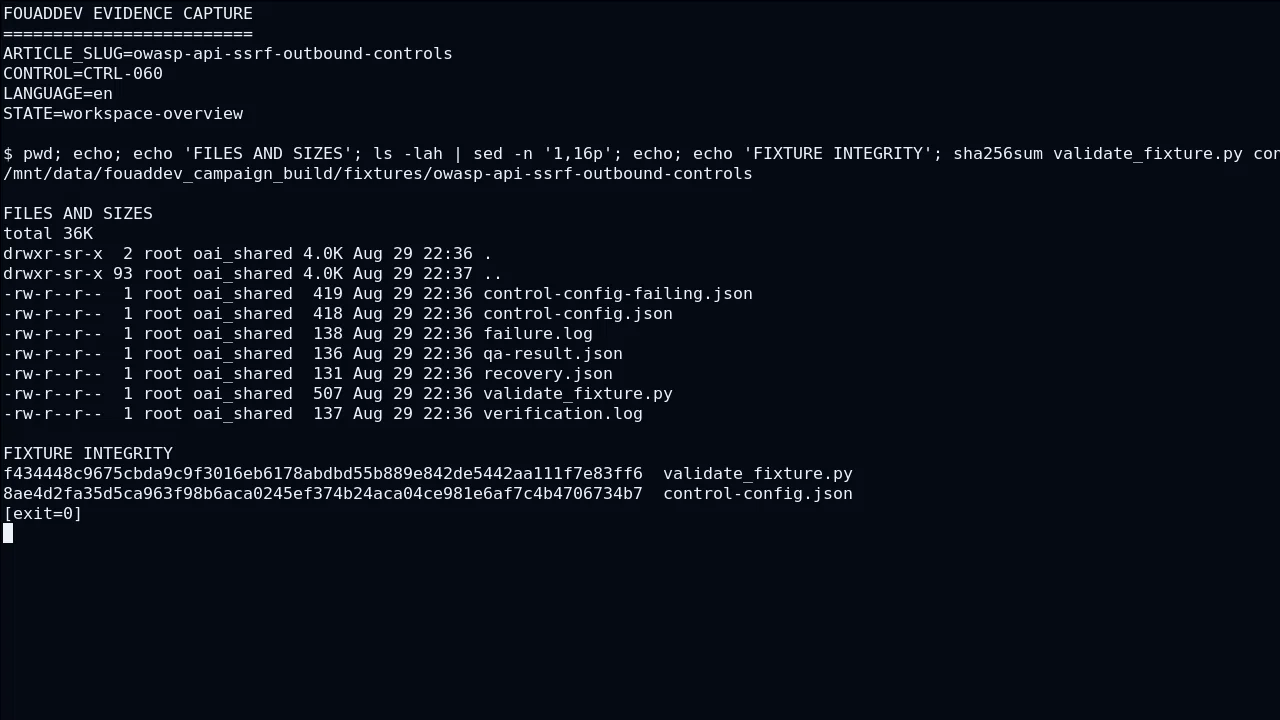
Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c21 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns OWASP API7:2023 into a reviewable decision point with a named input and a retained output. To test SSRF, fixture owasp-api-ssrf-outbound-controls-c21 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URL. Operations then observes the transition between URL and DNS, while security checks that egress receives neither implicit authority nor unnecessary data.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c22 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. If the egress verification fails, rollback restores the configuration around OWASP API7:2023, replays owasp-api-ssrf-outbound-controls-c22, and compares the new state with the control evidence from SSRF. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to URL, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by DNS and OWASP API7:2023: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c22 is labeled as a limitation or inference, never promoted to fact.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c23 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns URL into a reviewable decision point with a named input and a retained output. To test DNS, fixture owasp-api-ssrf-outbound-controls-c23 contains both an allowed state and a rejected state; rejection must occur before any change attributed to egress. Operations then observes the transition between egress and OWASP API7:2023, while security checks that SSRF receives neither implicit authority nor unnecessary data.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c24 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. If the SSRF verification fails, rollback restores the configuration around URL, replays owasp-api-ssrf-outbound-controls-c24, and compares the new state with the control evidence from DNS. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to egress, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OWASP API7:2023 and URL: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c24 is labeled as a limitation or inference, never promoted to fact.
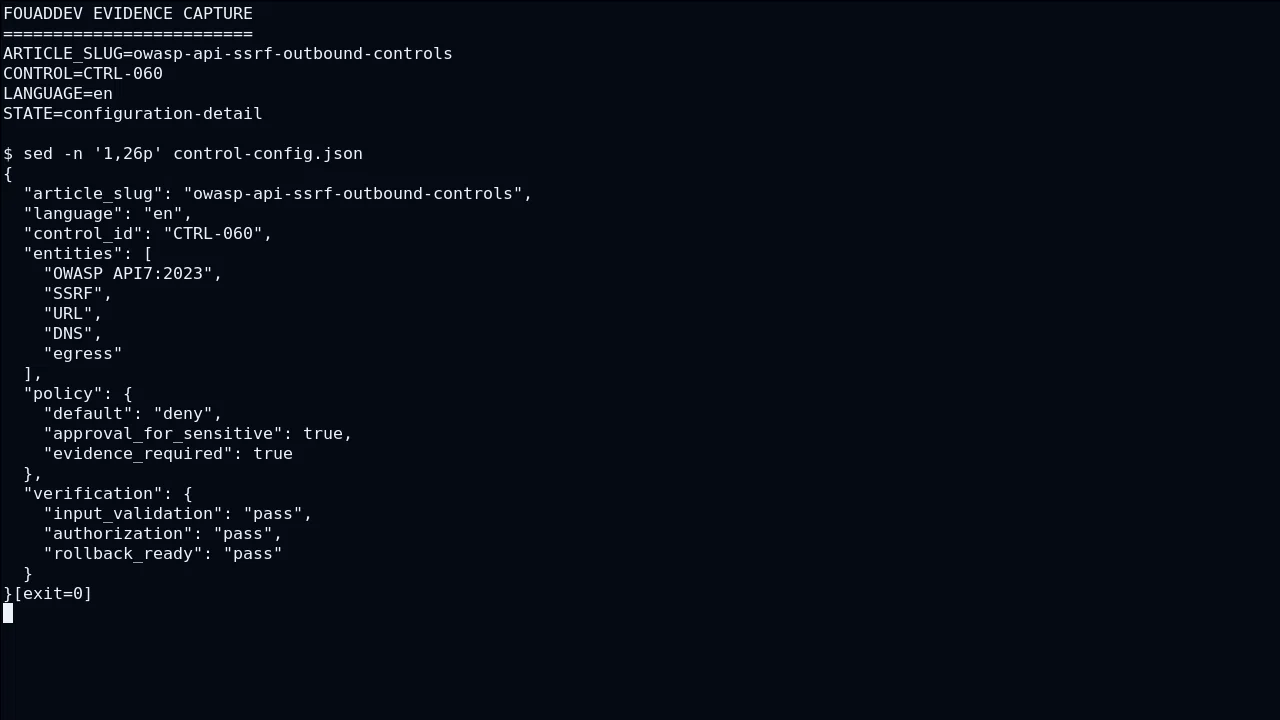
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c31 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. The conclusion stays bounded by DNS and OWASP API7:2023: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c31 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns SSRF into a reviewable decision point with a named input and a retained output. To test URL, fixture owasp-api-ssrf-outbound-controls-c31 contains both an allowed state and a rejected state; rejection must occur before any change attributed to DNS.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c32 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. Operations then observes the transition between egress and OWASP API7:2023, while security checks that SSRF receives neither implicit authority nor unnecessary data. If the OWASP API7:2023 verification fails, rollback restores the configuration around SSRF, replays owasp-api-ssrf-outbound-controls-c32, and compares the new state with the control evidence from URL. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to DNS, a concrete condition, and evidence instead of a generic assurance.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c33 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. The conclusion stays bounded by OWASP API7:2023 and URL: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c33 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns DNS into a reviewable decision point with a named input and a retained output. To test egress, fixture owasp-api-ssrf-outbound-controls-c33 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP API7:2023.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c34 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. Operations then observes the transition between SSRF and URL, while security checks that DNS receives neither implicit authority nor unnecessary data. If the URL verification fails, rollback restores the configuration around DNS, replays owasp-api-ssrf-outbound-controls-c34, and compares the new state with the control evidence from egress. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to OWASP API7:2023, a concrete condition, and evidence instead of a generic assurance.
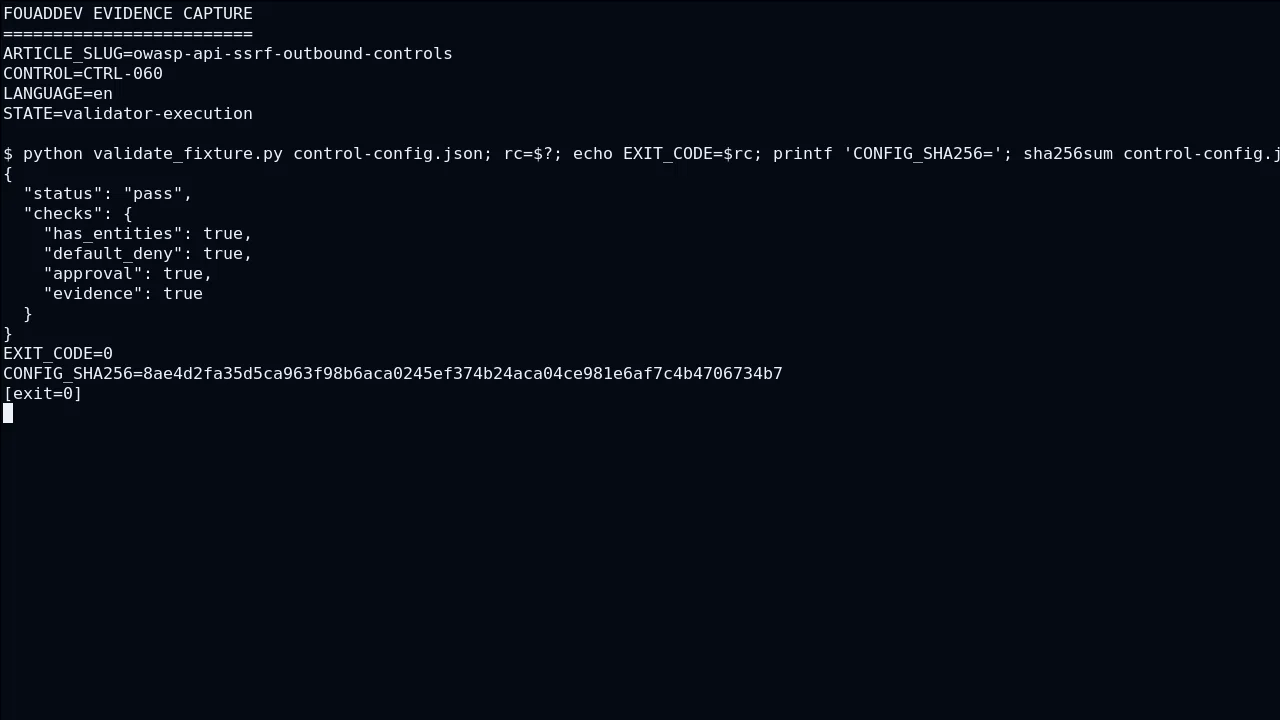
Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c41 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to DNS, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by egress and SSRF: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c41 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns URL into a reviewable decision point with a named input and a retained output.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c42 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. To test egress, fixture owasp-api-ssrf-outbound-controls-c42 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP API7:2023. Operations then observes the transition between OWASP API7:2023 and SSRF, while security checks that URL receives neither implicit authority nor unnecessary data. If the SSRF verification fails, rollback restores the configuration around URL, replays owasp-api-ssrf-outbound-controls-c42, and compares the new state with the control evidence from DNS.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c43 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to OWASP API7:2023, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by SSRF and DNS: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c43 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns egress into a reviewable decision point with a named input and a retained output.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c44 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. To test SSRF, fixture owasp-api-ssrf-outbound-controls-c44 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URL. Operations then observes the transition between URL and DNS, while security checks that egress receives neither implicit authority nor unnecessary data. If the DNS verification fails, rollback restores the configuration around egress, replays owasp-api-ssrf-outbound-controls-c44, and compares the new state with the control evidence from OWASP API7:2023.
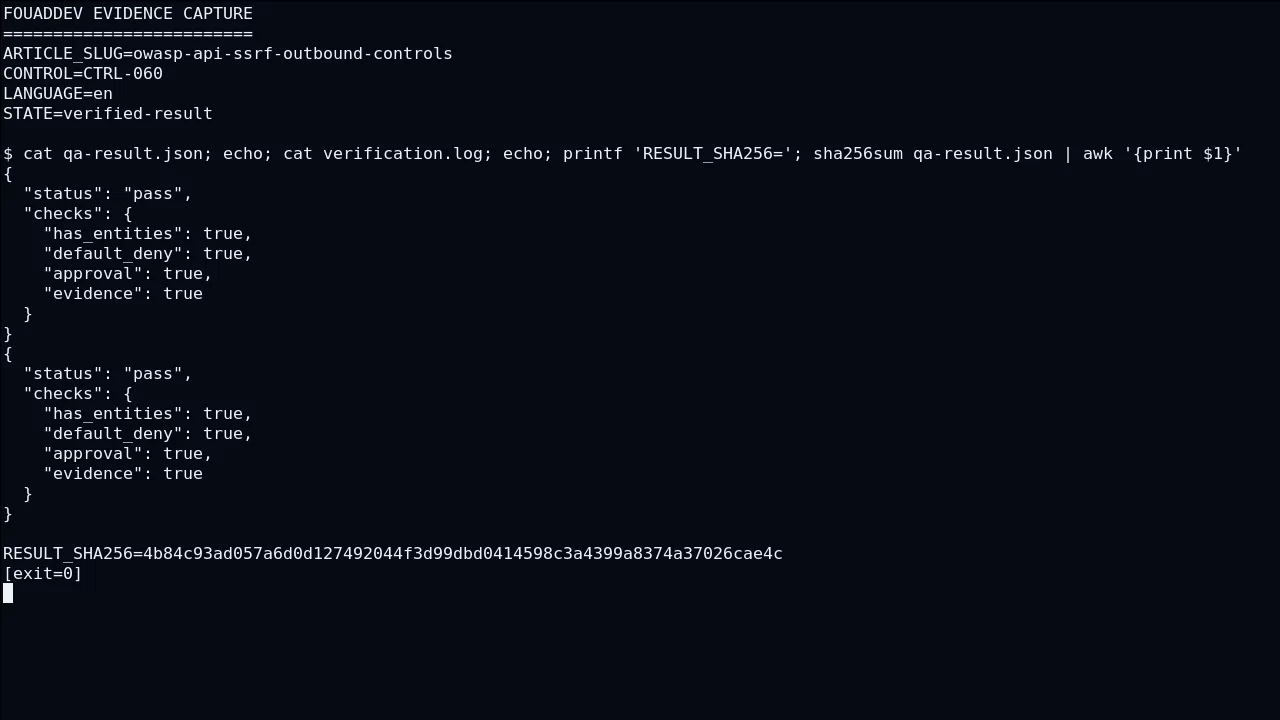
Trust boundaries around URL
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c51 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. If the SSRF verification fails, rollback restores the configuration around URL, replays owasp-api-ssrf-outbound-controls-c51, and compares the new state with the control evidence from DNS. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to egress, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OWASP API7:2023 and URL: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c51 is labeled as a limitation or inference, never promoted to fact.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c52 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns egress into a reviewable decision point with a named input and a retained output. To test OWASP API7:2023, fixture owasp-api-ssrf-outbound-controls-c52 contains both an allowed state and a rejected state; rejection must occur before any change attributed to SSRF. Operations then observes the transition between SSRF and URL, while security checks that DNS receives neither implicit authority nor unnecessary data.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c53 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. If the DNS verification fails, rollback restores the configuration around egress, replays owasp-api-ssrf-outbound-controls-c53, and compares the new state with the control evidence from OWASP API7:2023. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to SSRF, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by URL and egress: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c53 is labeled as a limitation or inference, never promoted to fact.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c54 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns SSRF into a reviewable decision point with a named input and a retained output. To test URL, fixture owasp-api-ssrf-outbound-controls-c54 contains both an allowed state and a rejected state; rejection must occur before any change attributed to DNS. Operations then observes the transition between DNS and egress, while security checks that OWASP API7:2023 receives neither implicit authority nor unnecessary data.
Build the decision path with DNS
The starting point is not a feature; it is an observable decision boundary.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c61 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. Operations then observes the transition between SSRF and URL, while security checks that DNS receives neither implicit authority nor unnecessary data. If the URL verification fails, rollback restores the configuration around DNS, replays owasp-api-ssrf-outbound-controls-c61, and compares the new state with the control evidence from egress. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to OWASP API7:2023, a concrete condition, and evidence instead of a generic assurance.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c62 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. The conclusion stays bounded by URL and egress: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c62 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns OWASP API7:2023 into a reviewable decision point with a named input and a retained output. To test SSRF, fixture owasp-api-ssrf-outbound-controls-c62 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URL.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c63 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. Operations then observes the transition between DNS and egress, while security checks that OWASP API7:2023 receives neither implicit authority nor unnecessary data. If the egress verification fails, rollback restores the configuration around OWASP API7:2023, replays owasp-api-ssrf-outbound-controls-c63, and compares the new state with the control evidence from SSRF. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to URL, a concrete condition, and evidence instead of a generic assurance.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c64 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. The conclusion stays bounded by egress and SSRF: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c64 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns URL into a reviewable decision point with a named input and a retained output. To test DNS, fixture owasp-api-ssrf-outbound-controls-c64 contains both an allowed state and a rejected state; rejection must occur before any change attributed to egress.
Verify egress with observable evidence
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c71 starts at OWASP API7:2023 and treats SSRF as an explicit boundary rather than an implicit assumption. The first control requires URL to emit an observable result before DNS can trigger the intended effect around egress. To test SSRF, fixture owasp-api-ssrf-outbound-controls-c71 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URL. Operations then observes the transition between URL and DNS, while security checks that egress receives neither implicit authority nor unnecessary data. If the DNS verification fails, rollback restores the configuration around egress, replays owasp-api-ssrf-outbound-controls-c71, and compares the new state with the control evidence from OWASP API7:2023.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c72 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to URL, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by DNS and OWASP API7:2023: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c72 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns SSRF into a reviewable decision point with a named input and a retained output.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c73 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. To test DNS, fixture owasp-api-ssrf-outbound-controls-c73 contains both an allowed state and a rejected state; rejection must occur before any change attributed to egress. Operations then observes the transition between egress and OWASP API7:2023, while security checks that SSRF receives neither implicit authority nor unnecessary data. If the OWASP API7:2023 verification fails, rollback restores the configuration around SSRF, replays owasp-api-ssrf-outbound-controls-c73, and compares the new state with the control evidence from URL.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c74 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to egress, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OWASP API7:2023 and URL: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c74 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns DNS into a reviewable decision point with a named input and a retained output.
Evidence point: OWASP documents that oWASP REST guidance emphasizes HTTPS, explicit access control and careful handling of tokens, methods, inputs and security headers. This source anchors verify egress with observable evidence but does not replace local verification. [S7]Controls that remain after launch
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c81 starts at SSRF and treats URL as an explicit boundary rather than an implicit assumption. The first control requires DNS to emit an observable result before egress can trigger the intended effect around OWASP API7:2023. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns SSRF into a reviewable decision point with a named input and a retained output. To test URL, fixture owasp-api-ssrf-outbound-controls-c81 contains both an allowed state and a rejected state; rejection must occur before any change attributed to DNS. Operations then observes the transition between DNS and egress, while security checks that OWASP API7:2023 receives neither implicit authority nor unnecessary data.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c82 starts at URL and treats DNS as an explicit boundary rather than an implicit assumption. The first control requires egress to emit an observable result before OWASP API7:2023 can trigger the intended effect around SSRF. If the OWASP API7:2023 verification fails, rollback restores the configuration around SSRF, replays owasp-api-ssrf-outbound-controls-c82, and compares the new state with the control evidence from URL. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to DNS, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by egress and SSRF: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c82 is labeled as a limitation or inference, never promoted to fact.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c83 starts at DNS and treats egress as an explicit boundary rather than an implicit assumption. The first control requires OWASP API7:2023 to emit an observable result before SSRF can trigger the intended effect around URL. That sequence serves this concrete job: Control destination resolution, protocols, redirects and network egress for features that fetch user-influenced URLs. It turns DNS into a reviewable decision point with a named input and a retained output. To test egress, fixture owasp-api-ssrf-outbound-controls-c83 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP API7:2023. Operations then observes the transition between OWASP API7:2023 and SSRF, while security checks that URL receives neither implicit authority nor unnecessary data.
In “OWASP API SSRF: defend the outbound request path, not only the URL field”, scenario owasp-api-ssrf-outbound-controls-c84 starts at egress and treats OWASP API7:2023 as an explicit boundary rather than an implicit assumption. The first control requires SSRF to emit an observable result before URL can trigger the intended effect around DNS. If the URL verification fails, rollback restores the configuration around DNS, replays owasp-api-ssrf-outbound-controls-c84, and compares the new state with the control evidence from egress. This detail makes “OWASP API SSRF: defend the outbound request path, not only the URL field” reviewable because each operational statement points to OWASP API7:2023, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by SSRF and DNS: anything not demonstrated by scenario owasp-api-ssrf-outbound-controls-c84 is labeled as a limitation or inference, never promoted to fact.
Evidence point: OWASP documents that oWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around OWASP API7:2023 has an input, a rule, a rejection behavior, and evidence.
- The control around SSRF has an input, a rule, a rejection behavior, and evidence.
- The control around URL has an input, a rule, a rejection behavior, and evidence.
- The control around DNS has an input, a rule, a rejection behavior, and evidence.
- The control around egress has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] OWASP Top 10 for LLM Applications 2025 — The 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. source
- [S2] RFC 9700: Best Current Practice for OAuth 2.0 Security — RFC 9700 updates OAuth 2.0 security practice, including exact redirect URI matching and avoiding open redirectors and insecure legacy patterns. source
- [S3] Authentication Cheat Sheet — OWASP authentication guidance separates identity proofing, authentication and session management and recommends strong controls for sensitive operations. source
- [S4] Content Security Policy Cheat Sheet — OWASP recommends strict CSP designs based on nonces or hashes instead of large static allowlists. source
- [S5] Security Checklist - Kubernetes — Kubernetes publishes a baseline security checklist while warning that cluster security requires ongoing context-specific attention rather than checklist compliance alone. source
- [S6] OWASP API Security Top 10 2023 — OWASP API Security Top 10 2023 highlights authorization failures, authentication weaknesses, resource abuse, SSRF, misconfiguration and unsafe API consumption. source
- [S7] REST Security Cheat Sheet — OWASP REST guidance emphasizes HTTPS, explicit access control and careful handling of tokens, methods, inputs and security headers. source
- [S8] OWASP Top 10 for Large Language Model Applications — OWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. source
- [S9] Encrypted session - OpenAI Agents SDK — EncryptedSession can wrap a session store with Fernet encryption, per-session HKDF-derived keys and TTL-based expiration. source
- [S10] Results - OpenAI Agents SDK — Run results expose final output, new items, agent identity, raw responses, guardrail results, state and usage diagnostics. source



Comments
No published comment yet.
Sign in to comment