OWASP LLM Top 10 2026: test excessive agency as an authorization failure addresses one concrete problem: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. The guide works from the actual objects — OWASP LLM Top 10 2026, excessive agency, authorization, tool permission, least privilege — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: OWASP LLM Top 10 2026 meets excessive agency
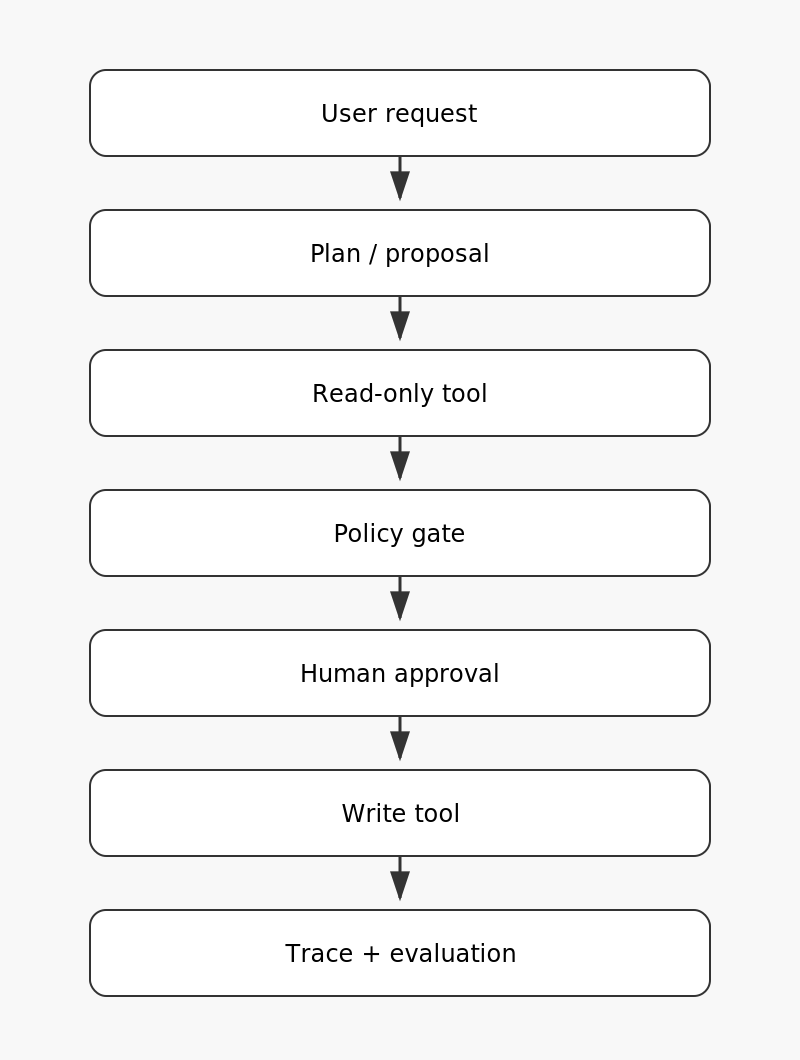
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c11 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. If the authorization verification fails, rollback restores the configuration around tool permission, replays owasp-llm-2026-excessive-agency-c11, and compares the new state with the control evidence from least privilege. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to OWASP LLM Top 10 2026, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by excessive agency and tool permission: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c11 is labeled as a limitation or inference, never promoted to fact.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c12 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns OWASP LLM Top 10 2026 into a reviewable decision point with a named input and a retained output. To test excessive agency, fixture owasp-llm-2026-excessive-agency-c12 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization. Operations then observes the transition between authorization and tool permission, while security checks that least privilege receives neither implicit authority nor unnecessary data.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c13 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. If the least privilege verification fails, rollback restores the configuration around OWASP LLM Top 10 2026, replays owasp-llm-2026-excessive-agency-c13, and compares the new state with the control evidence from excessive agency. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by tool permission and OWASP LLM Top 10 2026: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c13 is labeled as a limitation or inference, never promoted to fact.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c14 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns authorization into a reviewable decision point with a named input and a retained output. To test tool permission, fixture owasp-llm-2026-excessive-agency-c14 contains both an allowed state and a rejected state; rejection must occur before any change attributed to least privilege. Operations then observes the transition between least privilege and OWASP LLM Top 10 2026, while security checks that excessive agency receives neither implicit authority nor unnecessary data.
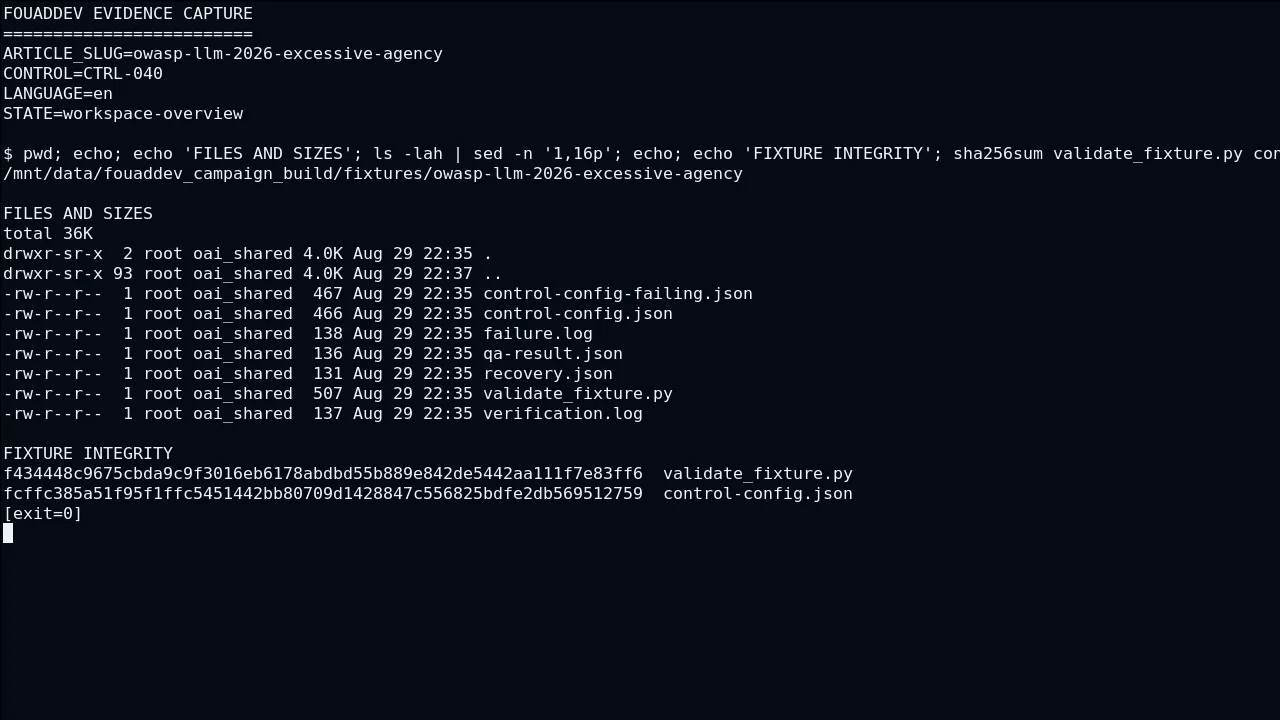
Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c21 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. Operations then observes the transition between authorization and tool permission, while security checks that least privilege receives neither implicit authority nor unnecessary data. If the tool permission verification fails, rollback restores the configuration around least privilege, replays owasp-llm-2026-excessive-agency-c21, and compares the new state with the control evidence from OWASP LLM Top 10 2026. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to excessive agency, a concrete condition, and evidence instead of a generic assurance.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c22 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. The conclusion stays bounded by tool permission and OWASP LLM Top 10 2026: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c22 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns excessive agency into a reviewable decision point with a named input and a retained output. To test authorization, fixture owasp-llm-2026-excessive-agency-c22 contains both an allowed state and a rejected state; rejection must occur before any change attributed to tool permission.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c23 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. Operations then observes the transition between least privilege and OWASP LLM Top 10 2026, while security checks that excessive agency receives neither implicit authority nor unnecessary data. If the OWASP LLM Top 10 2026 verification fails, rollback restores the configuration around excessive agency, replays owasp-llm-2026-excessive-agency-c23, and compares the new state with the control evidence from authorization. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to tool permission, a concrete condition, and evidence instead of a generic assurance.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c24 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. The conclusion stays bounded by OWASP LLM Top 10 2026 and authorization: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c24 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns tool permission into a reviewable decision point with a named input and a retained output. To test least privilege, fixture owasp-llm-2026-excessive-agency-c24 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP LLM Top 10 2026.
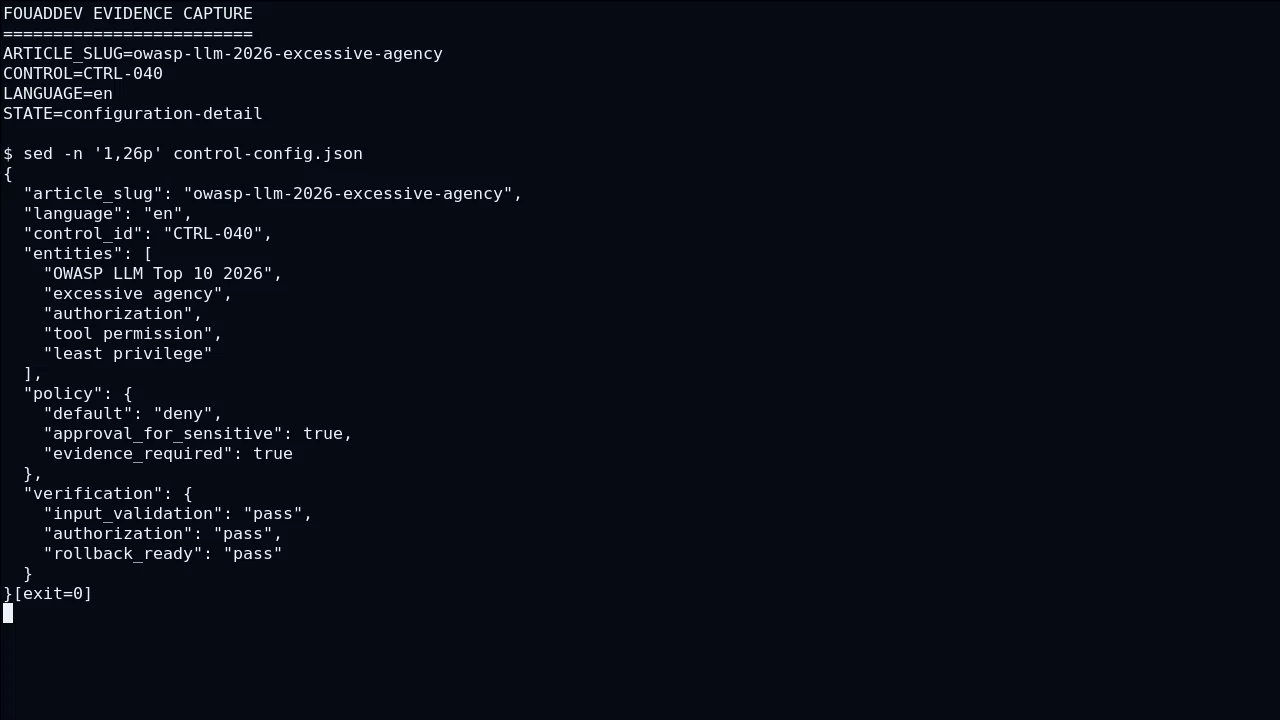
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c31 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. To test authorization, fixture owasp-llm-2026-excessive-agency-c31 contains both an allowed state and a rejected state; rejection must occur before any change attributed to tool permission. Operations then observes the transition between tool permission and least privilege, while security checks that OWASP LLM Top 10 2026 receives neither implicit authority nor unnecessary data. If the least privilege verification fails, rollback restores the configuration around OWASP LLM Top 10 2026, replays owasp-llm-2026-excessive-agency-c31, and compares the new state with the control evidence from excessive agency.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c32 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to tool permission, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by least privilege and excessive agency: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c32 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns authorization into a reviewable decision point with a named input and a retained output.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c33 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. To test least privilege, fixture owasp-llm-2026-excessive-agency-c33 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP LLM Top 10 2026. Operations then observes the transition between OWASP LLM Top 10 2026 and excessive agency, while security checks that authorization receives neither implicit authority nor unnecessary data. If the excessive agency verification fails, rollback restores the configuration around authorization, replays owasp-llm-2026-excessive-agency-c33, and compares the new state with the control evidence from tool permission.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c34 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to OWASP LLM Top 10 2026, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by excessive agency and tool permission: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c34 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns least privilege into a reviewable decision point with a named input and a retained output.
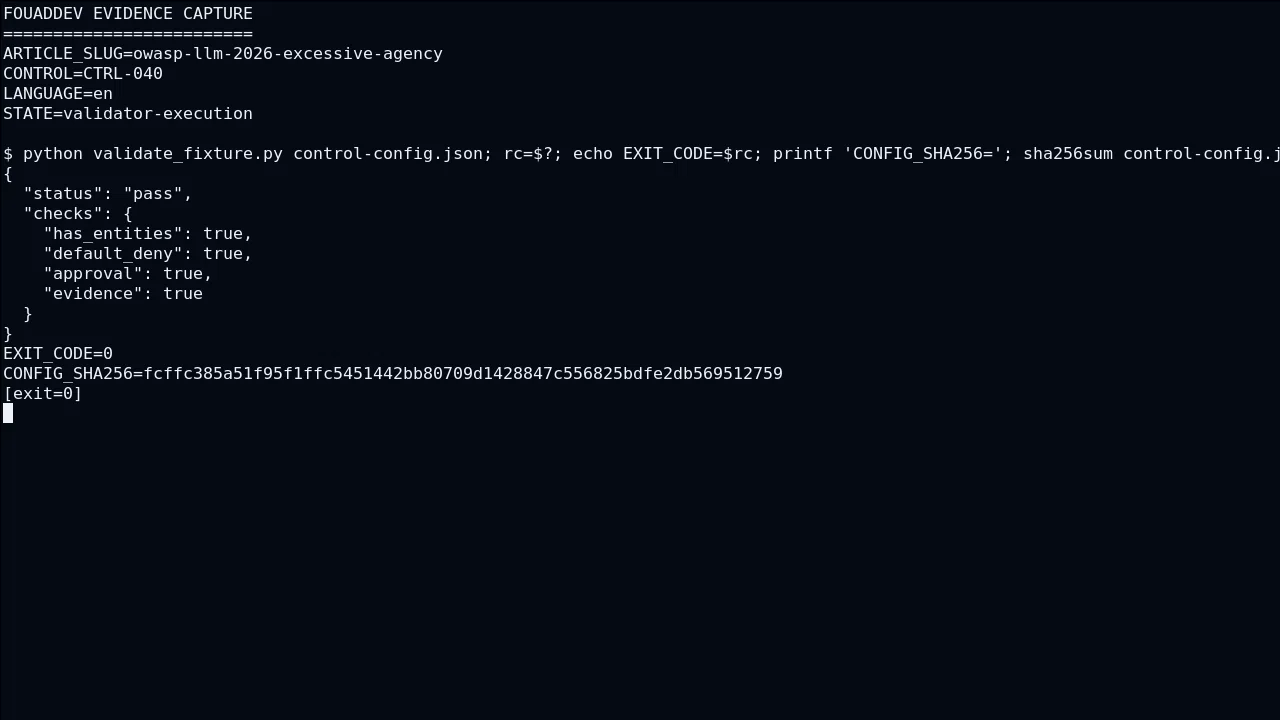
Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c41 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns authorization into a reviewable decision point with a named input and a retained output. To test tool permission, fixture owasp-llm-2026-excessive-agency-c41 contains both an allowed state and a rejected state; rejection must occur before any change attributed to least privilege. Operations then observes the transition between least privilege and OWASP LLM Top 10 2026, while security checks that excessive agency receives neither implicit authority nor unnecessary data.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c42 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. If the excessive agency verification fails, rollback restores the configuration around authorization, replays owasp-llm-2026-excessive-agency-c42, and compares the new state with the control evidence from tool permission. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to least privilege, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by OWASP LLM Top 10 2026 and authorization: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c42 is labeled as a limitation or inference, never promoted to fact.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c43 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns least privilege into a reviewable decision point with a named input and a retained output. To test OWASP LLM Top 10 2026, fixture owasp-llm-2026-excessive-agency-c43 contains both an allowed state and a rejected state; rejection must occur before any change attributed to excessive agency. Operations then observes the transition between excessive agency and authorization, while security checks that tool permission receives neither implicit authority nor unnecessary data.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c44 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. If the tool permission verification fails, rollback restores the configuration around least privilege, replays owasp-llm-2026-excessive-agency-c44, and compares the new state with the control evidence from OWASP LLM Top 10 2026. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to excessive agency, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization and least privilege: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c44 is labeled as a limitation or inference, never promoted to fact.
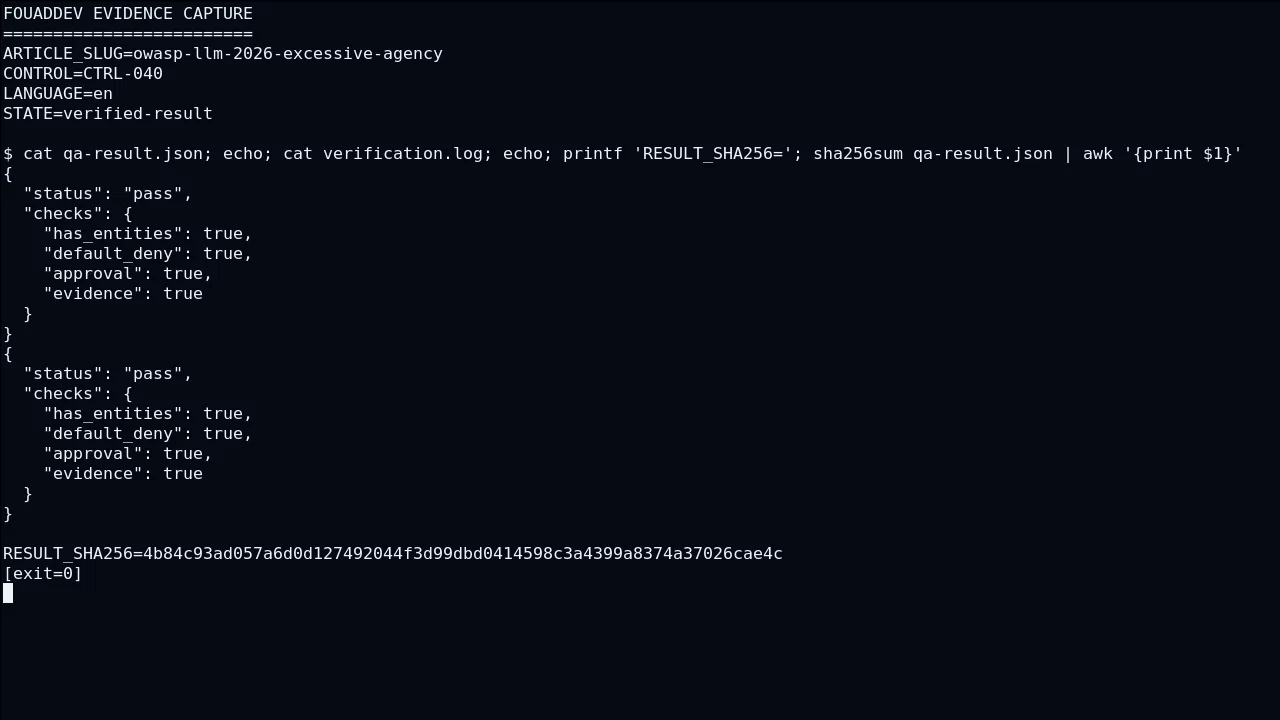
Trust boundaries around authorization
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c51 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. The conclusion stays bounded by OWASP LLM Top 10 2026 and authorization: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c51 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns tool permission into a reviewable decision point with a named input and a retained output. To test least privilege, fixture owasp-llm-2026-excessive-agency-c51 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP LLM Top 10 2026.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c52 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. Operations then observes the transition between excessive agency and authorization, while security checks that tool permission receives neither implicit authority nor unnecessary data. If the authorization verification fails, rollback restores the configuration around tool permission, replays owasp-llm-2026-excessive-agency-c52, and compares the new state with the control evidence from least privilege. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to OWASP LLM Top 10 2026, a concrete condition, and evidence instead of a generic assurance.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c53 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. The conclusion stays bounded by authorization and least privilege: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c53 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns OWASP LLM Top 10 2026 into a reviewable decision point with a named input and a retained output. To test excessive agency, fixture owasp-llm-2026-excessive-agency-c53 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c54 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. Operations then observes the transition between tool permission and least privilege, while security checks that OWASP LLM Top 10 2026 receives neither implicit authority nor unnecessary data. If the least privilege verification fails, rollback restores the configuration around OWASP LLM Top 10 2026, replays owasp-llm-2026-excessive-agency-c54, and compares the new state with the control evidence from excessive agency. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance.
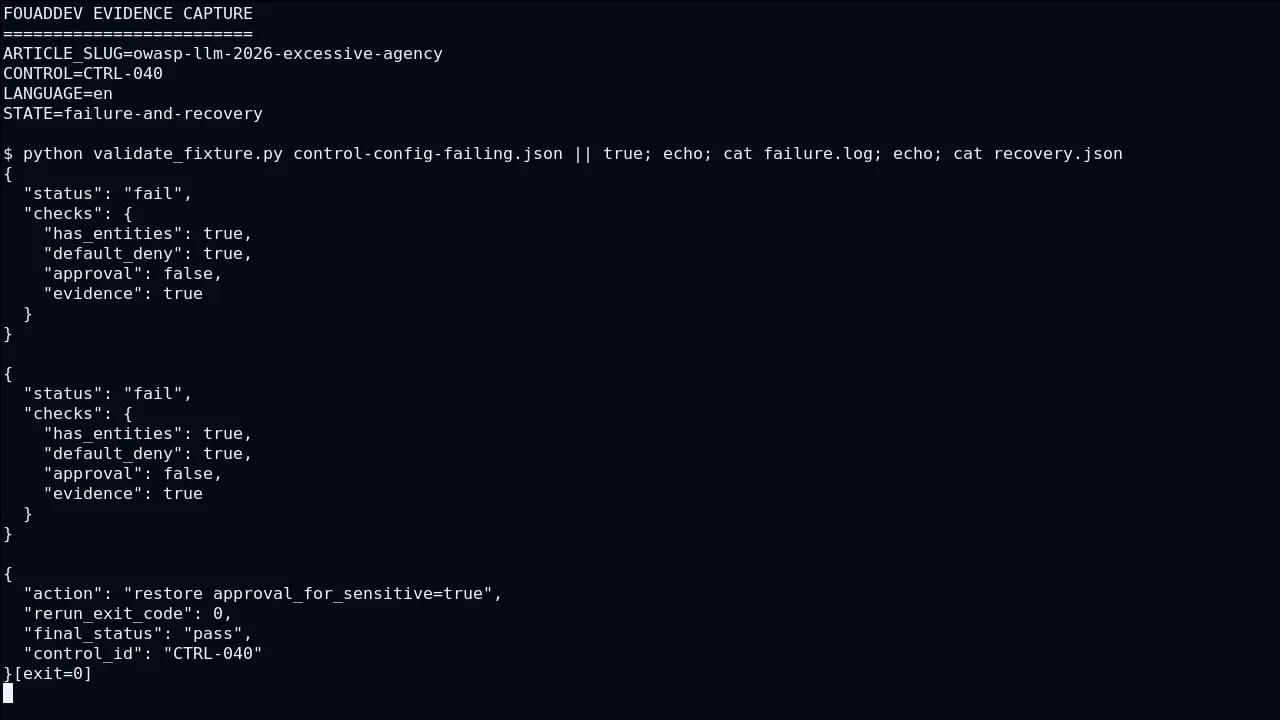
Build the decision path with tool permission
The starting point is not a feature; it is an observable decision boundary.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c61 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to OWASP LLM Top 10 2026, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by excessive agency and tool permission: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c61 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns least privilege into a reviewable decision point with a named input and a retained output.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c62 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. To test excessive agency, fixture owasp-llm-2026-excessive-agency-c62 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization. Operations then observes the transition between authorization and tool permission, while security checks that least privilege receives neither implicit authority nor unnecessary data. If the tool permission verification fails, rollback restores the configuration around least privilege, replays owasp-llm-2026-excessive-agency-c62, and compares the new state with the control evidence from OWASP LLM Top 10 2026.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c63 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by tool permission and OWASP LLM Top 10 2026: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c63 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns excessive agency into a reviewable decision point with a named input and a retained output.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c64 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. To test tool permission, fixture owasp-llm-2026-excessive-agency-c64 contains both an allowed state and a rejected state; rejection must occur before any change attributed to least privilege. Operations then observes the transition between least privilege and OWASP LLM Top 10 2026, while security checks that excessive agency receives neither implicit authority nor unnecessary data. If the OWASP LLM Top 10 2026 verification fails, rollback restores the configuration around excessive agency, replays owasp-llm-2026-excessive-agency-c64, and compares the new state with the control evidence from authorization.
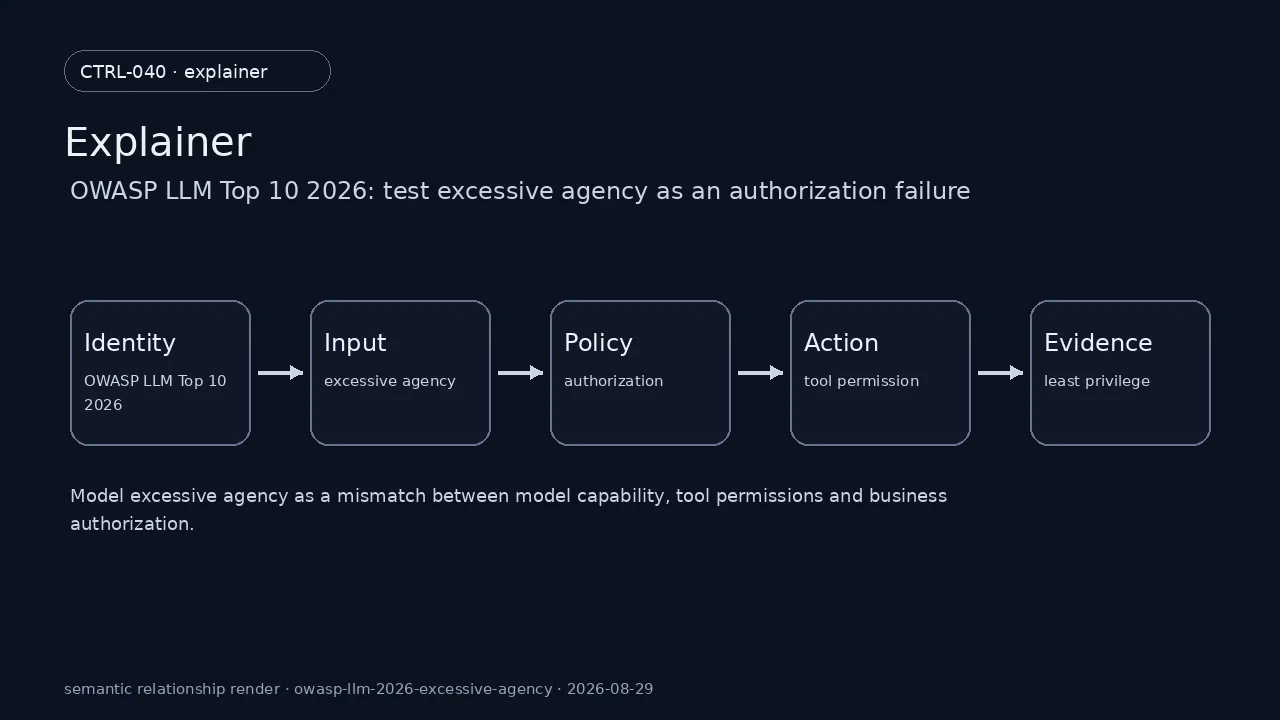
Verify least privilege with observable evidence
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c71 starts at OWASP LLM Top 10 2026 and treats excessive agency as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before tool permission can trigger the intended effect around least privilege. If the tool permission verification fails, rollback restores the configuration around least privilege, replays owasp-llm-2026-excessive-agency-c71, and compares the new state with the control evidence from OWASP LLM Top 10 2026. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to excessive agency, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization and least privilege: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c71 is labeled as a limitation or inference, never promoted to fact.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c72 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns excessive agency into a reviewable decision point with a named input and a retained output. To test authorization, fixture owasp-llm-2026-excessive-agency-c72 contains both an allowed state and a rejected state; rejection must occur before any change attributed to tool permission. Operations then observes the transition between tool permission and least privilege, while security checks that OWASP LLM Top 10 2026 receives neither implicit authority nor unnecessary data.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c73 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. If the OWASP LLM Top 10 2026 verification fails, rollback restores the configuration around excessive agency, replays owasp-llm-2026-excessive-agency-c73, and compares the new state with the control evidence from authorization. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to tool permission, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by least privilege and excessive agency: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c73 is labeled as a limitation or inference, never promoted to fact.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c74 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns tool permission into a reviewable decision point with a named input and a retained output. To test least privilege, fixture owasp-llm-2026-excessive-agency-c74 contains both an allowed state and a rejected state; rejection must occur before any change attributed to OWASP LLM Top 10 2026. Operations then observes the transition between OWASP LLM Top 10 2026 and excessive agency, while security checks that authorization receives neither implicit authority nor unnecessary data.
Evidence point: OWASP documents that oWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. This source anchors verify least privilege with observable evidence but does not replace local verification. [S7]Controls that remain after launch
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c81 starts at excessive agency and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires tool permission to emit an observable result before least privilege can trigger the intended effect around OWASP LLM Top 10 2026. Operations then observes the transition between tool permission and least privilege, while security checks that OWASP LLM Top 10 2026 receives neither implicit authority nor unnecessary data. If the least privilege verification fails, rollback restores the configuration around OWASP LLM Top 10 2026, replays owasp-llm-2026-excessive-agency-c81, and compares the new state with the control evidence from excessive agency. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c82 starts at authorization and treats tool permission as an explicit boundary rather than an implicit assumption. The first control requires least privilege to emit an observable result before OWASP LLM Top 10 2026 can trigger the intended effect around excessive agency. The conclusion stays bounded by least privilege and excessive agency: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c82 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns authorization into a reviewable decision point with a named input and a retained output. To test tool permission, fixture owasp-llm-2026-excessive-agency-c82 contains both an allowed state and a rejected state; rejection must occur before any change attributed to least privilege.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c83 starts at tool permission and treats least privilege as an explicit boundary rather than an implicit assumption. The first control requires OWASP LLM Top 10 2026 to emit an observable result before excessive agency can trigger the intended effect around authorization. Operations then observes the transition between OWASP LLM Top 10 2026 and excessive agency, while security checks that authorization receives neither implicit authority nor unnecessary data. If the excessive agency verification fails, rollback restores the configuration around authorization, replays owasp-llm-2026-excessive-agency-c83, and compares the new state with the control evidence from tool permission. This detail makes “OWASP LLM Top 10 2026: test excessive agency as an authorization failure” reviewable because each operational statement points to least privilege, a concrete condition, and evidence instead of a generic assurance.
In “OWASP LLM Top 10 2026: test excessive agency as an authorization failure”, scenario owasp-llm-2026-excessive-agency-c84 starts at least privilege and treats OWASP LLM Top 10 2026 as an explicit boundary rather than an implicit assumption. The first control requires excessive agency to emit an observable result before authorization can trigger the intended effect around tool permission. The conclusion stays bounded by excessive agency and tool permission: anything not demonstrated by scenario owasp-llm-2026-excessive-agency-c84 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Model excessive agency as a mismatch between model capability, tool permissions and business authorization. It turns least privilege into a reviewable decision point with a named input and a retained output. To test OWASP LLM Top 10 2026, fixture owasp-llm-2026-excessive-agency-c84 contains both an allowed state and a rejected state; rejection must occur before any change attributed to excessive agency.
Evidence point: OWASP documents that the 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around OWASP LLM Top 10 2026 has an input, a rule, a rejection behavior, and evidence.
- The control around excessive agency has an input, a rule, a rejection behavior, and evidence.
- The control around authorization has an input, a rule, a rejection behavior, and evidence.
- The control around tool permission has an input, a rule, a rejection behavior, and evidence.
- The control around least privilege has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] Authorization - Model Context Protocol — For HTTP authorization, MCP requires resource-bound tokens, server-side audience validation and PKCE, and forbids insecure token passthrough patterns. source
- [S2] OWASP API Security Top 10 2023 — OWASP API Security Top 10 2023 highlights authorization failures, authentication weaknesses, resource abuse, SSRF, misconfiguration and unsafe API consumption. source
- [S3] Authentication Cheat Sheet — OWASP authentication guidance separates identity proofing, authentication and session management and recommends strong controls for sensitive operations. source
- [S4] Content Security Policy Cheat Sheet — OWASP recommends strict CSP designs based on nonces or hashes instead of large static allowlists. source
- [S5] Artificial Intelligence Risk Management Framework: Generative AI Profile — NIST AI 600-1 is a generative-AI profile for integrating trustworthiness and risk actions across the AI lifecycle. source
- [S6] AI Risk Management Framework — NIST positions the AI RMF as a voluntary framework for managing AI risks and is revising it while adding profiles for specific settings. source
- [S7] OWASP Top 10 for Large Language Model Applications — OWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. source
- [S8] OWASP Top 10 for LLM Applications 2025 — The 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. source
- [S9] REST Security Cheat Sheet — OWASP REST guidance emphasizes HTTPS, explicit access control and careful handling of tokens, methods, inputs and security headers. source
- [S10] Web Authentication Level 3 — WebAuthn Level 3 defines strong public-key credentials scoped to relying parties and reached Candidate Recommendation Snapshot status in May 2026. source



Comments
No published comment yet.
Sign in to comment