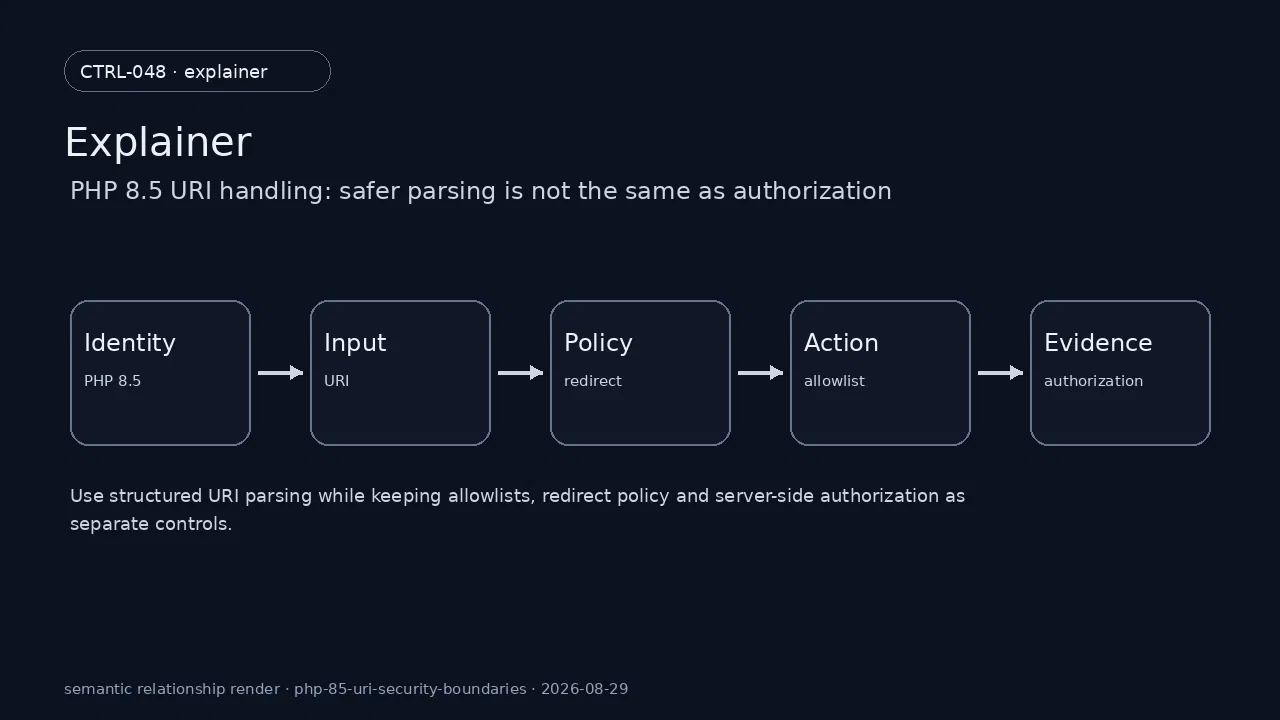
PHP 8.5 URI handling: safer parsing is not the same as authorization addresses one concrete problem: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. The guide works from the actual objects — PHP 8.5, URI, redirect, allowlist, authorization — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: PHP 8.5 meets URI
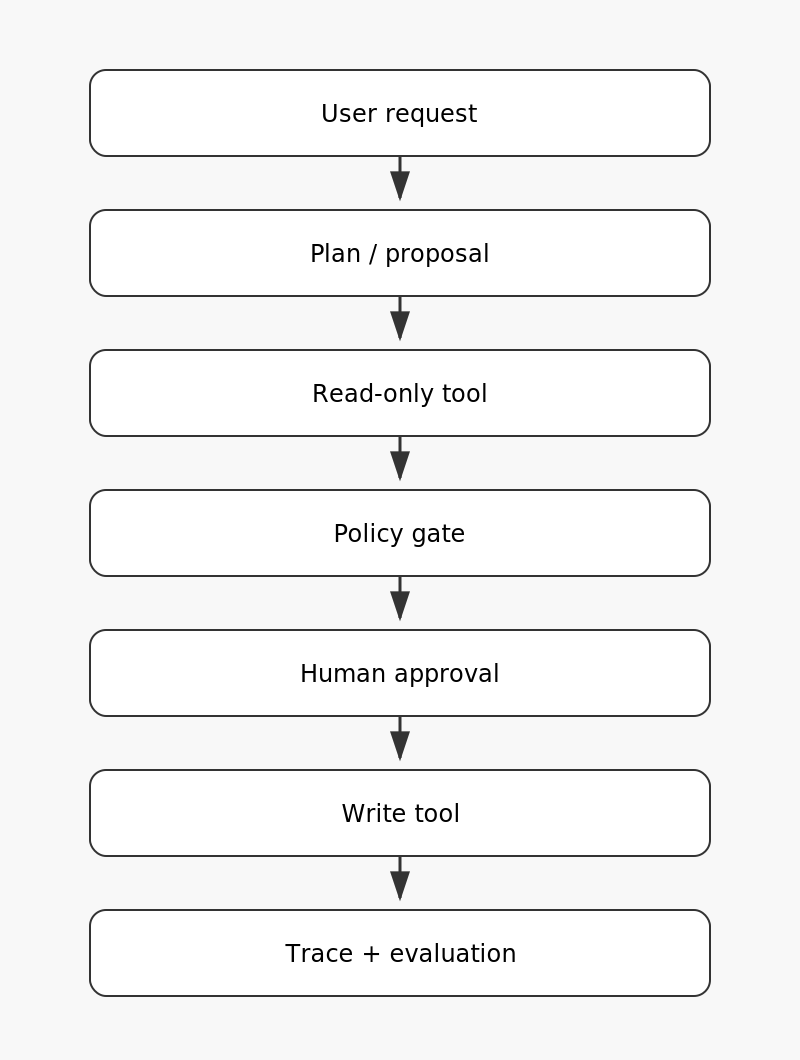
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c11 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. To test allowlist, fixture php-85-uri-security-boundaries-c11 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization. Operations then observes the transition between authorization and PHP 8.5, while security checks that URI receives neither implicit authority nor unnecessary data. If the PHP 8.5 verification fails, rollback restores the configuration around URI, replays php-85-uri-security-boundaries-c11, and compares the new state with the control evidence from redirect.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c12 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by PHP 8.5 and redirect: anything not demonstrated by scenario php-85-uri-security-boundaries-c12 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns allowlist into a reviewable decision point with a named input and a retained output.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c13 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. To test PHP 8.5, fixture php-85-uri-security-boundaries-c13 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URI. Operations then observes the transition between URI and redirect, while security checks that allowlist receives neither implicit authority nor unnecessary data. If the redirect verification fails, rollback restores the configuration around allowlist, replays php-85-uri-security-boundaries-c13, and compares the new state with the control evidence from authorization.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c14 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to URI, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by redirect and authorization: anything not demonstrated by scenario php-85-uri-security-boundaries-c14 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns PHP 8.5 into a reviewable decision point with a named input and a retained output.

Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c21 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns allowlist into a reviewable decision point with a named input and a retained output. To test authorization, fixture php-85-uri-security-boundaries-c21 contains both an allowed state and a rejected state; rejection must occur before any change attributed to PHP 8.5. Operations then observes the transition between PHP 8.5 and URI, while security checks that redirect receives neither implicit authority nor unnecessary data.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c22 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. If the redirect verification fails, rollback restores the configuration around allowlist, replays php-85-uri-security-boundaries-c22, and compares the new state with the control evidence from authorization. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to PHP 8.5, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by URI and allowlist: anything not demonstrated by scenario php-85-uri-security-boundaries-c22 is labeled as a limitation or inference, never promoted to fact.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c23 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns PHP 8.5 into a reviewable decision point with a named input and a retained output. To test URI, fixture php-85-uri-security-boundaries-c23 contains both an allowed state and a rejected state; rejection must occur before any change attributed to redirect. Operations then observes the transition between redirect and allowlist, while security checks that authorization receives neither implicit authority nor unnecessary data.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c24 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. If the authorization verification fails, rollback restores the configuration around PHP 8.5, replays php-85-uri-security-boundaries-c24, and compares the new state with the control evidence from URI. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to redirect, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by allowlist and PHP 8.5: anything not demonstrated by scenario php-85-uri-security-boundaries-c24 is labeled as a limitation or inference, never promoted to fact.
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c31 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. The conclusion stays bounded by URI and allowlist: anything not demonstrated by scenario php-85-uri-security-boundaries-c31 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns authorization into a reviewable decision point with a named input and a retained output. To test PHP 8.5, fixture php-85-uri-security-boundaries-c31 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URI.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c32 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. Operations then observes the transition between redirect and allowlist, while security checks that authorization receives neither implicit authority nor unnecessary data. If the allowlist verification fails, rollback restores the configuration around authorization, replays php-85-uri-security-boundaries-c32, and compares the new state with the control evidence from PHP 8.5. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to URI, a concrete condition, and evidence instead of a generic assurance.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c33 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. The conclusion stays bounded by allowlist and PHP 8.5: anything not demonstrated by scenario php-85-uri-security-boundaries-c33 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns URI into a reviewable decision point with a named input and a retained output. To test redirect, fixture php-85-uri-security-boundaries-c33 contains both an allowed state and a rejected state; rejection must occur before any change attributed to allowlist.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c34 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. Operations then observes the transition between authorization and PHP 8.5, while security checks that URI receives neither implicit authority nor unnecessary data. If the PHP 8.5 verification fails, rollback restores the configuration around URI, replays php-85-uri-security-boundaries-c34, and compares the new state with the control evidence from redirect. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to allowlist, a concrete condition, and evidence instead of a generic assurance.

Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c41 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to URI, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by redirect and authorization: anything not demonstrated by scenario php-85-uri-security-boundaries-c41 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns PHP 8.5 into a reviewable decision point with a named input and a retained output.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c42 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. To test redirect, fixture php-85-uri-security-boundaries-c42 contains both an allowed state and a rejected state; rejection must occur before any change attributed to allowlist. Operations then observes the transition between allowlist and authorization, while security checks that PHP 8.5 receives neither implicit authority nor unnecessary data. If the authorization verification fails, rollback restores the configuration around PHP 8.5, replays php-85-uri-security-boundaries-c42, and compares the new state with the control evidence from URI.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c43 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to allowlist, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization and URI: anything not demonstrated by scenario php-85-uri-security-boundaries-c43 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns redirect into a reviewable decision point with a named input and a retained output.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c44 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. To test authorization, fixture php-85-uri-security-boundaries-c44 contains both an allowed state and a rejected state; rejection must occur before any change attributed to PHP 8.5. Operations then observes the transition between PHP 8.5 and URI, while security checks that redirect receives neither implicit authority nor unnecessary data. If the URI verification fails, rollback restores the configuration around redirect, replays php-85-uri-security-boundaries-c44, and compares the new state with the control evidence from allowlist.

Trust boundaries around redirect
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c51 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. If the authorization verification fails, rollback restores the configuration around PHP 8.5, replays php-85-uri-security-boundaries-c51, and compares the new state with the control evidence from URI. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to redirect, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by allowlist and PHP 8.5: anything not demonstrated by scenario php-85-uri-security-boundaries-c51 is labeled as a limitation or inference, never promoted to fact.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c52 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns redirect into a reviewable decision point with a named input and a retained output. To test allowlist, fixture php-85-uri-security-boundaries-c52 contains both an allowed state and a rejected state; rejection must occur before any change attributed to authorization. Operations then observes the transition between authorization and PHP 8.5, while security checks that URI receives neither implicit authority nor unnecessary data.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c53 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. If the URI verification fails, rollback restores the configuration around redirect, replays php-85-uri-security-boundaries-c53, and compares the new state with the control evidence from allowlist. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to authorization, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by PHP 8.5 and redirect: anything not demonstrated by scenario php-85-uri-security-boundaries-c53 is labeled as a limitation or inference, never promoted to fact.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c54 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns authorization into a reviewable decision point with a named input and a retained output. To test PHP 8.5, fixture php-85-uri-security-boundaries-c54 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URI. Operations then observes the transition between URI and redirect, while security checks that allowlist receives neither implicit authority nor unnecessary data.

Build the decision path with allowlist
The starting point is not a feature; it is an observable decision boundary.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c61 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. Operations then observes the transition between authorization and PHP 8.5, while security checks that URI receives neither implicit authority nor unnecessary data. If the PHP 8.5 verification fails, rollback restores the configuration around URI, replays php-85-uri-security-boundaries-c61, and compares the new state with the control evidence from redirect. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to allowlist, a concrete condition, and evidence instead of a generic assurance.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c62 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. The conclusion stays bounded by PHP 8.5 and redirect: anything not demonstrated by scenario php-85-uri-security-boundaries-c62 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns allowlist into a reviewable decision point with a named input and a retained output. To test authorization, fixture php-85-uri-security-boundaries-c62 contains both an allowed state and a rejected state; rejection must occur before any change attributed to PHP 8.5.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c63 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. Operations then observes the transition between URI and redirect, while security checks that allowlist receives neither implicit authority nor unnecessary data. If the redirect verification fails, rollback restores the configuration around allowlist, replays php-85-uri-security-boundaries-c63, and compares the new state with the control evidence from authorization. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to PHP 8.5, a concrete condition, and evidence instead of a generic assurance.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c64 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. The conclusion stays bounded by redirect and authorization: anything not demonstrated by scenario php-85-uri-security-boundaries-c64 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns PHP 8.5 into a reviewable decision point with a named input and a retained output. To test URI, fixture php-85-uri-security-boundaries-c64 contains both an allowed state and a rejected state; rejection must occur before any change attributed to redirect.
Verify authorization with observable evidence
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c71 starts at allowlist and treats authorization as an explicit boundary rather than an implicit assumption. The first control requires PHP 8.5 to emit an observable result before URI can trigger the intended effect around redirect. To test authorization, fixture php-85-uri-security-boundaries-c71 contains both an allowed state and a rejected state; rejection must occur before any change attributed to PHP 8.5. Operations then observes the transition between PHP 8.5 and URI, while security checks that redirect receives neither implicit authority nor unnecessary data. If the URI verification fails, rollback restores the configuration around redirect, replays php-85-uri-security-boundaries-c71, and compares the new state with the control evidence from allowlist.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c72 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to PHP 8.5, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by URI and allowlist: anything not demonstrated by scenario php-85-uri-security-boundaries-c72 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns authorization into a reviewable decision point with a named input and a retained output.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c73 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. To test URI, fixture php-85-uri-security-boundaries-c73 contains both an allowed state and a rejected state; rejection must occur before any change attributed to redirect. Operations then observes the transition between redirect and allowlist, while security checks that authorization receives neither implicit authority nor unnecessary data. If the allowlist verification fails, rollback restores the configuration around authorization, replays php-85-uri-security-boundaries-c73, and compares the new state with the control evidence from PHP 8.5.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c74 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to redirect, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by allowlist and PHP 8.5: anything not demonstrated by scenario php-85-uri-security-boundaries-c74 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns URI into a reviewable decision point with a named input and a retained output.
Evidence point: OWASP documents that oWASP recommends strict CSP designs based on nonces or hashes instead of large static allowlists. This source anchors verify authorization with observable evidence but does not replace local verification. [S7]Controls that remain after launch
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c81 starts at authorization and treats PHP 8.5 as an explicit boundary rather than an implicit assumption. The first control requires URI to emit an observable result before redirect can trigger the intended effect around allowlist. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns authorization into a reviewable decision point with a named input and a retained output. To test PHP 8.5, fixture php-85-uri-security-boundaries-c81 contains both an allowed state and a rejected state; rejection must occur before any change attributed to URI. Operations then observes the transition between URI and redirect, while security checks that allowlist receives neither implicit authority nor unnecessary data.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c82 starts at PHP 8.5 and treats URI as an explicit boundary rather than an implicit assumption. The first control requires redirect to emit an observable result before allowlist can trigger the intended effect around authorization. If the allowlist verification fails, rollback restores the configuration around authorization, replays php-85-uri-security-boundaries-c82, and compares the new state with the control evidence from PHP 8.5. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to URI, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by redirect and authorization: anything not demonstrated by scenario php-85-uri-security-boundaries-c82 is labeled as a limitation or inference, never promoted to fact.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c83 starts at URI and treats redirect as an explicit boundary rather than an implicit assumption. The first control requires allowlist to emit an observable result before authorization can trigger the intended effect around PHP 8.5. That sequence serves this concrete job: Use structured URI parsing while keeping allowlists, redirect policy and server-side authorization as separate controls. It turns URI into a reviewable decision point with a named input and a retained output. To test redirect, fixture php-85-uri-security-boundaries-c83 contains both an allowed state and a rejected state; rejection must occur before any change attributed to allowlist. Operations then observes the transition between allowlist and authorization, while security checks that PHP 8.5 receives neither implicit authority nor unnecessary data.
In “PHP 8.5 URI handling: safer parsing is not the same as authorization”, scenario php-85-uri-security-boundaries-c84 starts at redirect and treats allowlist as an explicit boundary rather than an implicit assumption. The first control requires authorization to emit an observable result before PHP 8.5 can trigger the intended effect around URI. If the PHP 8.5 verification fails, rollback restores the configuration around URI, replays php-85-uri-security-boundaries-c84, and compares the new state with the control evidence from redirect. This detail makes “PHP 8.5 URI handling: safer parsing is not the same as authorization” reviewable because each operational statement points to allowlist, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by authorization and URI: anything not demonstrated by scenario php-85-uri-security-boundaries-c84 is labeled as a limitation or inference, never promoted to fact.
Evidence point: GitHub documents that the dependency review action can fail pull requests based on vulnerability severity, dependency scope or license rules. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around PHP 8.5 has an input, a rule, a rejection behavior, and evidence.
- The control around URI has an input, a rule, a rejection behavior, and evidence.
- The control around redirect has an input, a rule, a rejection behavior, and evidence.
- The control around allowlist has an input, a rule, a rejection behavior, and evidence.
- The control around authorization has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] Migrating from PHP 8.3.x to PHP 8.4.x — PHP 8.4 introduces new features together with backward-incompatible and deprecated behavior that should be tested before production rollout. source
- [S2] REST Security Cheat Sheet — OWASP REST guidance emphasizes HTTPS, explicit access control and careful handling of tokens, methods, inputs and security headers. source
- [S3] Policies - Kubernetes — Kubernetes policy objects include NetworkPolicies for traffic controls and admission mechanisms for validating or mutating API requests. source
- [S4] PHP 8.5 Release Announcement — PHP 8.5 adds the URI extension, pipe operator, clone-with syntax and additional language/runtime improvements. source
- [S5] Authorization - Model Context Protocol — For HTTP authorization, MCP requires resource-bound tokens, server-side audience validation and PKCE, and forbids insecure token passthrough patterns. source
- [S6] Authentication Cheat Sheet — OWASP authentication guidance separates identity proofing, authentication and session management and recommends strong controls for sensitive operations. source
- [S7] Content Security Policy Cheat Sheet — OWASP recommends strict CSP designs based on nonces or hashes instead of large static allowlists. source
- [S8] Configuring the dependency review action — The dependency review action can fail pull requests based on vulnerability severity, dependency scope or license rules. source
- [S9] OpenAI Agents SDK — The Agents SDK is a higher-level runtime around model calls that manages tools, guardrails, handoffs, sessions and tracing. source
- [S10] Agents - OpenAI Agents SDK — An Agent combines instructions, tools and optional runtime behavior such as handoffs, guardrails and structured outputs. source



Comments
No published comment yet.
Sign in to comment