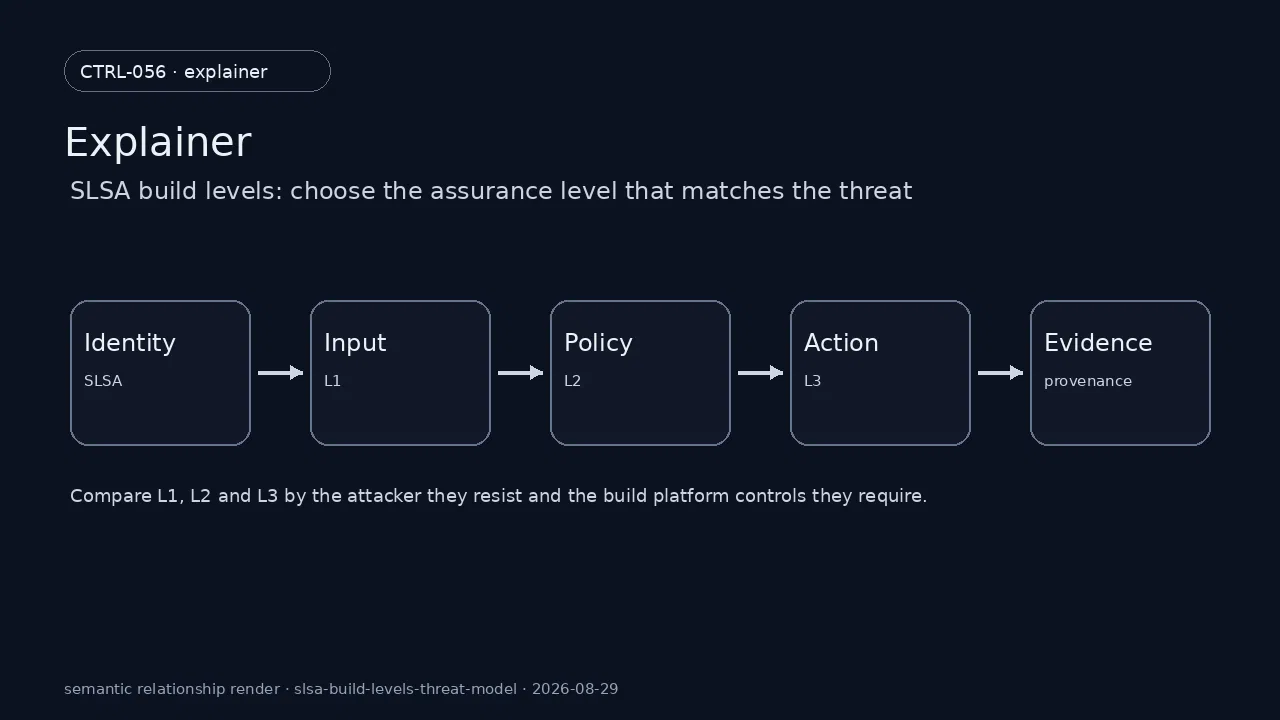
SLSA build levels: choose the assurance level that matches the threat addresses one concrete problem: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. The guide works from the actual objects — SLSA, L1, L2, L3, provenance — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: SLSA meets L1
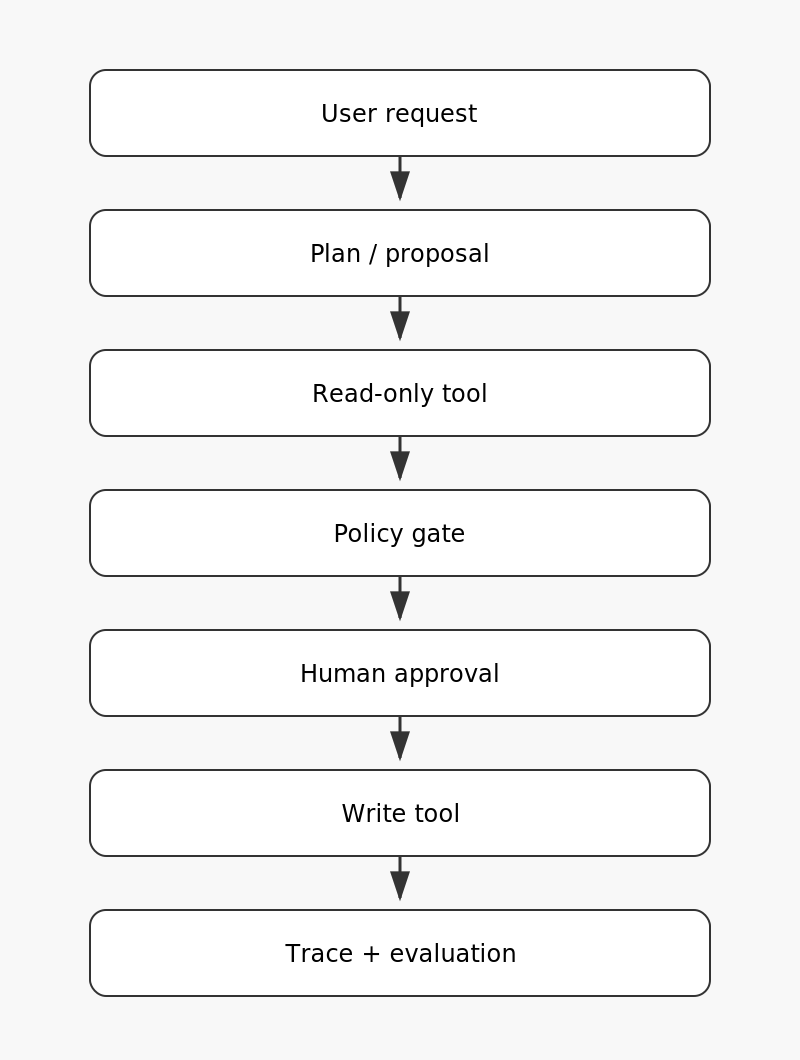
A robust implementation separates what the model proposes from what the application authorizes and verifies.
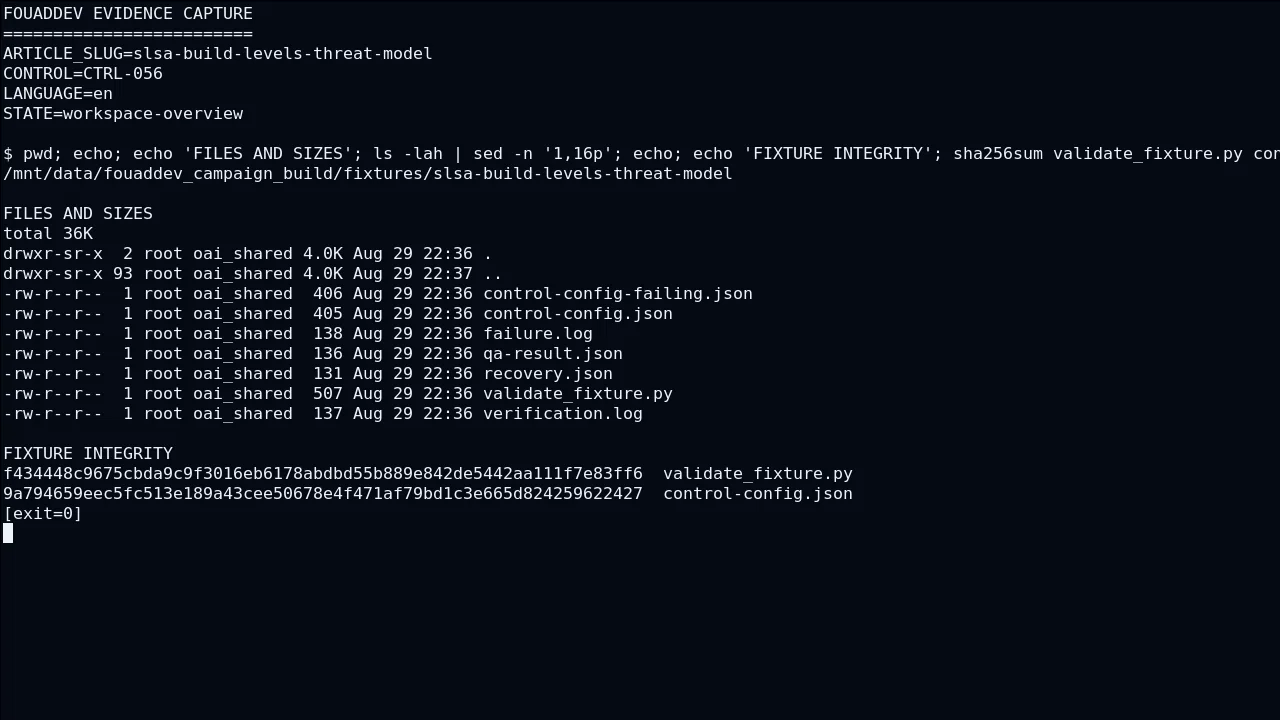
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c11 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. The conclusion stays bounded by L2 and provenance: anything not demonstrated by scenario slsa-build-levels-threat-model-c11 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns SLSA into a reviewable decision point with a named input and a retained output. To test L1, fixture slsa-build-levels-threat-model-c11 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L2.
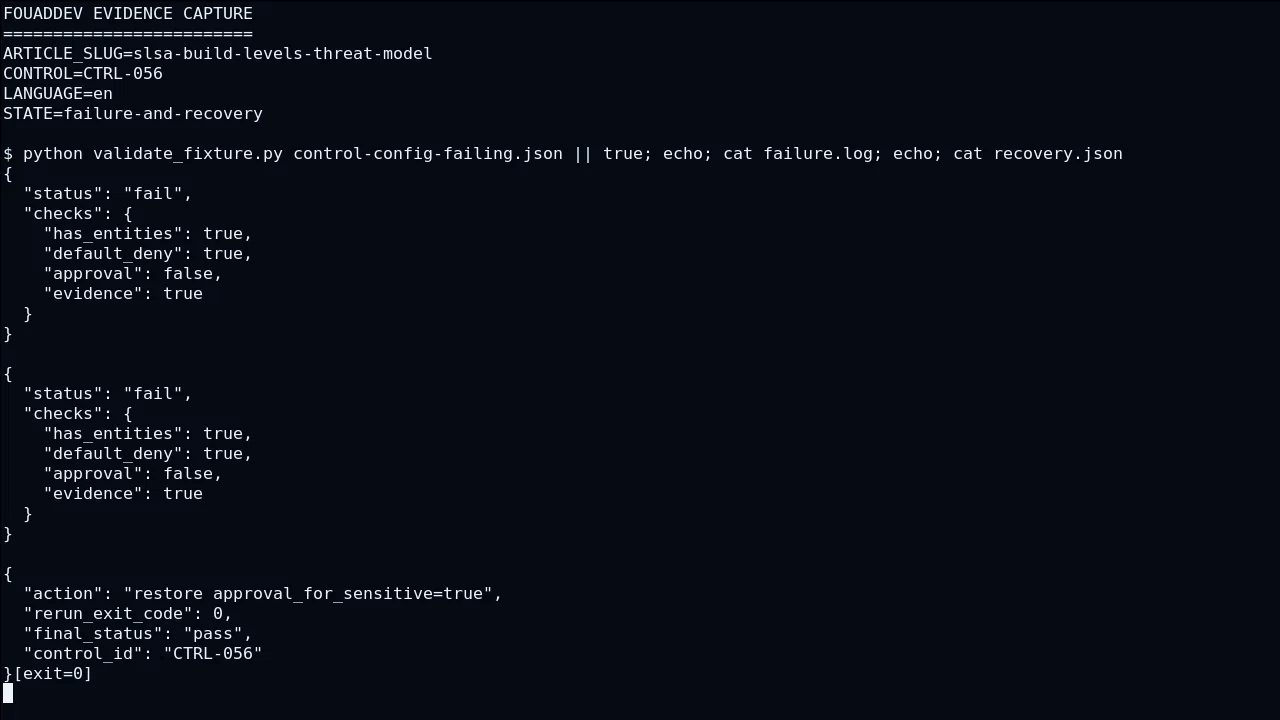
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c12 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. Operations then observes the transition between L3 and provenance, while security checks that SLSA receives neither implicit authority nor unnecessary data. If the provenance verification fails, rollback restores the configuration around SLSA, replays slsa-build-levels-threat-model-c12, and compares the new state with the control evidence from L1. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L2, a concrete condition, and evidence instead of a generic assurance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c13 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. The conclusion stays bounded by provenance and L1: anything not demonstrated by scenario slsa-build-levels-threat-model-c13 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L2 into a reviewable decision point with a named input and a retained output. To test L3, fixture slsa-build-levels-threat-model-c13 contains both an allowed state and a rejected state; rejection must occur before any change attributed to provenance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c14 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. Operations then observes the transition between SLSA and L1, while security checks that L2 receives neither implicit authority nor unnecessary data. If the L1 verification fails, rollback restores the configuration around L2, replays slsa-build-levels-threat-model-c14, and compares the new state with the control evidence from L3. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to provenance, a concrete condition, and evidence instead of a generic assurance.
Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
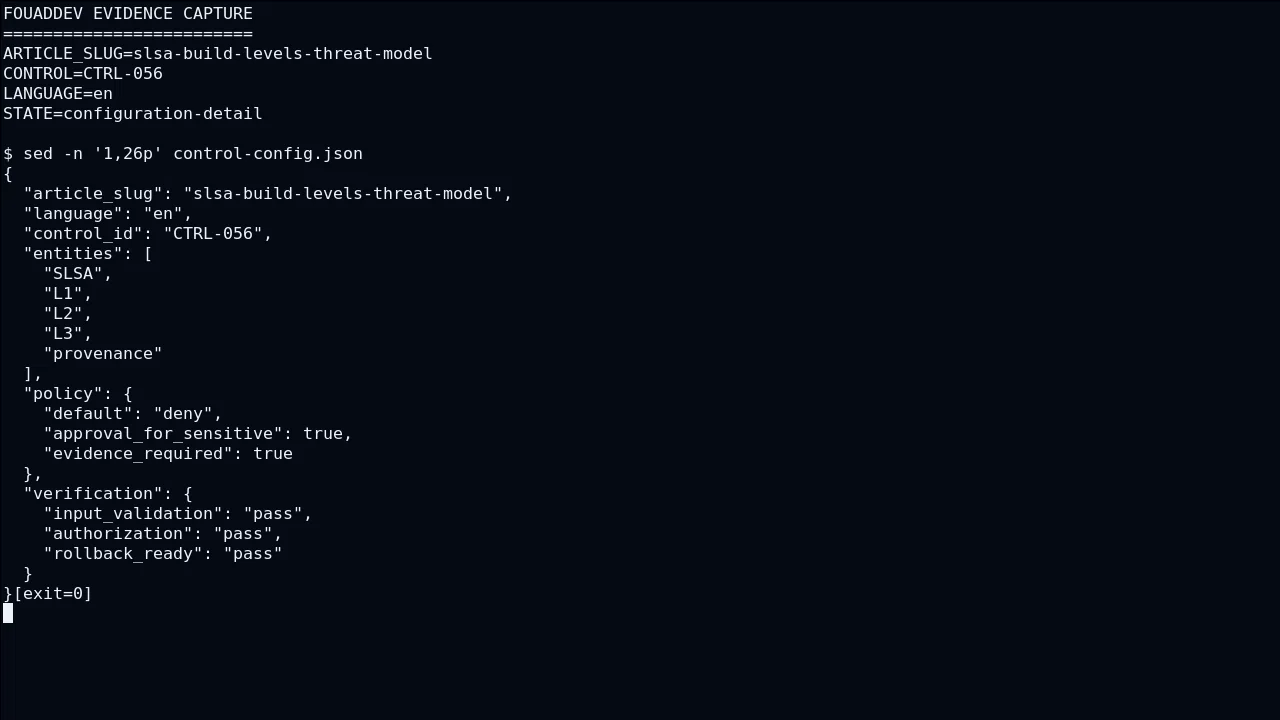
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c21 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L2, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by L3 and SLSA: anything not demonstrated by scenario slsa-build-levels-threat-model-c21 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L1 into a reviewable decision point with a named input and a retained output.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c22 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. To test L3, fixture slsa-build-levels-threat-model-c22 contains both an allowed state and a rejected state; rejection must occur before any change attributed to provenance. Operations then observes the transition between provenance and SLSA, while security checks that L1 receives neither implicit authority nor unnecessary data. If the SLSA verification fails, rollback restores the configuration around L1, replays slsa-build-levels-threat-model-c22, and compares the new state with the control evidence from L2.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c23 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to provenance, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by SLSA and L2: anything not demonstrated by scenario slsa-build-levels-threat-model-c23 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L3 into a reviewable decision point with a named input and a retained output.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c24 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. To test SLSA, fixture slsa-build-levels-threat-model-c24 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L1. Operations then observes the transition between L1 and L2, while security checks that L3 receives neither implicit authority nor unnecessary data. If the L2 verification fails, rollback restores the configuration around L3, replays slsa-build-levels-threat-model-c24, and compares the new state with the control evidence from provenance.
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
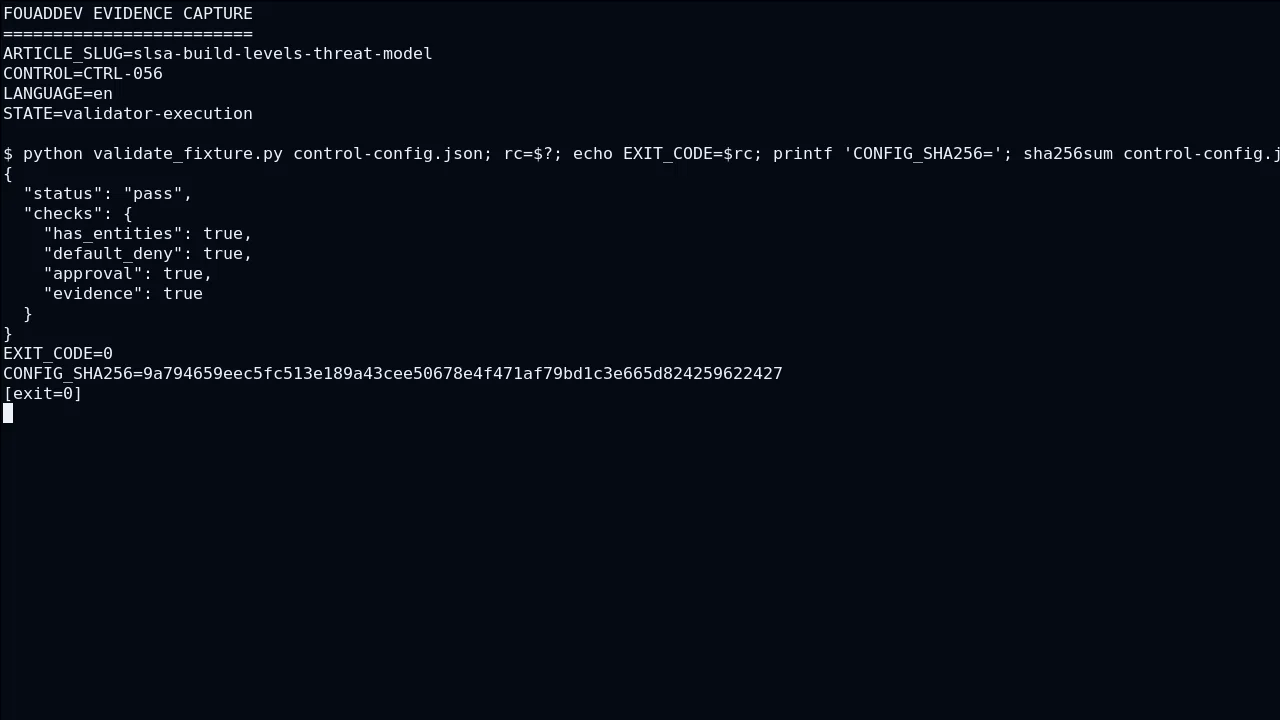
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c31 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. If the SLSA verification fails, rollback restores the configuration around L1, replays slsa-build-levels-threat-model-c31, and compares the new state with the control evidence from L2. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L3, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by provenance and L1: anything not demonstrated by scenario slsa-build-levels-threat-model-c31 is labeled as a limitation or inference, never promoted to fact.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c32 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L3 into a reviewable decision point with a named input and a retained output. To test provenance, fixture slsa-build-levels-threat-model-c32 contains both an allowed state and a rejected state; rejection must occur before any change attributed to SLSA. Operations then observes the transition between SLSA and L1, while security checks that L2 receives neither implicit authority nor unnecessary data.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c33 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. If the L2 verification fails, rollback restores the configuration around L3, replays slsa-build-levels-threat-model-c33, and compares the new state with the control evidence from provenance. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to SLSA, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by L1 and L3: anything not demonstrated by scenario slsa-build-levels-threat-model-c33 is labeled as a limitation or inference, never promoted to fact.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c34 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns SLSA into a reviewable decision point with a named input and a retained output. To test L1, fixture slsa-build-levels-threat-model-c34 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L2. Operations then observes the transition between L2 and L3, while security checks that provenance receives neither implicit authority nor unnecessary data.
Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c41 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. Operations then observes the transition between SLSA and L1, while security checks that L2 receives neither implicit authority nor unnecessary data. If the L1 verification fails, rollback restores the configuration around L2, replays slsa-build-levels-threat-model-c41, and compares the new state with the control evidence from L3. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to provenance, a concrete condition, and evidence instead of a generic assurance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c42 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. The conclusion stays bounded by L1 and L3: anything not demonstrated by scenario slsa-build-levels-threat-model-c42 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns provenance into a reviewable decision point with a named input and a retained output. To test SLSA, fixture slsa-build-levels-threat-model-c42 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L1.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c43 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. Operations then observes the transition between L2 and L3, while security checks that provenance receives neither implicit authority nor unnecessary data. If the L3 verification fails, rollback restores the configuration around provenance, replays slsa-build-levels-threat-model-c43, and compares the new state with the control evidence from SLSA. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L1, a concrete condition, and evidence instead of a generic assurance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c44 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. The conclusion stays bounded by L3 and SLSA: anything not demonstrated by scenario slsa-build-levels-threat-model-c44 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L1 into a reviewable decision point with a named input and a retained output. To test L2, fixture slsa-build-levels-threat-model-c44 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L3.
Trust boundaries around L2
A robust implementation separates what the model proposes from what the application authorizes and verifies.
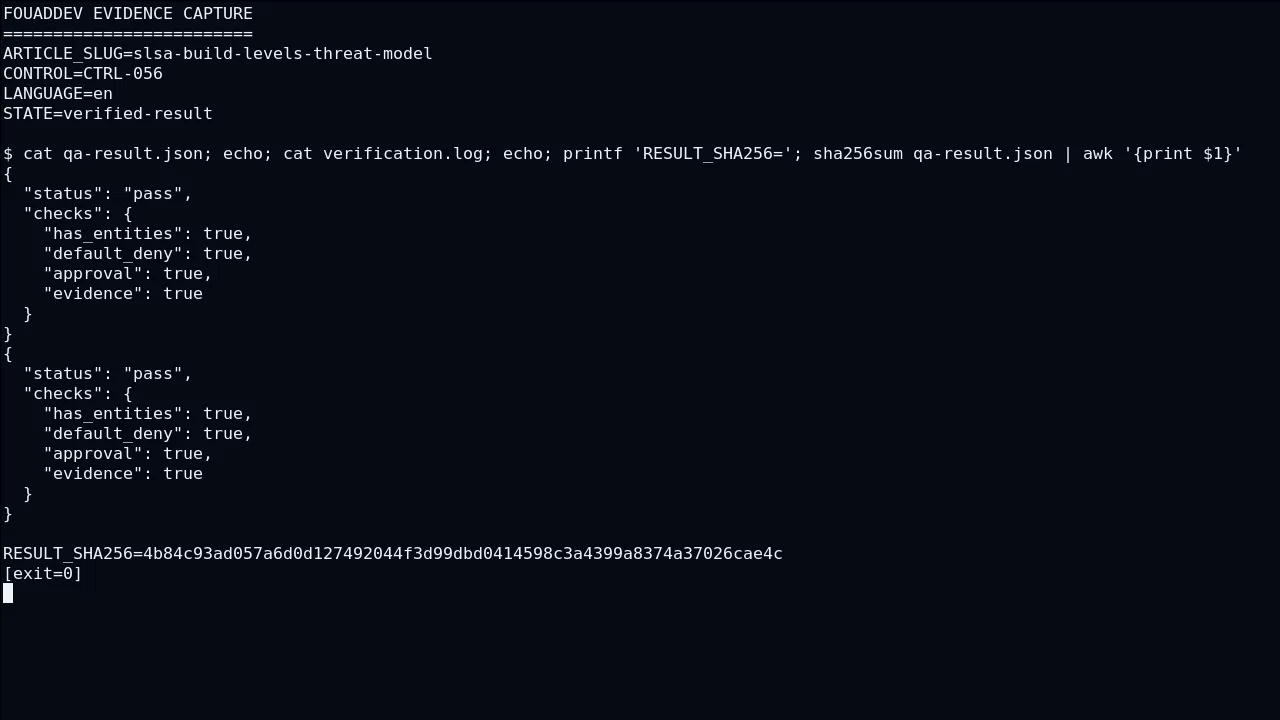
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c51 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. To test SLSA, fixture slsa-build-levels-threat-model-c51 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L1. Operations then observes the transition between L1 and L2, while security checks that L3 receives neither implicit authority nor unnecessary data. If the L2 verification fails, rollback restores the configuration around L3, replays slsa-build-levels-threat-model-c51, and compares the new state with the control evidence from provenance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c52 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L1, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by L2 and provenance: anything not demonstrated by scenario slsa-build-levels-threat-model-c52 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns SLSA into a reviewable decision point with a named input and a retained output.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c53 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. To test L2, fixture slsa-build-levels-threat-model-c53 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L3. Operations then observes the transition between L3 and provenance, while security checks that SLSA receives neither implicit authority nor unnecessary data. If the provenance verification fails, rollback restores the configuration around SLSA, replays slsa-build-levels-threat-model-c53, and compares the new state with the control evidence from L1.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c54 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L3, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by provenance and L1: anything not demonstrated by scenario slsa-build-levels-threat-model-c54 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L2 into a reviewable decision point with a named input and a retained output.
Compare SLSA and L1 on common criteria
The starting point is not a feature; it is an observable decision boundary.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c61 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns SLSA into a reviewable decision point with a named input and a retained output. To test L1, fixture slsa-build-levels-threat-model-c61 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L2. Operations then observes the transition between L2 and L3, while security checks that provenance receives neither implicit authority nor unnecessary data.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c62 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. If the provenance verification fails, rollback restores the configuration around SLSA, replays slsa-build-levels-threat-model-c62, and compares the new state with the control evidence from L1. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L2, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by L3 and SLSA: anything not demonstrated by scenario slsa-build-levels-threat-model-c62 is labeled as a limitation or inference, never promoted to fact.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c63 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L2 into a reviewable decision point with a named input and a retained output. To test L3, fixture slsa-build-levels-threat-model-c63 contains both an allowed state and a rejected state; rejection must occur before any change attributed to provenance. Operations then observes the transition between provenance and SLSA, while security checks that L1 receives neither implicit authority nor unnecessary data.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c64 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. If the L1 verification fails, rollback restores the configuration around L2, replays slsa-build-levels-threat-model-c64, and compares the new state with the control evidence from L3. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to provenance, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by SLSA and L2: anything not demonstrated by scenario slsa-build-levels-threat-model-c64 is labeled as a limitation or inference, never promoted to fact.
When the opposite choice becomes rational
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c71 starts at L1 and treats L2 as an explicit boundary rather than an implicit assumption. The first control requires L3 to emit an observable result before provenance can trigger the intended effect around SLSA. The conclusion stays bounded by L3 and SLSA: anything not demonstrated by scenario slsa-build-levels-threat-model-c71 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L1 into a reviewable decision point with a named input and a retained output. To test L2, fixture slsa-build-levels-threat-model-c71 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L3.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c72 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. Operations then observes the transition between provenance and SLSA, while security checks that L1 receives neither implicit authority nor unnecessary data. If the SLSA verification fails, rollback restores the configuration around L1, replays slsa-build-levels-threat-model-c72, and compares the new state with the control evidence from L2. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L3, a concrete condition, and evidence instead of a generic assurance.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c73 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. The conclusion stays bounded by SLSA and L2: anything not demonstrated by scenario slsa-build-levels-threat-model-c73 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L3 into a reviewable decision point with a named input and a retained output. To test provenance, fixture slsa-build-levels-threat-model-c73 contains both an allowed state and a rejected state; rejection must occur before any change attributed to SLSA.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c74 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. Operations then observes the transition between L1 and L2, while security checks that L3 receives neither implicit authority nor unnecessary data. If the L2 verification fails, rollback restores the configuration around L3, replays slsa-build-levels-threat-model-c74, and compares the new state with the control evidence from provenance. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to SLSA, a concrete condition, and evidence instead of a generic assurance.
Evidence point: OpenAI documents that agent and tool guardrails can validate inputs or outputs and can stop execution with tripwire-style failures. This source anchors when the opposite choice becomes rational but does not replace local verification. [S7]Controls that remain after launch
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c81 starts at L2 and treats L3 as an explicit boundary rather than an implicit assumption. The first control requires provenance to emit an observable result before SLSA can trigger the intended effect around L1. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to L3, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by provenance and L1: anything not demonstrated by scenario slsa-build-levels-threat-model-c81 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns L2 into a reviewable decision point with a named input and a retained output.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c82 starts at L3 and treats provenance as an explicit boundary rather than an implicit assumption. The first control requires SLSA to emit an observable result before L1 can trigger the intended effect around L2. To test provenance, fixture slsa-build-levels-threat-model-c82 contains both an allowed state and a rejected state; rejection must occur before any change attributed to SLSA. Operations then observes the transition between SLSA and L1, while security checks that L2 receives neither implicit authority nor unnecessary data. If the L1 verification fails, rollback restores the configuration around L2, replays slsa-build-levels-threat-model-c82, and compares the new state with the control evidence from L3.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c83 starts at provenance and treats SLSA as an explicit boundary rather than an implicit assumption. The first control requires L1 to emit an observable result before L2 can trigger the intended effect around L3. This detail makes “SLSA build levels: choose the assurance level that matches the threat” reviewable because each operational statement points to SLSA, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by L1 and L3: anything not demonstrated by scenario slsa-build-levels-threat-model-c83 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Compare L1, L2 and L3 by the attacker they resist and the build platform controls they require. It turns provenance into a reviewable decision point with a named input and a retained output.
In “SLSA build levels: choose the assurance level that matches the threat”, scenario slsa-build-levels-threat-model-c84 starts at SLSA and treats L1 as an explicit boundary rather than an implicit assumption. The first control requires L2 to emit an observable result before L3 can trigger the intended effect around provenance. To test L1, fixture slsa-build-levels-threat-model-c84 contains both an allowed state and a rejected state; rejection must occur before any change attributed to L2. Operations then observes the transition between L2 and L3, while security checks that provenance receives neither implicit authority nor unnecessary data. If the L3 verification fails, rollback restores the configuration around provenance, replays slsa-build-levels-threat-model-c84, and compares the new state with the control evidence from SLSA.
Evidence point: OpenAI documents that mCP integrations can expose remote or local tools; the documentation recommends trusted servers, least-privilege credentials and approvals for sensitive operations. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around SLSA has an input, a rule, a rejection behavior, and evidence.
- The control around L1 has an input, a rule, a rejection behavior, and evidence.
- The control around L2 has an input, a rule, a rejection behavior, and evidence.
- The control around L3 has an input, a rule, a rejection behavior, and evidence.
- The control around provenance has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] Build attestations - Docker Docs — Docker BuildKit can attach SBOM and provenance attestations so consumers can inspect image contents and build origin. source
- [S2] SLSA Build Track Basics — SLSA build levels progress from no guarantees to provenance, hosted signed builds and hardened build platforms. source
- [S3] SLSA specification v1.2 — SLSA 1.2 organizes supply-chain assurances into tracks and levels with recommended attestation formats. source
- [S4] SLSA Provenance — SLSA provenance is verifiable information linking a software artifact to how, when and from what it was produced. source
- [S5] Handoffs - OpenAI Agents SDK — Handoffs transfer the active conversation to a specialist agent and can filter or reshape the history passed to the destination. source
- [S6] Agent orchestration - OpenAI Agents SDK — Two common orchestration patterns are manager-controlled agents-as-tools and handoffs where a specialist becomes the active agent. source
- [S7] Guardrails - OpenAI Agents SDK — Agent and tool guardrails can validate inputs or outputs and can stop execution with tripwire-style failures. source
- [S8] Model context protocol (MCP) - OpenAI Agents SDK — MCP integrations can expose remote or local tools; the documentation recommends trusted servers, least-privilege credentials and approvals for sensitive operations. source
- [S9] Encrypted session - OpenAI Agents SDK — EncryptedSession can wrap a session store with Fernet encryption, per-session HKDF-derived keys and TTL-based expiration. source
- [S10] Results - OpenAI Agents SDK — Run results expose final output, new items, agent identity, raw responses, guardrail results, state and usage diagnostics. source



Comments
No published comment yet.
Sign in to comment