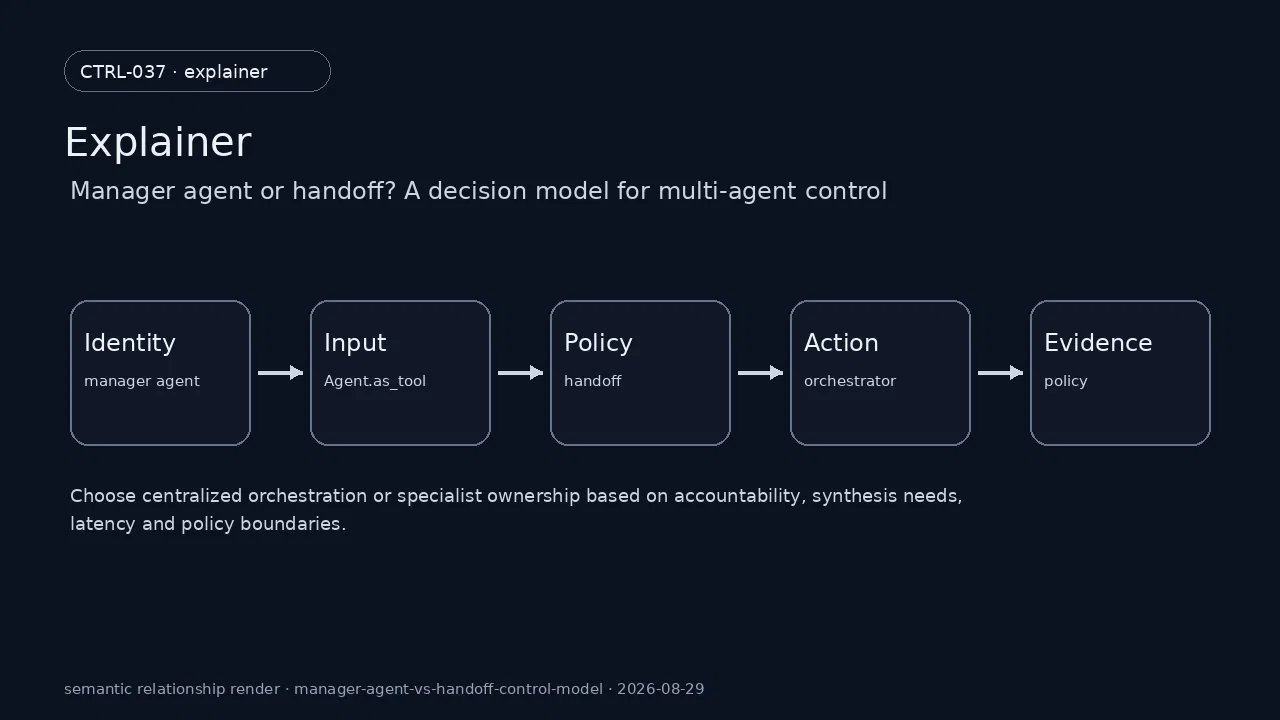
Manager agent or handoff? A decision model for multi-agent control addresses one concrete problem: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. The guide works from the actual objects — manager agent, Agent.as_tool, handoff, orchestrator, policy — and aims for a verifiable decision rather than a generic pattern.
The concrete problem: manager agent meets Agent.as_tool
The starting point is not a feature; it is an observable decision boundary.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c11 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns Agent.as_tool into a reviewable decision point with a named input and a retained output. To test handoff, fixture manager-agent-vs-handoff-control-model-c11 contains both an allowed state and a rejected state; rejection must occur before any change attributed to orchestrator. Operations then observes the transition between orchestrator and policy, while security checks that manager agent receives neither implicit authority nor unnecessary data.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c12 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. If the manager agent verification fails, rollback restores the configuration around Agent.as_tool, replays manager-agent-vs-handoff-control-model-c12, and compares the new state with the control evidence from handoff. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to orchestrator, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by policy and Agent.as_tool: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c12 is labeled as a limitation or inference, never promoted to fact.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c13 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns orchestrator into a reviewable decision point with a named input and a retained output. To test policy, fixture manager-agent-vs-handoff-control-model-c13 contains both an allowed state and a rejected state; rejection must occur before any change attributed to manager agent. Operations then observes the transition between manager agent and Agent.as_tool, while security checks that handoff receives neither implicit authority nor unnecessary data.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c14 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. If the handoff verification fails, rollback restores the configuration around orchestrator, replays manager-agent-vs-handoff-control-model-c14, and compares the new state with the control evidence from policy. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to manager agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by Agent.as_tool and orchestrator: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c14 is labeled as a limitation or inference, never promoted to fact.
Trust boundaries around handoff
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c21 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. The conclusion stays bounded by policy and Agent.as_tool: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c21 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns handoff into a reviewable decision point with a named input and a retained output. To test orchestrator, fixture manager-agent-vs-handoff-control-model-c21 contains both an allowed state and a rejected state; rejection must occur before any change attributed to policy.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c22 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. Operations then observes the transition between manager agent and Agent.as_tool, while security checks that handoff receives neither implicit authority nor unnecessary data. If the Agent.as_tool verification fails, rollback restores the configuration around handoff, replays manager-agent-vs-handoff-control-model-c22, and compares the new state with the control evidence from orchestrator. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to policy, a concrete condition, and evidence instead of a generic assurance.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c23 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. The conclusion stays bounded by Agent.as_tool and orchestrator: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c23 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns policy into a reviewable decision point with a named input and a retained output. To test manager agent, fixture manager-agent-vs-handoff-control-model-c23 contains both an allowed state and a rejected state; rejection must occur before any change attributed to Agent.as_tool.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c24 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. Operations then observes the transition between handoff and orchestrator, while security checks that policy receives neither implicit authority nor unnecessary data. If the orchestrator verification fails, rollback restores the configuration around policy, replays manager-agent-vs-handoff-control-model-c24, and compares the new state with the control evidence from manager agent. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to Agent.as_tool, a concrete condition, and evidence instead of a generic assurance.
Compare manager agent and Agent.as_tool on common criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c31 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to policy, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by manager agent and handoff: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c31 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns orchestrator into a reviewable decision point with a named input and a retained output.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c32 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. To test manager agent, fixture manager-agent-vs-handoff-control-model-c32 contains both an allowed state and a rejected state; rejection must occur before any change attributed to Agent.as_tool. Operations then observes the transition between Agent.as_tool and handoff, while security checks that orchestrator receives neither implicit authority nor unnecessary data. If the handoff verification fails, rollback restores the configuration around orchestrator, replays manager-agent-vs-handoff-control-model-c32, and compares the new state with the control evidence from policy.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c33 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to Agent.as_tool, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by handoff and policy: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c33 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns manager agent into a reviewable decision point with a named input and a retained output.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c34 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. To test handoff, fixture manager-agent-vs-handoff-control-model-c34 contains both an allowed state and a rejected state; rejection must occur before any change attributed to orchestrator. Operations then observes the transition between orchestrator and policy, while security checks that manager agent receives neither implicit authority nor unnecessary data. If the policy verification fails, rollback restores the configuration around manager agent, replays manager-agent-vs-handoff-control-model-c34, and compares the new state with the control evidence from Agent.as_tool.
When the opposite choice becomes rational
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c41 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. If the handoff verification fails, rollback restores the configuration around orchestrator, replays manager-agent-vs-handoff-control-model-c41, and compares the new state with the control evidence from policy. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to manager agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by Agent.as_tool and orchestrator: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c41 is labeled as a limitation or inference, never promoted to fact.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c42 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns manager agent into a reviewable decision point with a named input and a retained output. To test Agent.as_tool, fixture manager-agent-vs-handoff-control-model-c42 contains both an allowed state and a rejected state; rejection must occur before any change attributed to handoff. Operations then observes the transition between handoff and orchestrator, while security checks that policy receives neither implicit authority nor unnecessary data.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c43 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. If the policy verification fails, rollback restores the configuration around manager agent, replays manager-agent-vs-handoff-control-model-c43, and compares the new state with the control evidence from Agent.as_tool. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to handoff, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by orchestrator and manager agent: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c43 is labeled as a limitation or inference, never promoted to fact.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c44 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns handoff into a reviewable decision point with a named input and a retained output. To test orchestrator, fixture manager-agent-vs-handoff-control-model-c44 contains both an allowed state and a rejected state; rejection must occur before any change attributed to policy. Operations then observes the transition between policy and manager agent, while security checks that Agent.as_tool receives neither implicit authority nor unnecessary data.
Failure modes, signals, and diagnosis
The starting point is not a feature; it is an observable decision boundary.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c51 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. Operations then observes the transition between handoff and orchestrator, while security checks that policy receives neither implicit authority nor unnecessary data. If the orchestrator verification fails, rollback restores the configuration around policy, replays manager-agent-vs-handoff-control-model-c51, and compares the new state with the control evidence from manager agent. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to Agent.as_tool, a concrete condition, and evidence instead of a generic assurance.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c52 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. The conclusion stays bounded by orchestrator and manager agent: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c52 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns Agent.as_tool into a reviewable decision point with a named input and a retained output. To test handoff, fixture manager-agent-vs-handoff-control-model-c52 contains both an allowed state and a rejected state; rejection must occur before any change attributed to orchestrator.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c53 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. Operations then observes the transition between policy and manager agent, while security checks that Agent.as_tool receives neither implicit authority nor unnecessary data. If the manager agent verification fails, rollback restores the configuration around Agent.as_tool, replays manager-agent-vs-handoff-control-model-c53, and compares the new state with the control evidence from handoff. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to orchestrator, a concrete condition, and evidence instead of a generic assurance.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c54 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. The conclusion stays bounded by manager agent and handoff: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c54 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns orchestrator into a reviewable decision point with a named input and a retained output. To test policy, fixture manager-agent-vs-handoff-control-model-c54 contains both an allowed state and a rejected state; rejection must occur before any change attributed to manager agent.
Progressive rollout and rollback
A production design should make it clear who decides, what evidence is available, and what can be rolled back.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c61 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. To test handoff, fixture manager-agent-vs-handoff-control-model-c61 contains both an allowed state and a rejected state; rejection must occur before any change attributed to orchestrator. Operations then observes the transition between orchestrator and policy, while security checks that manager agent receives neither implicit authority nor unnecessary data. If the policy verification fails, rollback restores the configuration around manager agent, replays manager-agent-vs-handoff-control-model-c61, and compares the new state with the control evidence from Agent.as_tool.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c62 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to orchestrator, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by policy and Agent.as_tool: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c62 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns handoff into a reviewable decision point with a named input and a retained output.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c63 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. To test policy, fixture manager-agent-vs-handoff-control-model-c63 contains both an allowed state and a rejected state; rejection must occur before any change attributed to manager agent. Operations then observes the transition between manager agent and Agent.as_tool, while security checks that handoff receives neither implicit authority nor unnecessary data. If the Agent.as_tool verification fails, rollback restores the configuration around handoff, replays manager-agent-vs-handoff-control-model-c63, and compares the new state with the control evidence from orchestrator.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c64 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to manager agent, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by Agent.as_tool and orchestrator: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c64 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns policy into a reviewable decision point with a named input and a retained output.
Production decision criteria
The hard part appears when the happy path meets authorization, failures, and operational constraints.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c71 starts at handoff and treats orchestrator as an explicit boundary rather than an implicit assumption. The first control requires policy to emit an observable result before manager agent can trigger the intended effect around Agent.as_tool. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns handoff into a reviewable decision point with a named input and a retained output. To test orchestrator, fixture manager-agent-vs-handoff-control-model-c71 contains both an allowed state and a rejected state; rejection must occur before any change attributed to policy. Operations then observes the transition between policy and manager agent, while security checks that Agent.as_tool receives neither implicit authority nor unnecessary data.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c72 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. If the Agent.as_tool verification fails, rollback restores the configuration around handoff, replays manager-agent-vs-handoff-control-model-c72, and compares the new state with the control evidence from orchestrator. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to policy, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by manager agent and handoff: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c72 is labeled as a limitation or inference, never promoted to fact.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c73 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns policy into a reviewable decision point with a named input and a retained output. To test manager agent, fixture manager-agent-vs-handoff-control-model-c73 contains both an allowed state and a rejected state; rejection must occur before any change attributed to Agent.as_tool. Operations then observes the transition between Agent.as_tool and handoff, while security checks that orchestrator receives neither implicit authority nor unnecessary data.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c74 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. If the orchestrator verification fails, rollback restores the configuration around policy, replays manager-agent-vs-handoff-control-model-c74, and compares the new state with the control evidence from manager agent. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to Agent.as_tool, a concrete condition, and evidence instead of a generic assurance. The conclusion stays bounded by handoff and policy: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c74 is labeled as a limitation or inference, never promoted to fact.
Evidence point: OWASP documents that oWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. This source anchors production decision criteria but does not replace local verification. [S7]Controls that remain after launch
A robust implementation separates what the model proposes from what the application authorizes and verifies.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c81 starts at orchestrator and treats policy as an explicit boundary rather than an implicit assumption. The first control requires manager agent to emit an observable result before Agent.as_tool can trigger the intended effect around handoff. The conclusion stays bounded by manager agent and handoff: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c81 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns orchestrator into a reviewable decision point with a named input and a retained output. To test policy, fixture manager-agent-vs-handoff-control-model-c81 contains both an allowed state and a rejected state; rejection must occur before any change attributed to manager agent.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c82 starts at policy and treats manager agent as an explicit boundary rather than an implicit assumption. The first control requires Agent.as_tool to emit an observable result before handoff can trigger the intended effect around orchestrator. Operations then observes the transition between Agent.as_tool and handoff, while security checks that orchestrator receives neither implicit authority nor unnecessary data. If the handoff verification fails, rollback restores the configuration around orchestrator, replays manager-agent-vs-handoff-control-model-c82, and compares the new state with the control evidence from policy. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to manager agent, a concrete condition, and evidence instead of a generic assurance.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c83 starts at manager agent and treats Agent.as_tool as an explicit boundary rather than an implicit assumption. The first control requires handoff to emit an observable result before orchestrator can trigger the intended effect around policy. The conclusion stays bounded by handoff and policy: anything not demonstrated by scenario manager-agent-vs-handoff-control-model-c83 is labeled as a limitation or inference, never promoted to fact. That sequence serves this concrete job: Choose centralized orchestration or specialist ownership based on accountability, synthesis needs, latency and policy boundaries. It turns manager agent into a reviewable decision point with a named input and a retained output. To test Agent.as_tool, fixture manager-agent-vs-handoff-control-model-c83 contains both an allowed state and a rejected state; rejection must occur before any change attributed to handoff.
In “Manager agent or handoff? A decision model for multi-agent control”, scenario manager-agent-vs-handoff-control-model-c84 starts at Agent.as_tool and treats handoff as an explicit boundary rather than an implicit assumption. The first control requires orchestrator to emit an observable result before policy can trigger the intended effect around manager agent. Operations then observes the transition between orchestrator and policy, while security checks that manager agent receives neither implicit authority nor unnecessary data. If the policy verification fails, rollback restores the configuration around manager agent, replays manager-agent-vs-handoff-control-model-c84, and compares the new state with the control evidence from Agent.as_tool. This detail makes “Manager agent or handoff? A decision model for multi-agent control” reviewable because each operational statement points to handoff, a concrete condition, and evidence instead of a generic assurance.
Evidence point: OWASP documents that the 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. This source anchors controls that remain after launch but does not replace local verification. [S8]Operational checklist
- The control around manager agent has an input, a rule, a rejection behavior, and evidence.
- The control around Agent.as_tool has an input, a rule, a rejection behavior, and evidence.
- The control around handoff has an input, a rule, a rejection behavior, and evidence.
- The control around orchestrator has an input, a rule, a rejection behavior, and evidence.
- The control around policy has an input, a rule, a rejection behavior, and evidence.
Sources and control points
- [S1] OpenAI Agents SDK — The Agents SDK is a higher-level runtime around model calls that manages tools, guardrails, handoffs, sessions and tracing. source
- [S2] Handoffs - OpenAI Agents SDK — Handoffs transfer the active conversation to a specialist agent and can filter or reshape the history passed to the destination. source
- [S3] Agent orchestration - OpenAI Agents SDK — Two common orchestration patterns are manager-controlled agents-as-tools and handoffs where a specialist becomes the active agent. source
- [S4] Policies - Kubernetes — Kubernetes policy objects include NetworkPolicies for traffic controls and admission mechanisms for validating or mutating API requests. source
- [S5] Artificial Intelligence Risk Management Framework: Generative AI Profile — NIST AI 600-1 is a generative-AI profile for integrating trustworthiness and risk actions across the AI lifecycle. source
- [S6] AI Risk Management Framework — NIST positions the AI RMF as a voluntary framework for managing AI risks and is revising it while adding profiles for specific settings. source
- [S7] OWASP Top 10 for Large Language Model Applications — OWASP identifies its 2026 LLM Top 10 as the current release for major security risks in LLM applications. source
- [S8] OWASP Top 10 for LLM Applications 2025 — The 2025 OWASP LLM list provides the prior baseline for risks observed as LLMs became embedded in more production applications. source
- [S9] Content-Security-Policy: trusted-types directive — The trusted-types CSP directive allowlists policy names and became broadly available across current browsers in 2026. source
- [S10] Content-Security-Policy: require-trusted-types-for directive — require-trusted-types-for can make DOM XSS sinks reject raw strings and accept trusted typed values instead. source


Comments
No published comment yet.
Sign in to comment